Required
Security
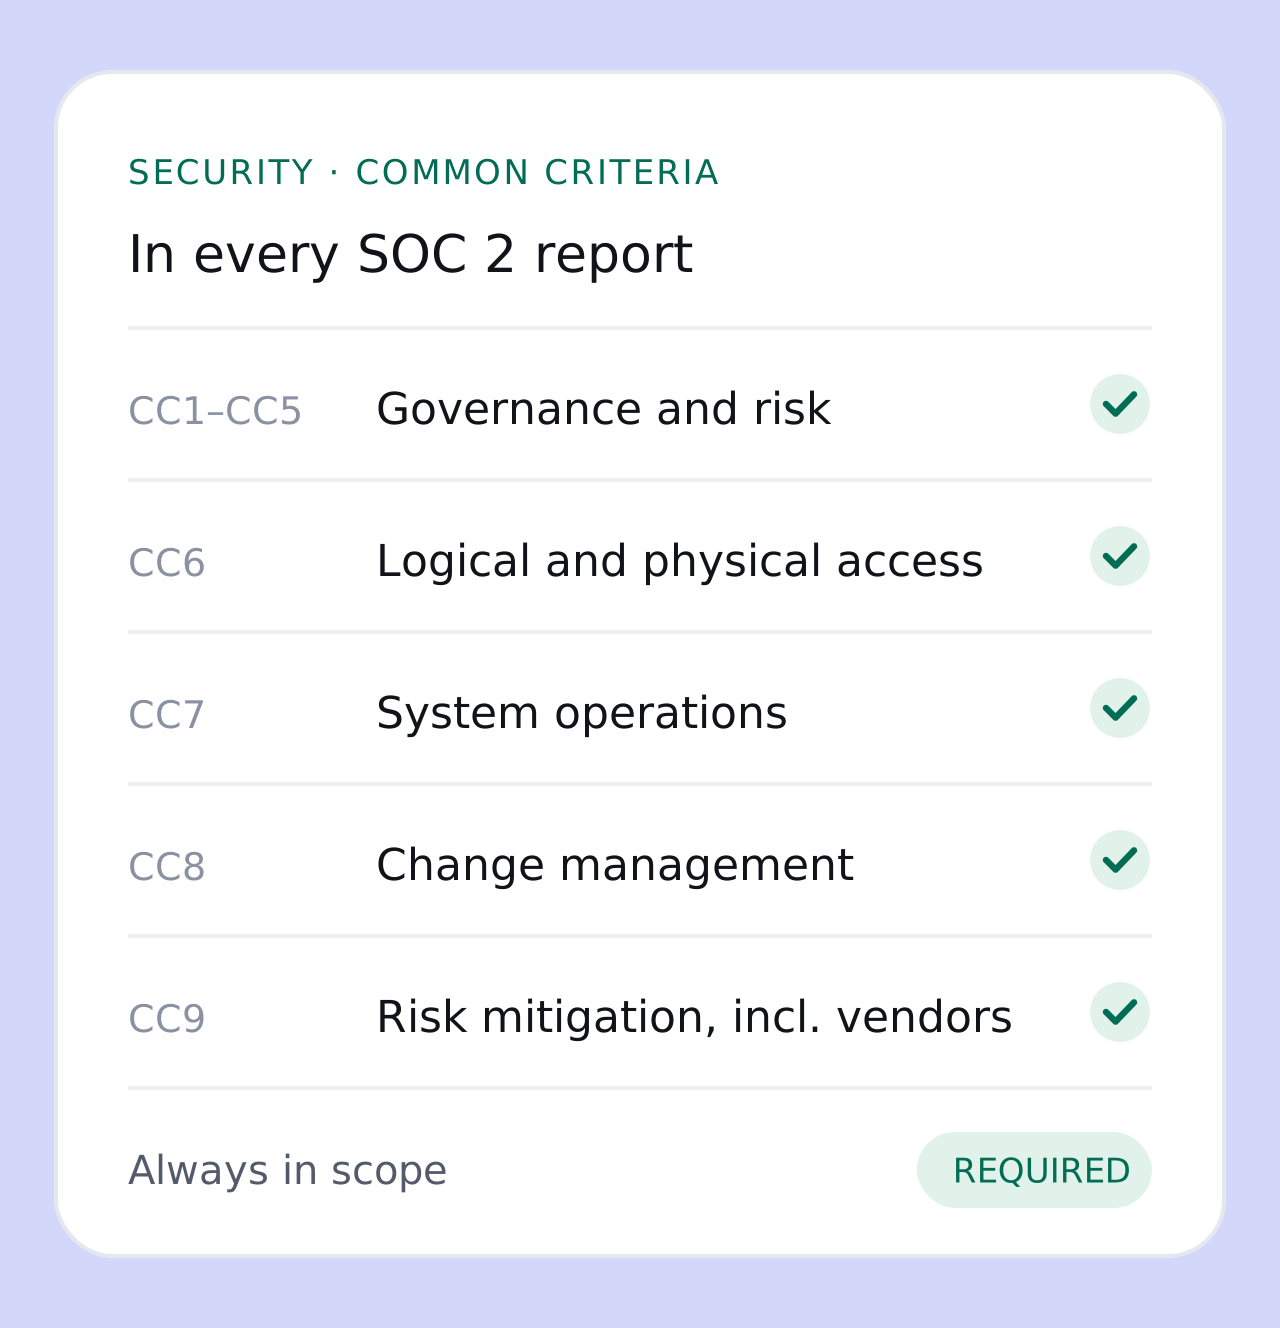
The common criteria, CC1 to CC9, cover governance, risk, access, operations and change. Every SOC 2 report includes them.
SOC 2 is a report, not a certificate. An independent CPA firm examines a company’s controls against the AICPA’s Trust Services Criteria and gives its opinion. Many of the cloud and SaaS suppliers you rely on hand one over instead of an ISO certificate.
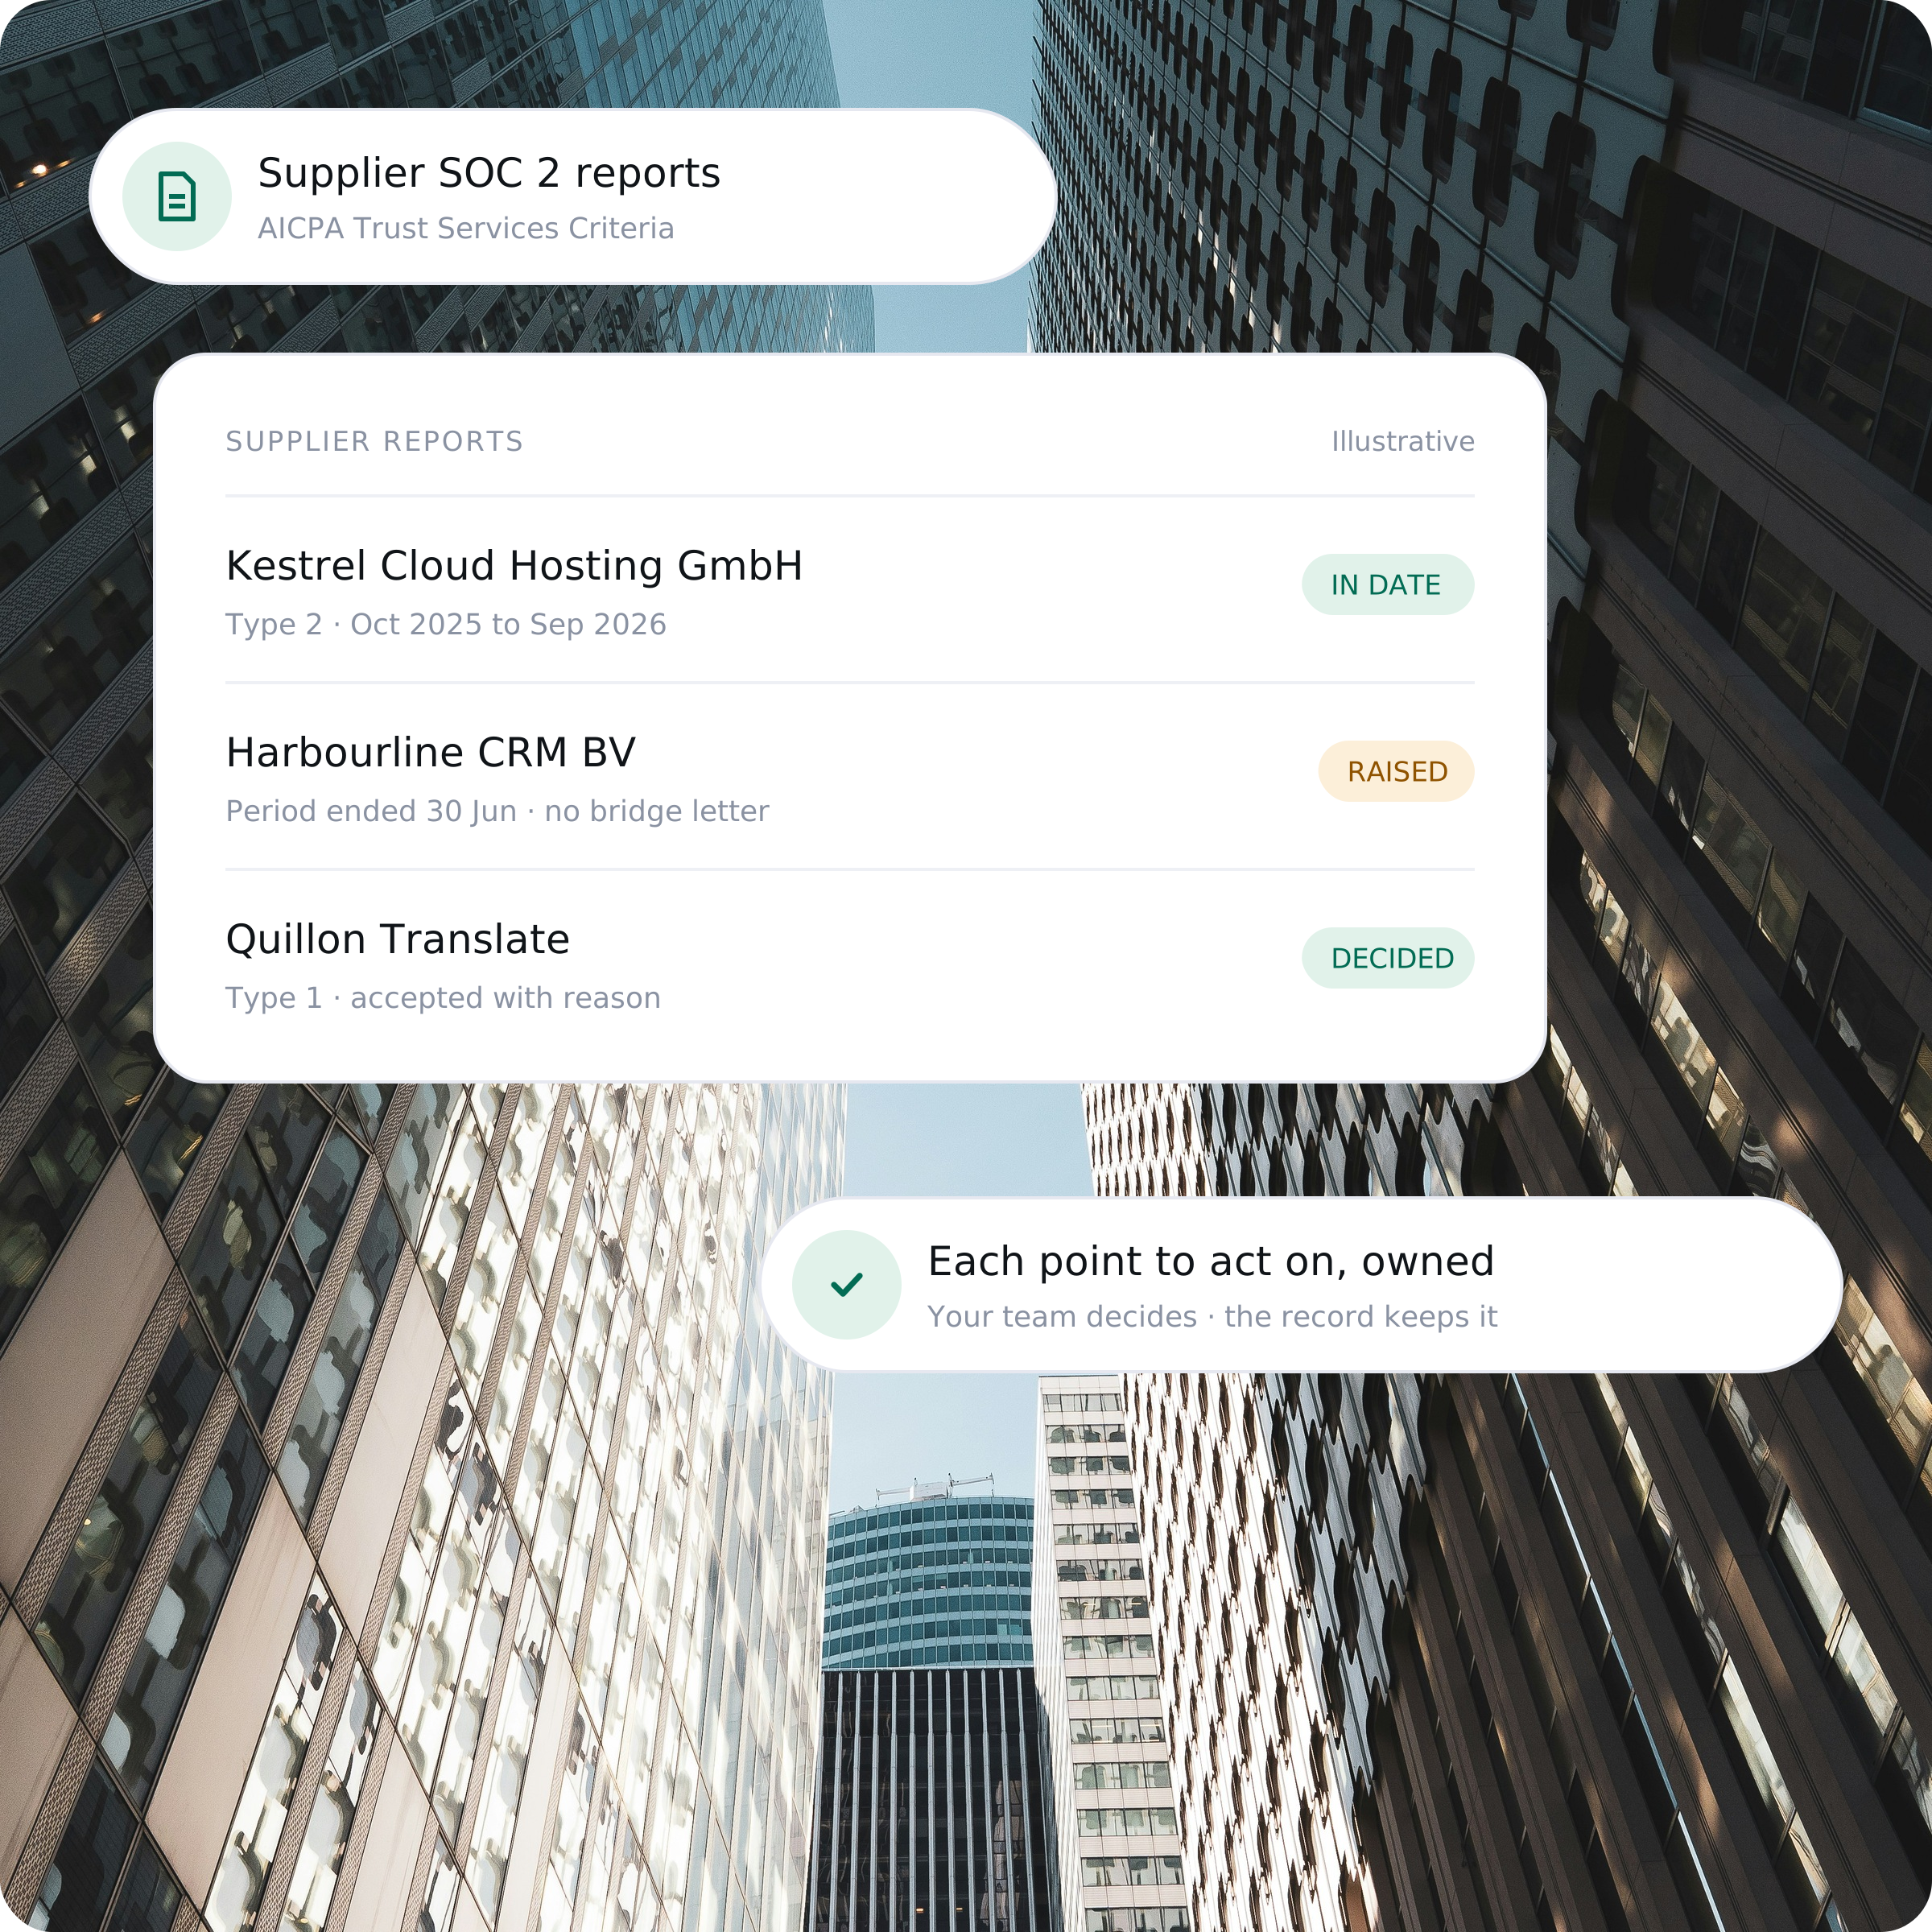
Montro keeps each supplier’s SOC 2 report with its entry, with the period it covers and the points your team needs to act on. When a report runs out of date, it comes back to your team for review.
Framework
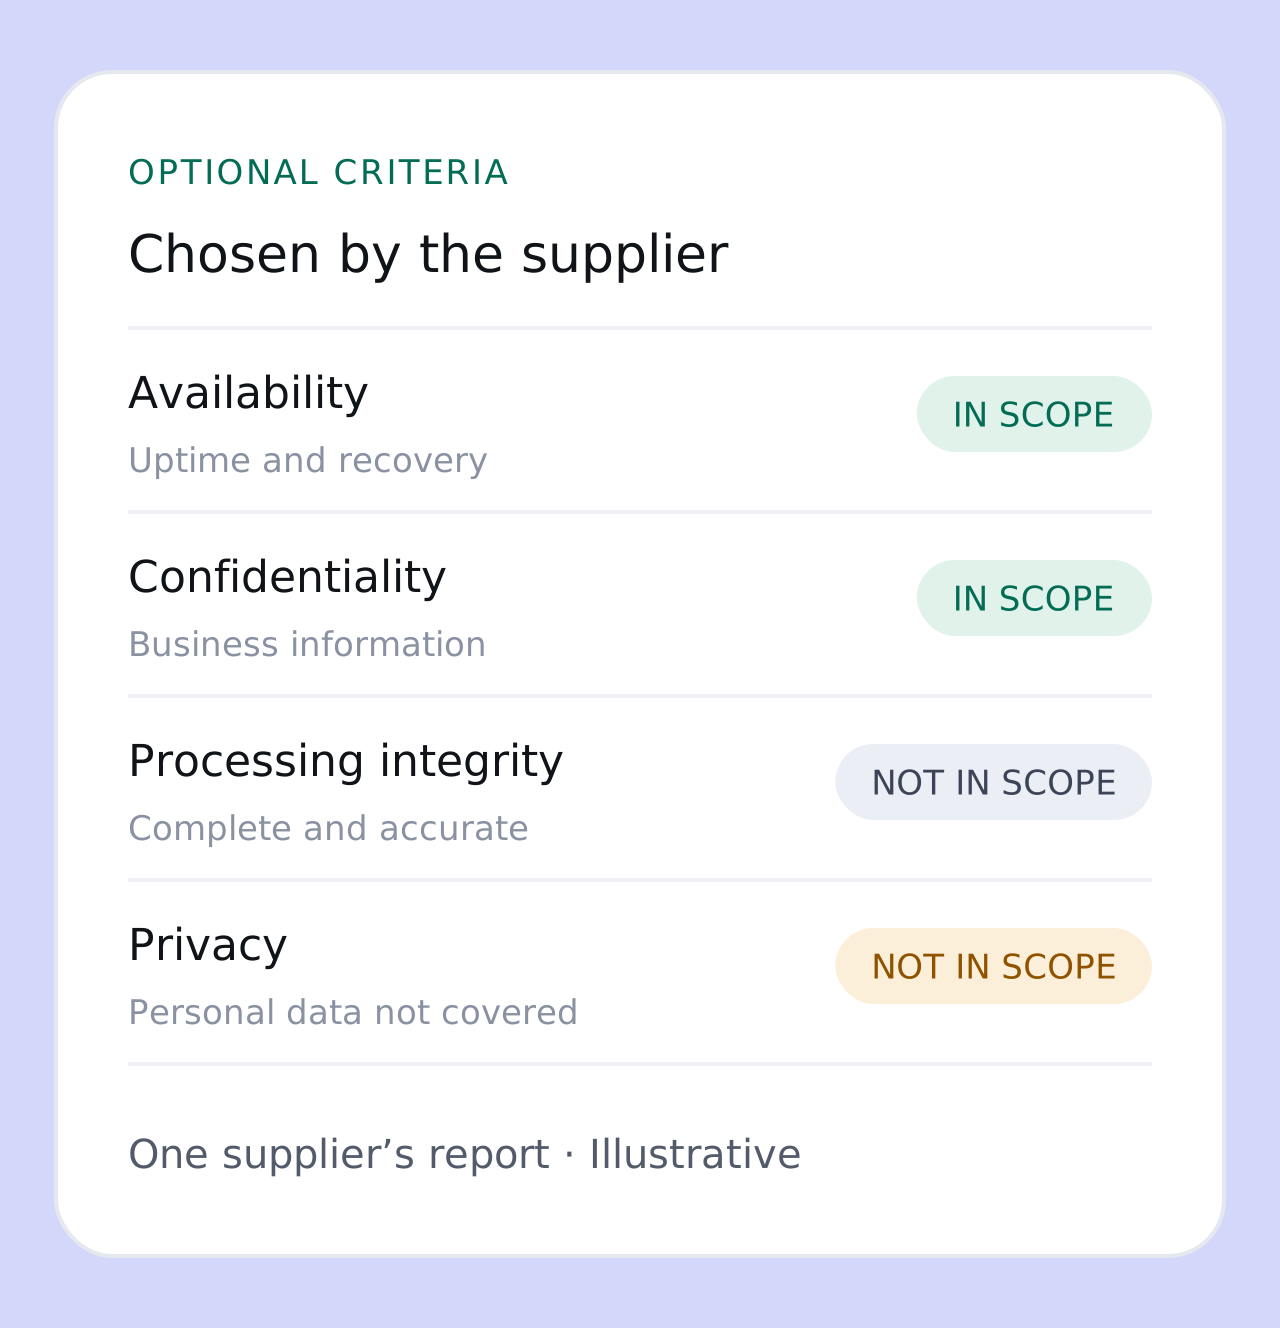
Five Trust Services Criteria set the scope. Security is always included, and the supplier chooses whether to add any of the other four.
Required
The common criteria, CC1 to CC9, cover governance, risk, access, operations and change. Every SOC 2 report includes them.
Optional
Added when the service calls for them. A report without the privacy criteria says nothing about how personal data is handled.
Suppliers
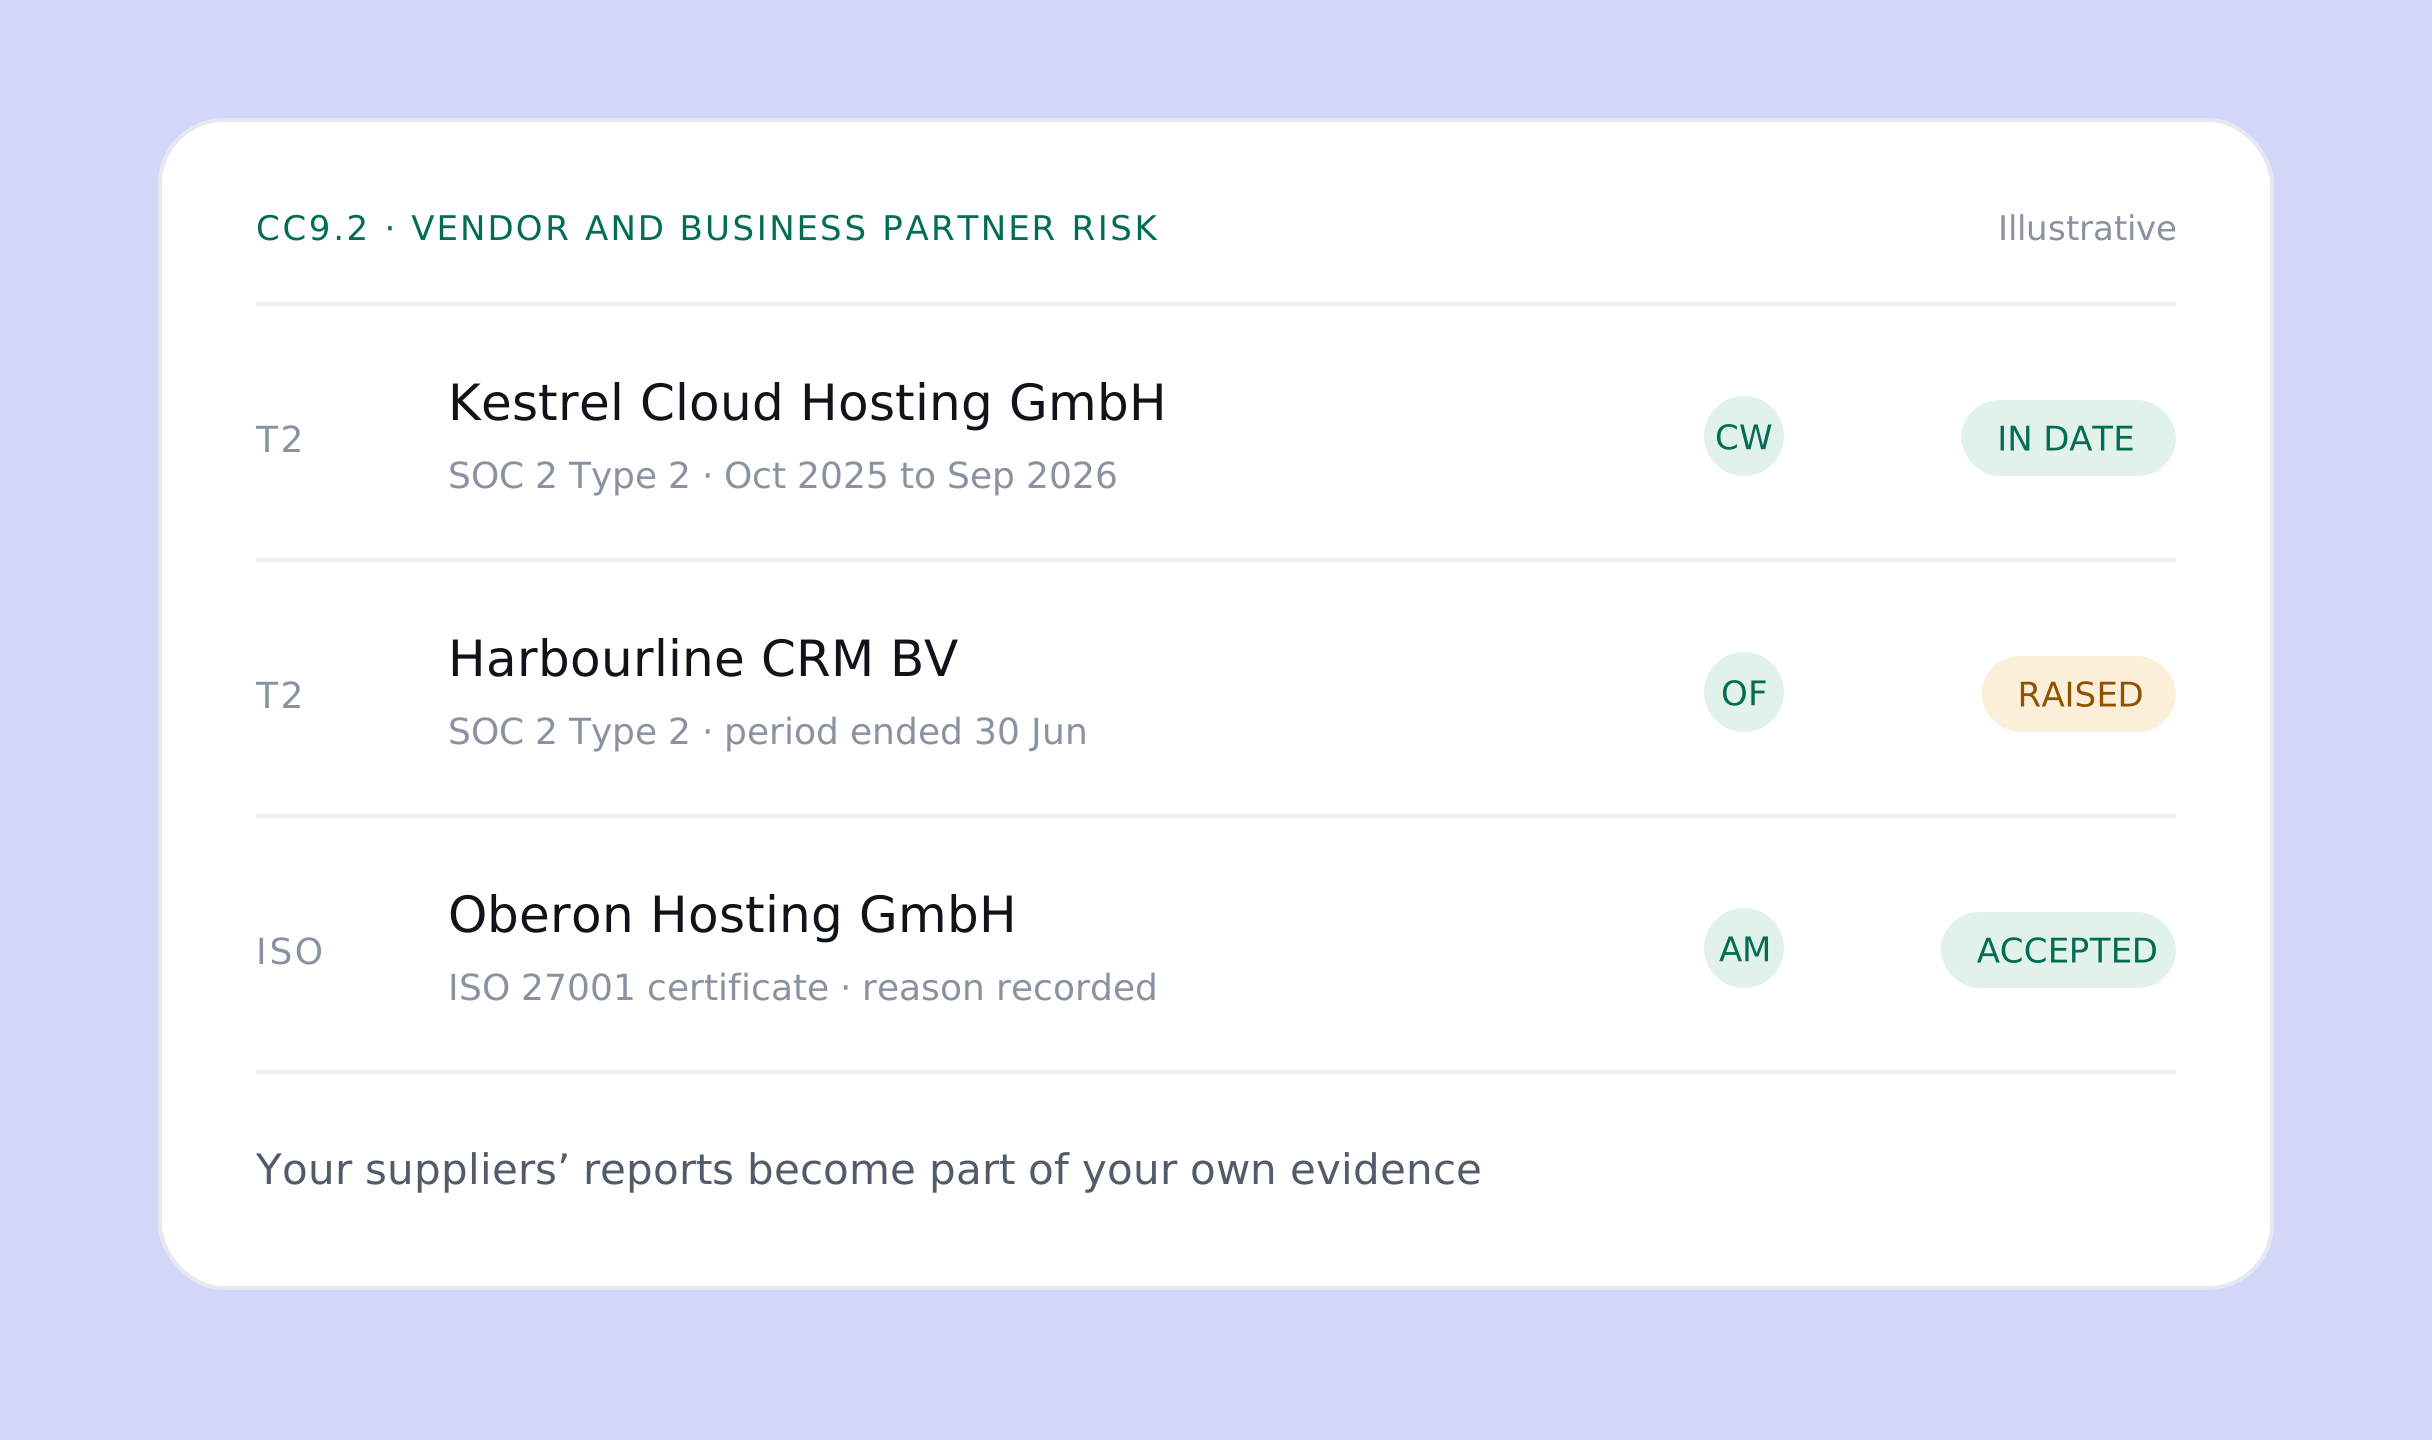
Criterion CC9.2 asks a company to assess and manage the risks from its own vendors. If you hold a SOC 2 report yourself, your suppliers’ reports become part of your evidence.
How Montro helps
Montro keeps the SOC 2 reports your suppliers send against their entries, and raises the changes that fall outside what those reports cover.
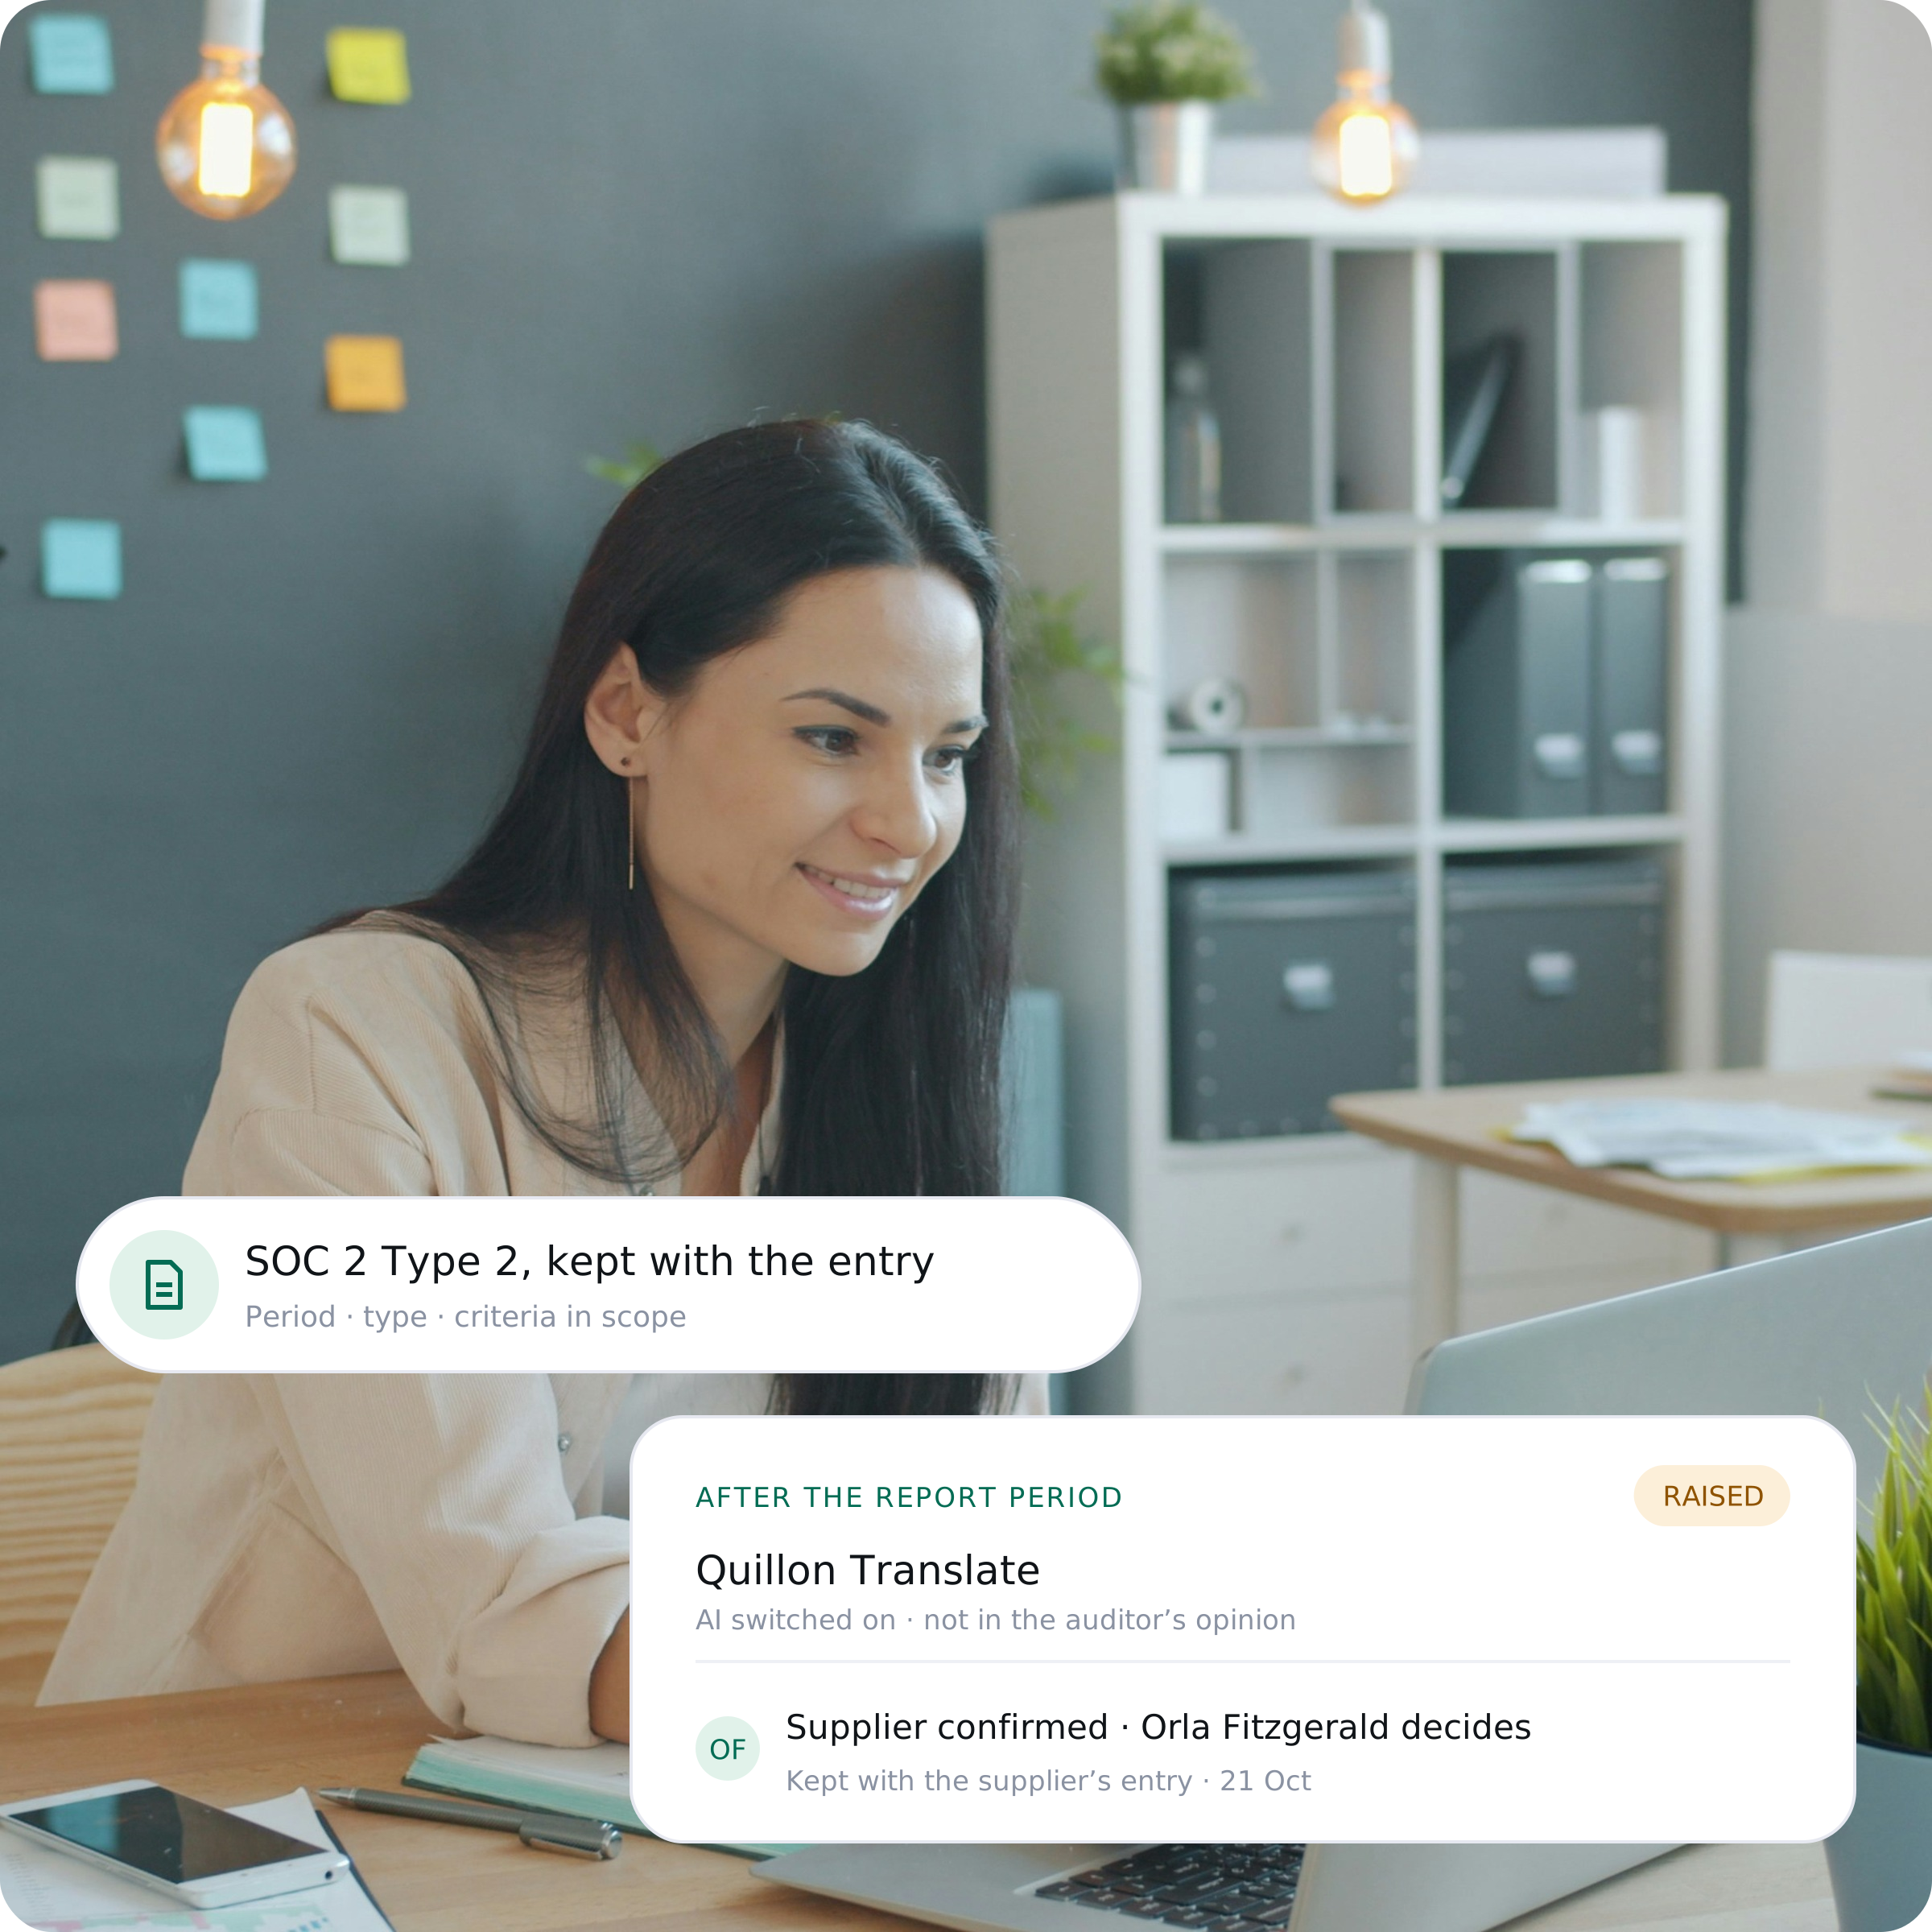
The report, its type, the period it covers and the criteria in scope sit with the supplier’s entry, ready when someone asks for them.
When a report’s period ends and no new report or bridge letter arrives, Montro raises it for your team to follow up.
A new sub-processor or AI switched on after the report period isn’t in the auditor’s opinion. Montro raises it, the supplier confirms, and your team decides.
What you get
A report is only useful once someone acts on what it says.
Your controls
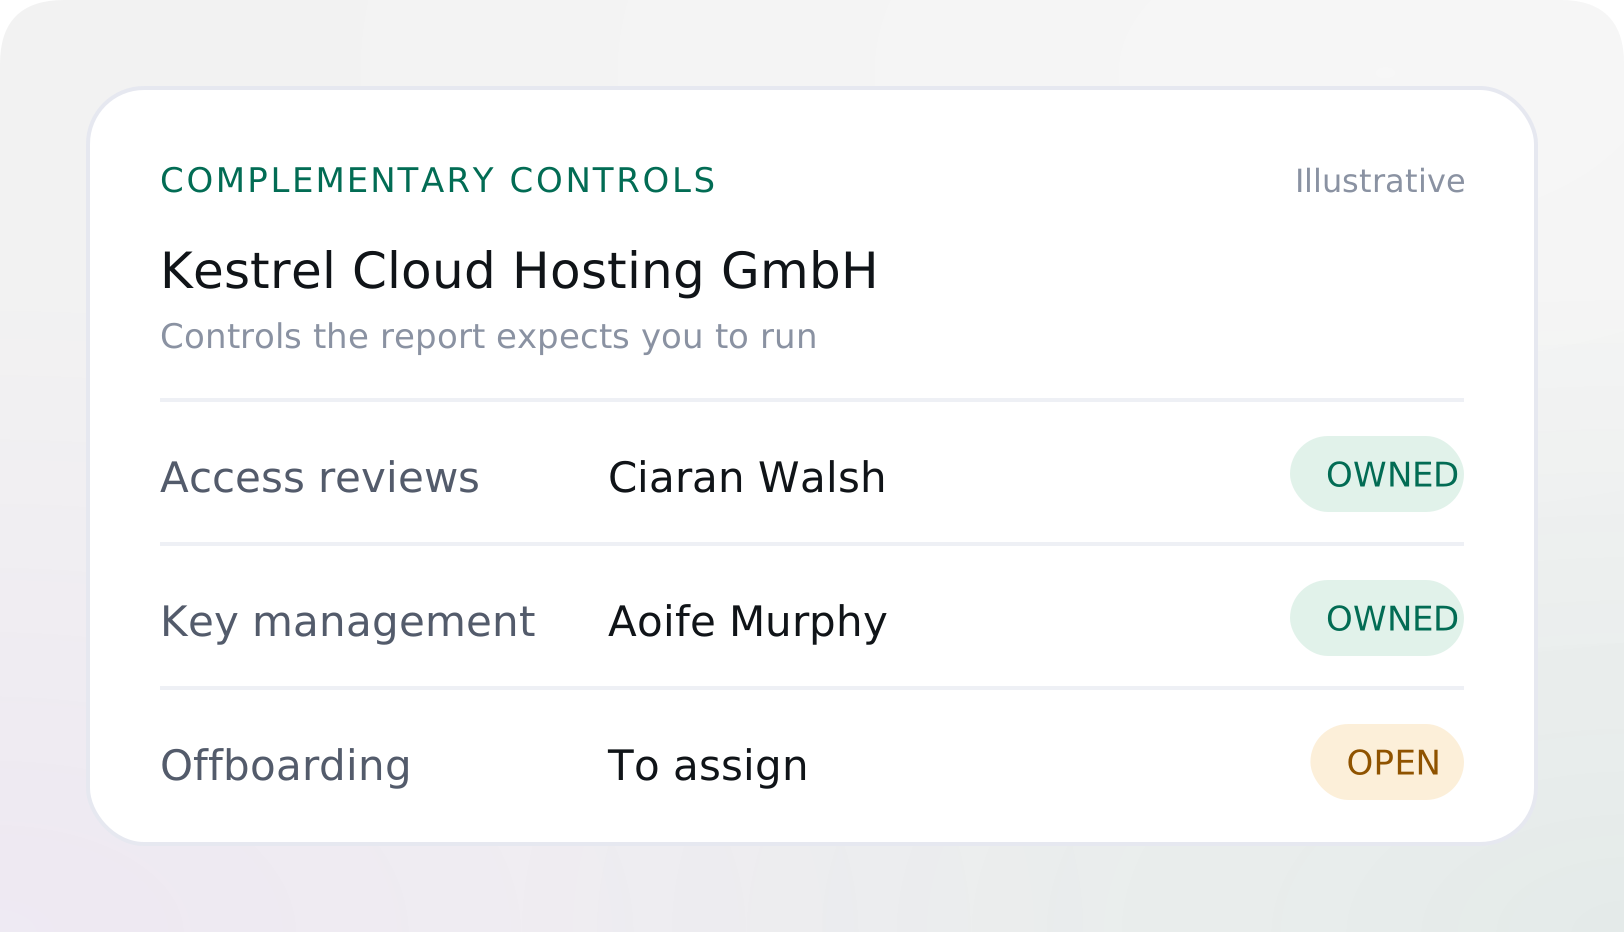
Reports list controls the customer is expected to run, such as reviewing who has access. Each one gets an owner on your side.
Exceptions
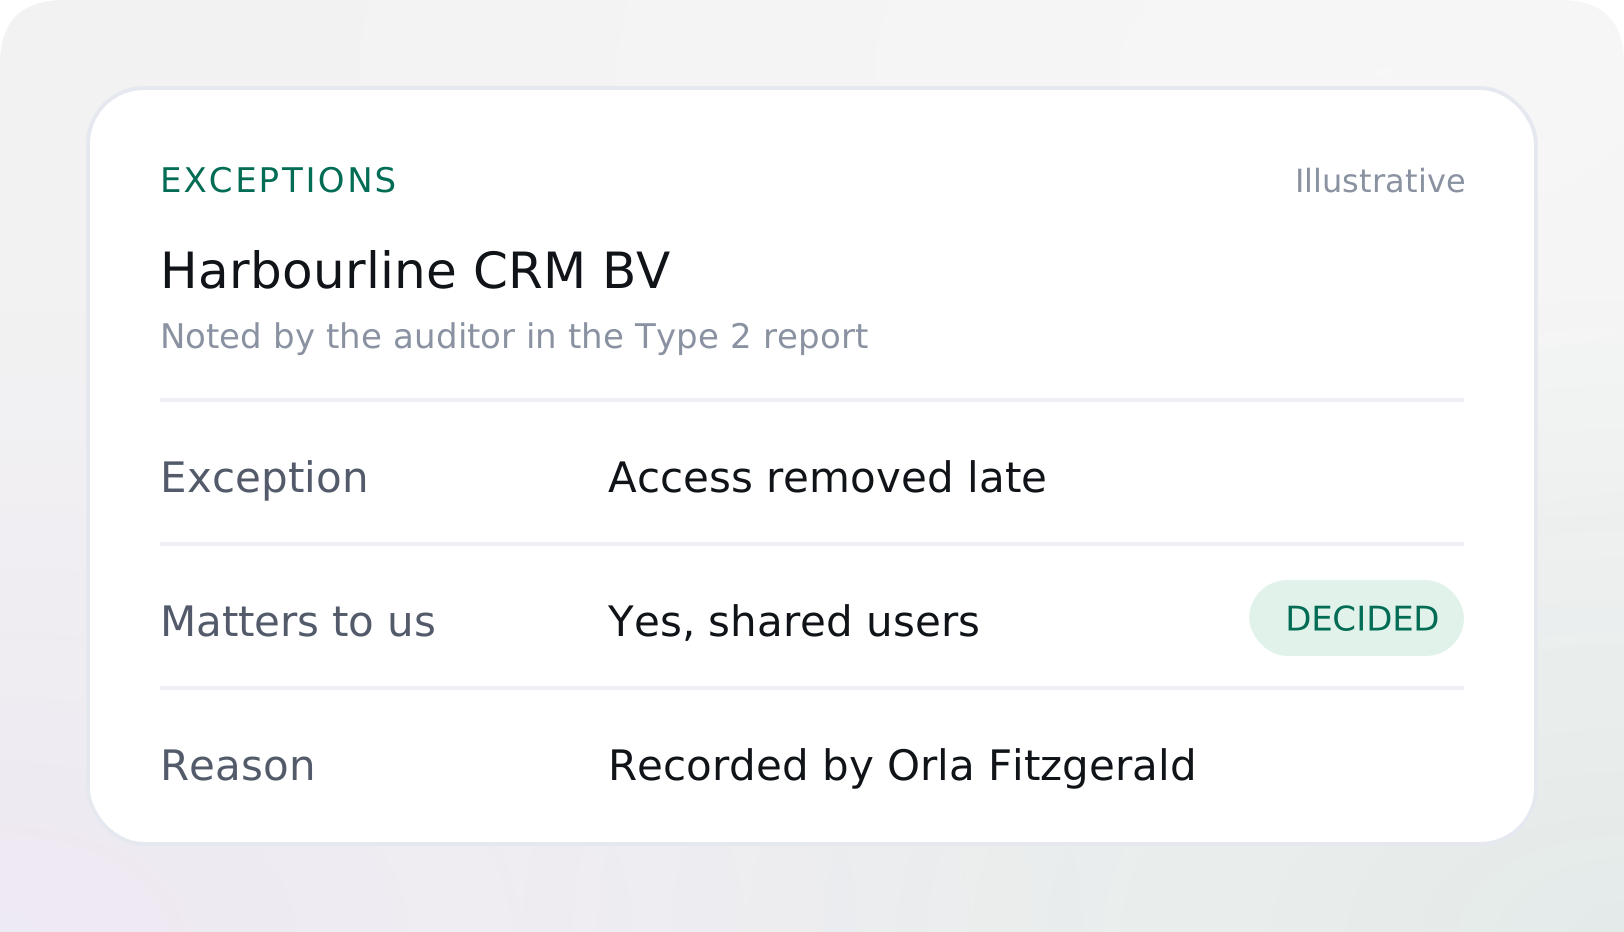
Where the auditor found a control didn’t work as described, your team records whether it matters to you and why.
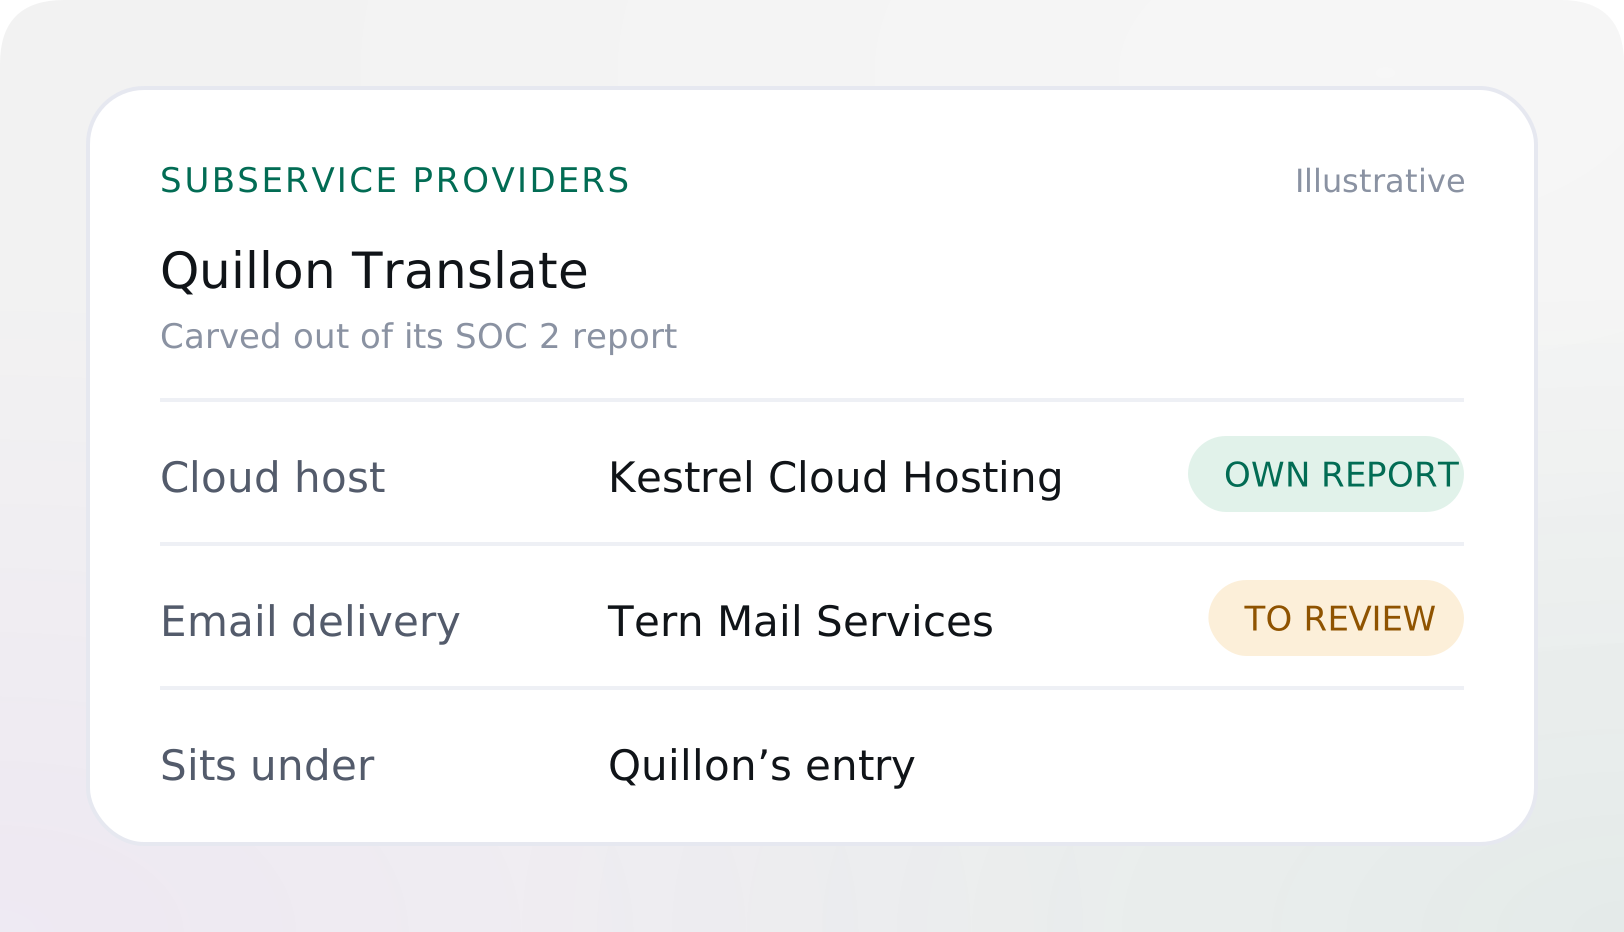
Subservice providers
Many reports leave out the supplier’s own providers, such as its cloud host. Those sit under the supplier’s entry, so you can see whose report covers what.
Type 1 and Type 2
A Type 1 report says controls were designed properly on a single date. A Type 2 report also tests whether they worked over a period, often six to twelve months, so it tells you far more about how a supplier operates day to day.
Montro records which type each supplier holds and the dates it covers. A Type 1 can be accepted for now with a reason, and when the Type 2 arrives the entry moves on with the earlier decision kept.
Questions about SOC 2 reports, and how Montro keeps them with your suppliers.
Keep reading
A supplier with a SOC 2 report often holds other evidence too, and your own obligations rarely stop at one framework.

For financial entities, a SOC 2 report supports the register of information but doesn’t replace it.
Read more
A report without the privacy criteria leaves processor questions for your record of processing.
Read more
The certificate many suppliers hold instead, and what its scope and dates tell you.
Read moreThird-party records are becoming decision logs. The firms that get this right will be the ones that can show who decided, on what evidence, and when.
A read-only connection, about an hour to set up, and a named person who can say yes to a decision.
Priced to scope — never per seat, never per supplier. Upgrade only when the evidence earns it.