Management system
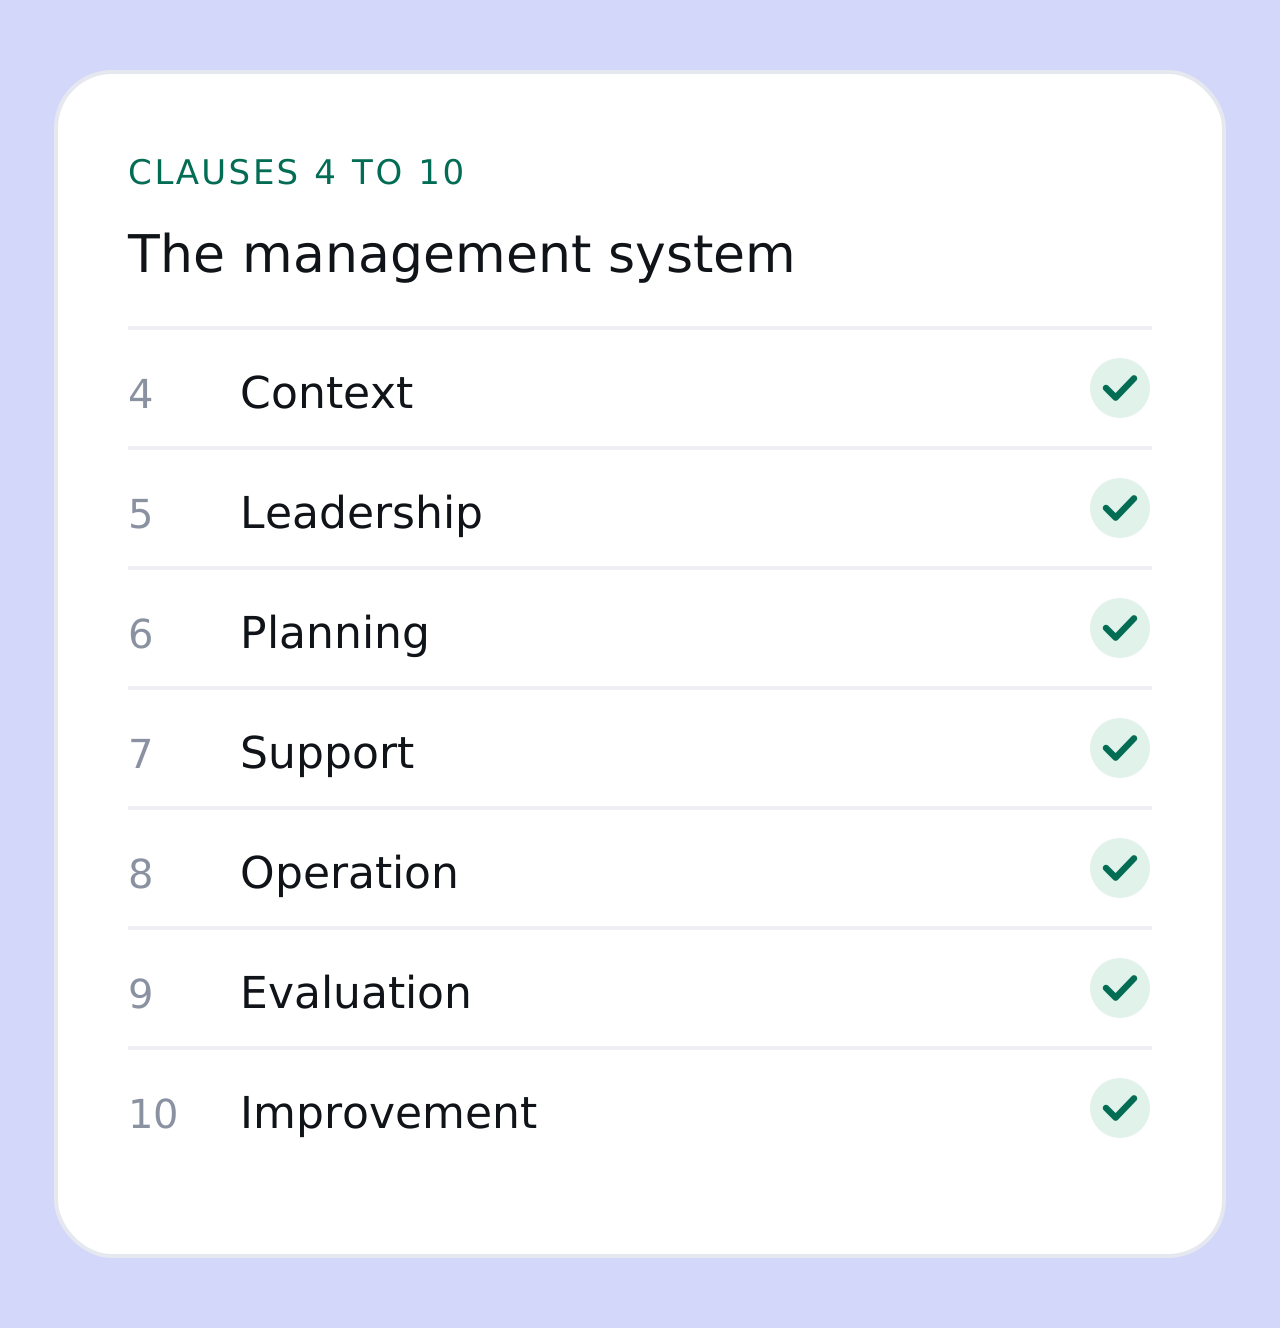
Clauses 4 to 10
Context, leadership, planning, support, operation, evaluation and improvement. Every certified organisation meets all seven
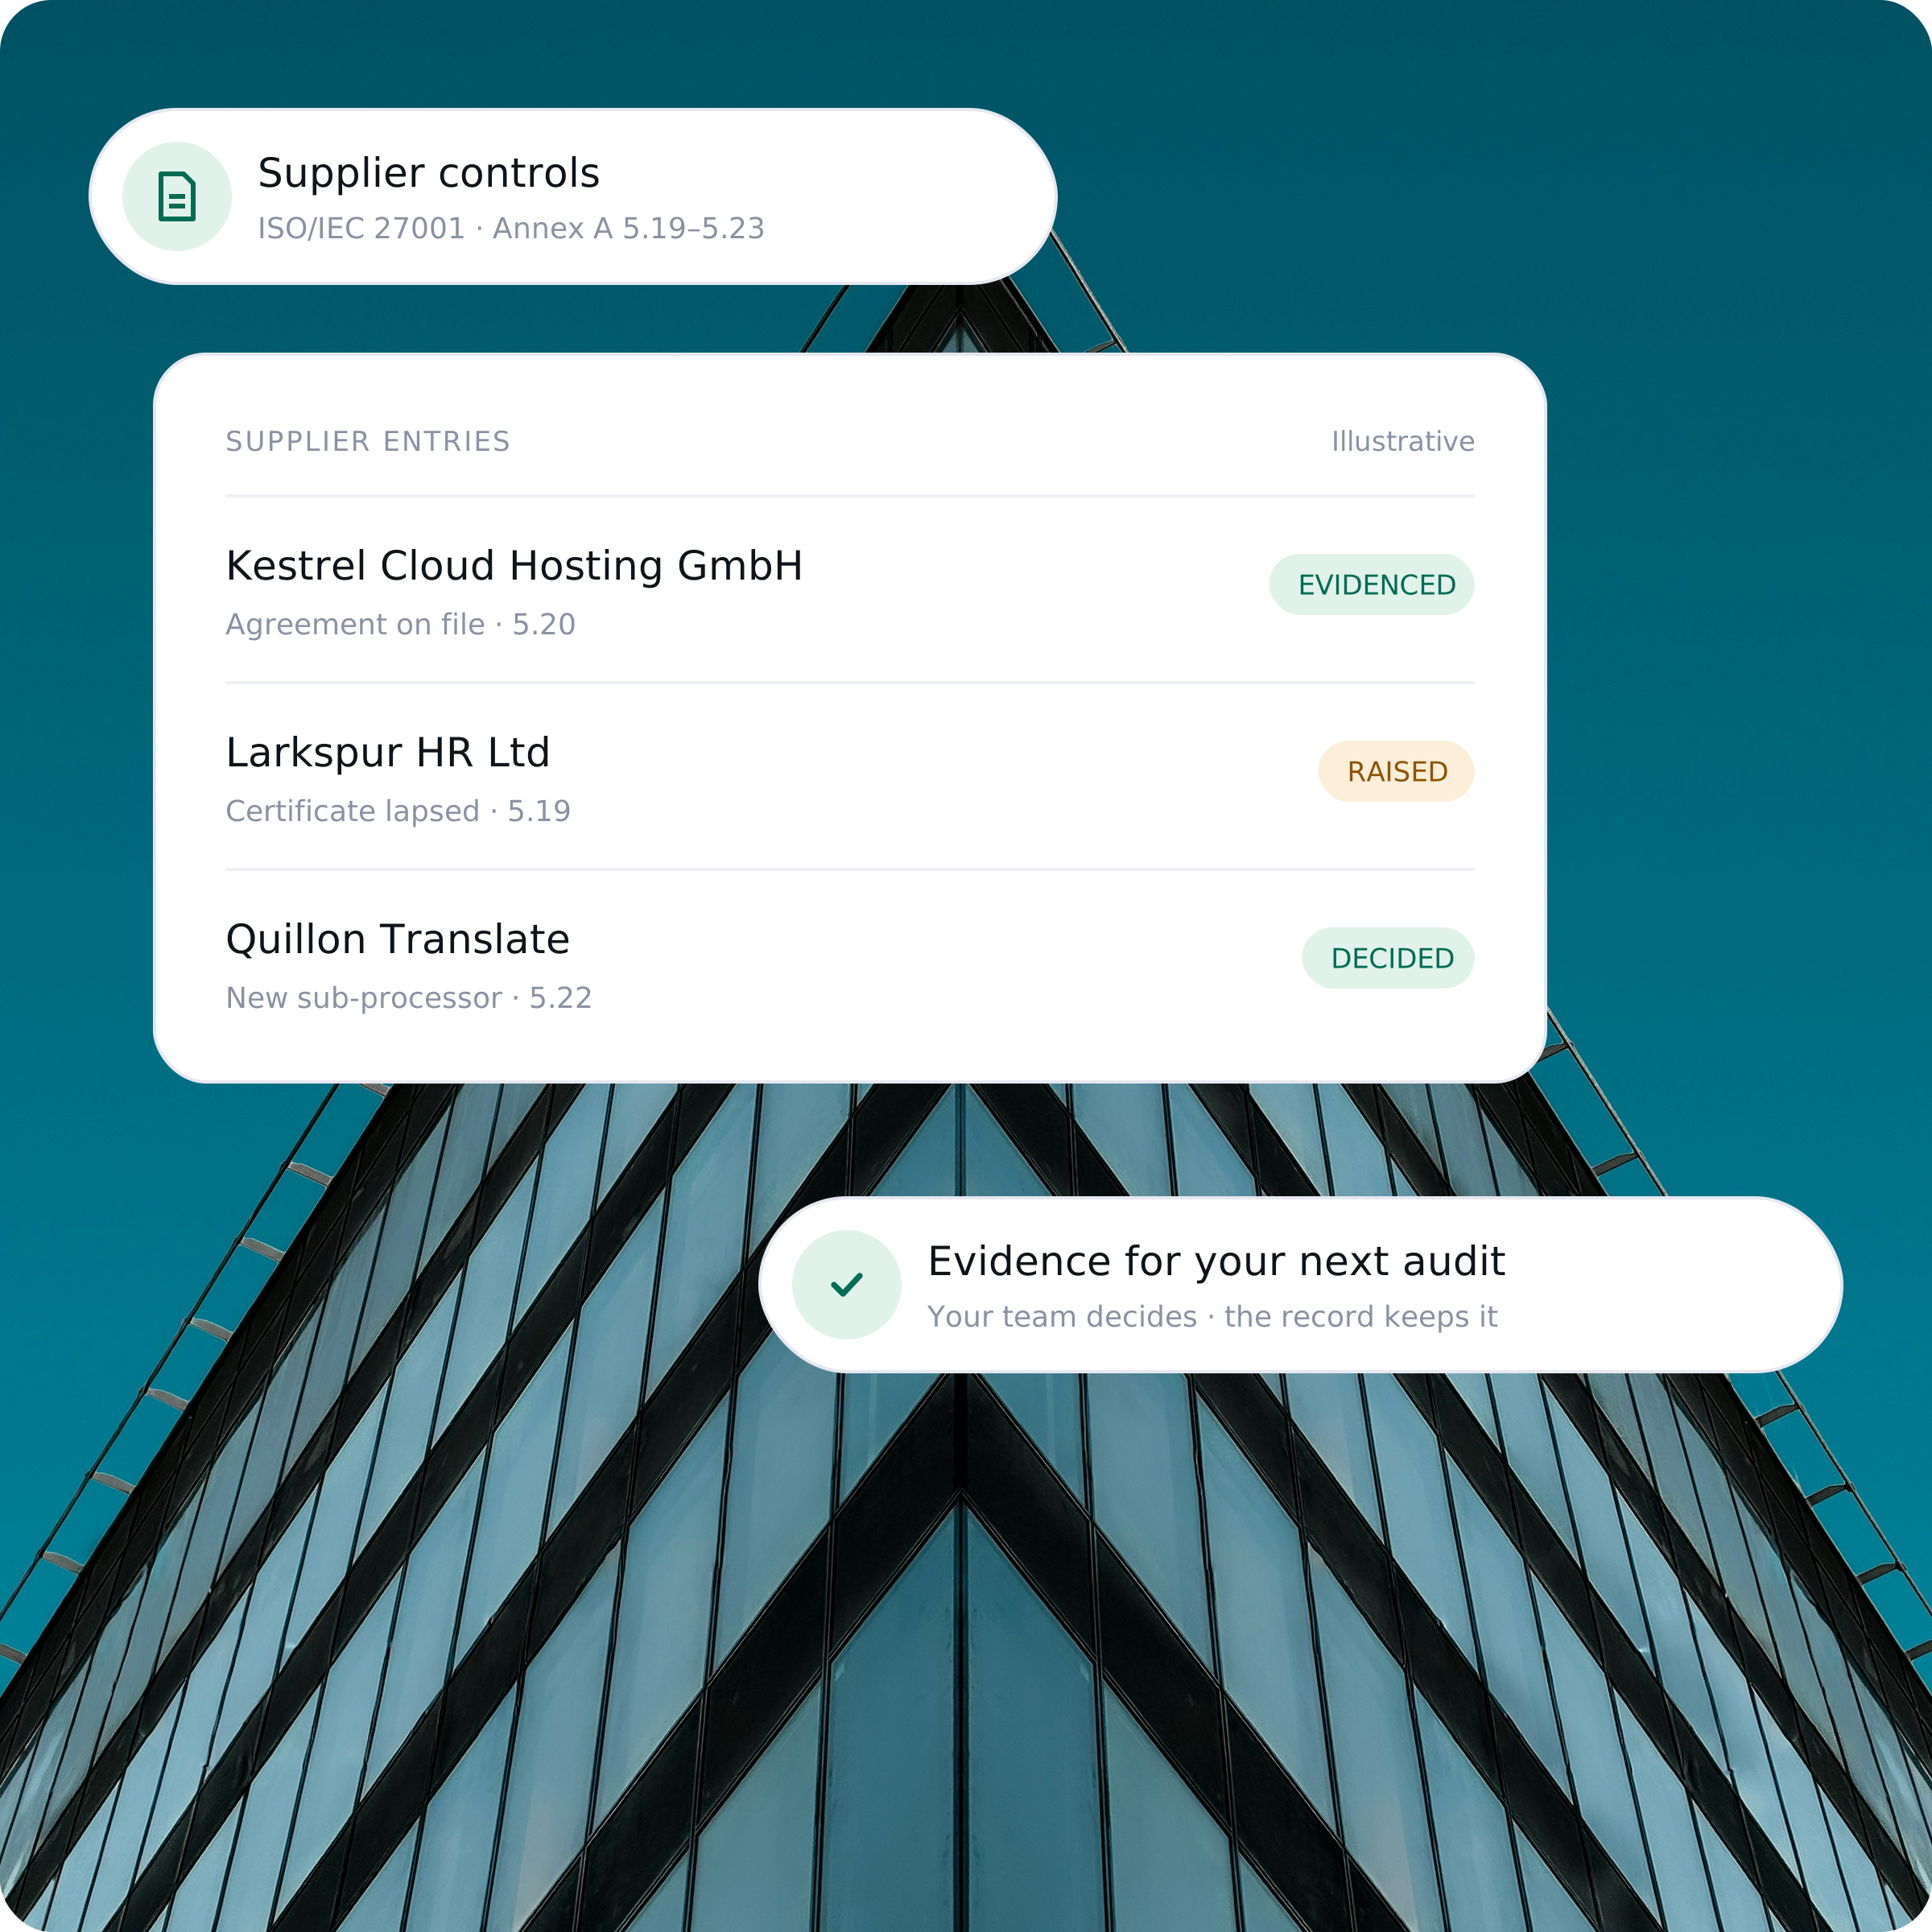
ISO/IEC 27001 is the international standard for an information security management system, certified by an independent body. Five of its Annex A controls, 5.19 to 5.23, cover suppliers: from security requirements and agreements to monitoring changes and using cloud services.
Montro keeps the supplier side of your ISMS current. A lapsed certificate or a new sub-processor is raised with its source and checked with the supplier, and your team’s decision stays with the entry as evidence for your next surveillance audit.
Framework
ISO 27001 has two parts. The clauses set out how the management system runs, and Annex A lists the controls you choose from, based on your own risk assessment.
Management system
Context, leadership, planning, support, operation, evaluation and improvement. Every certified organisation meets all seven
Controls
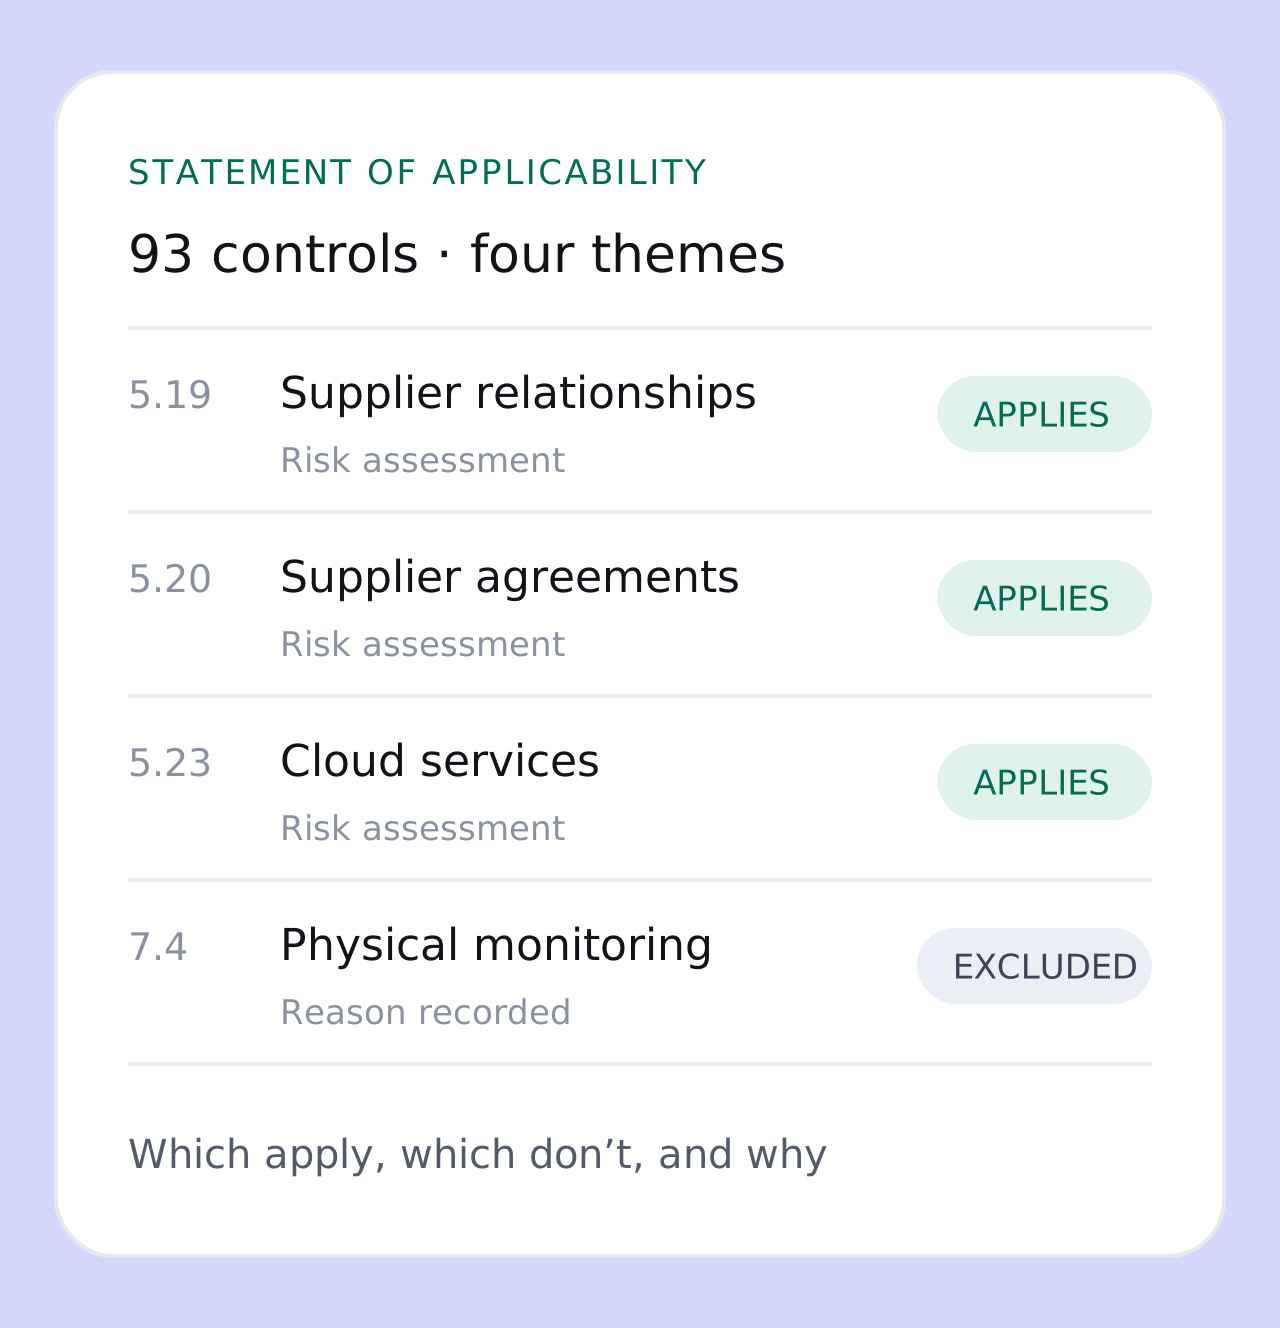
93 controls in four themes. Your Statement of Applicability records which apply to you, which don’t, and why.
Suppliers
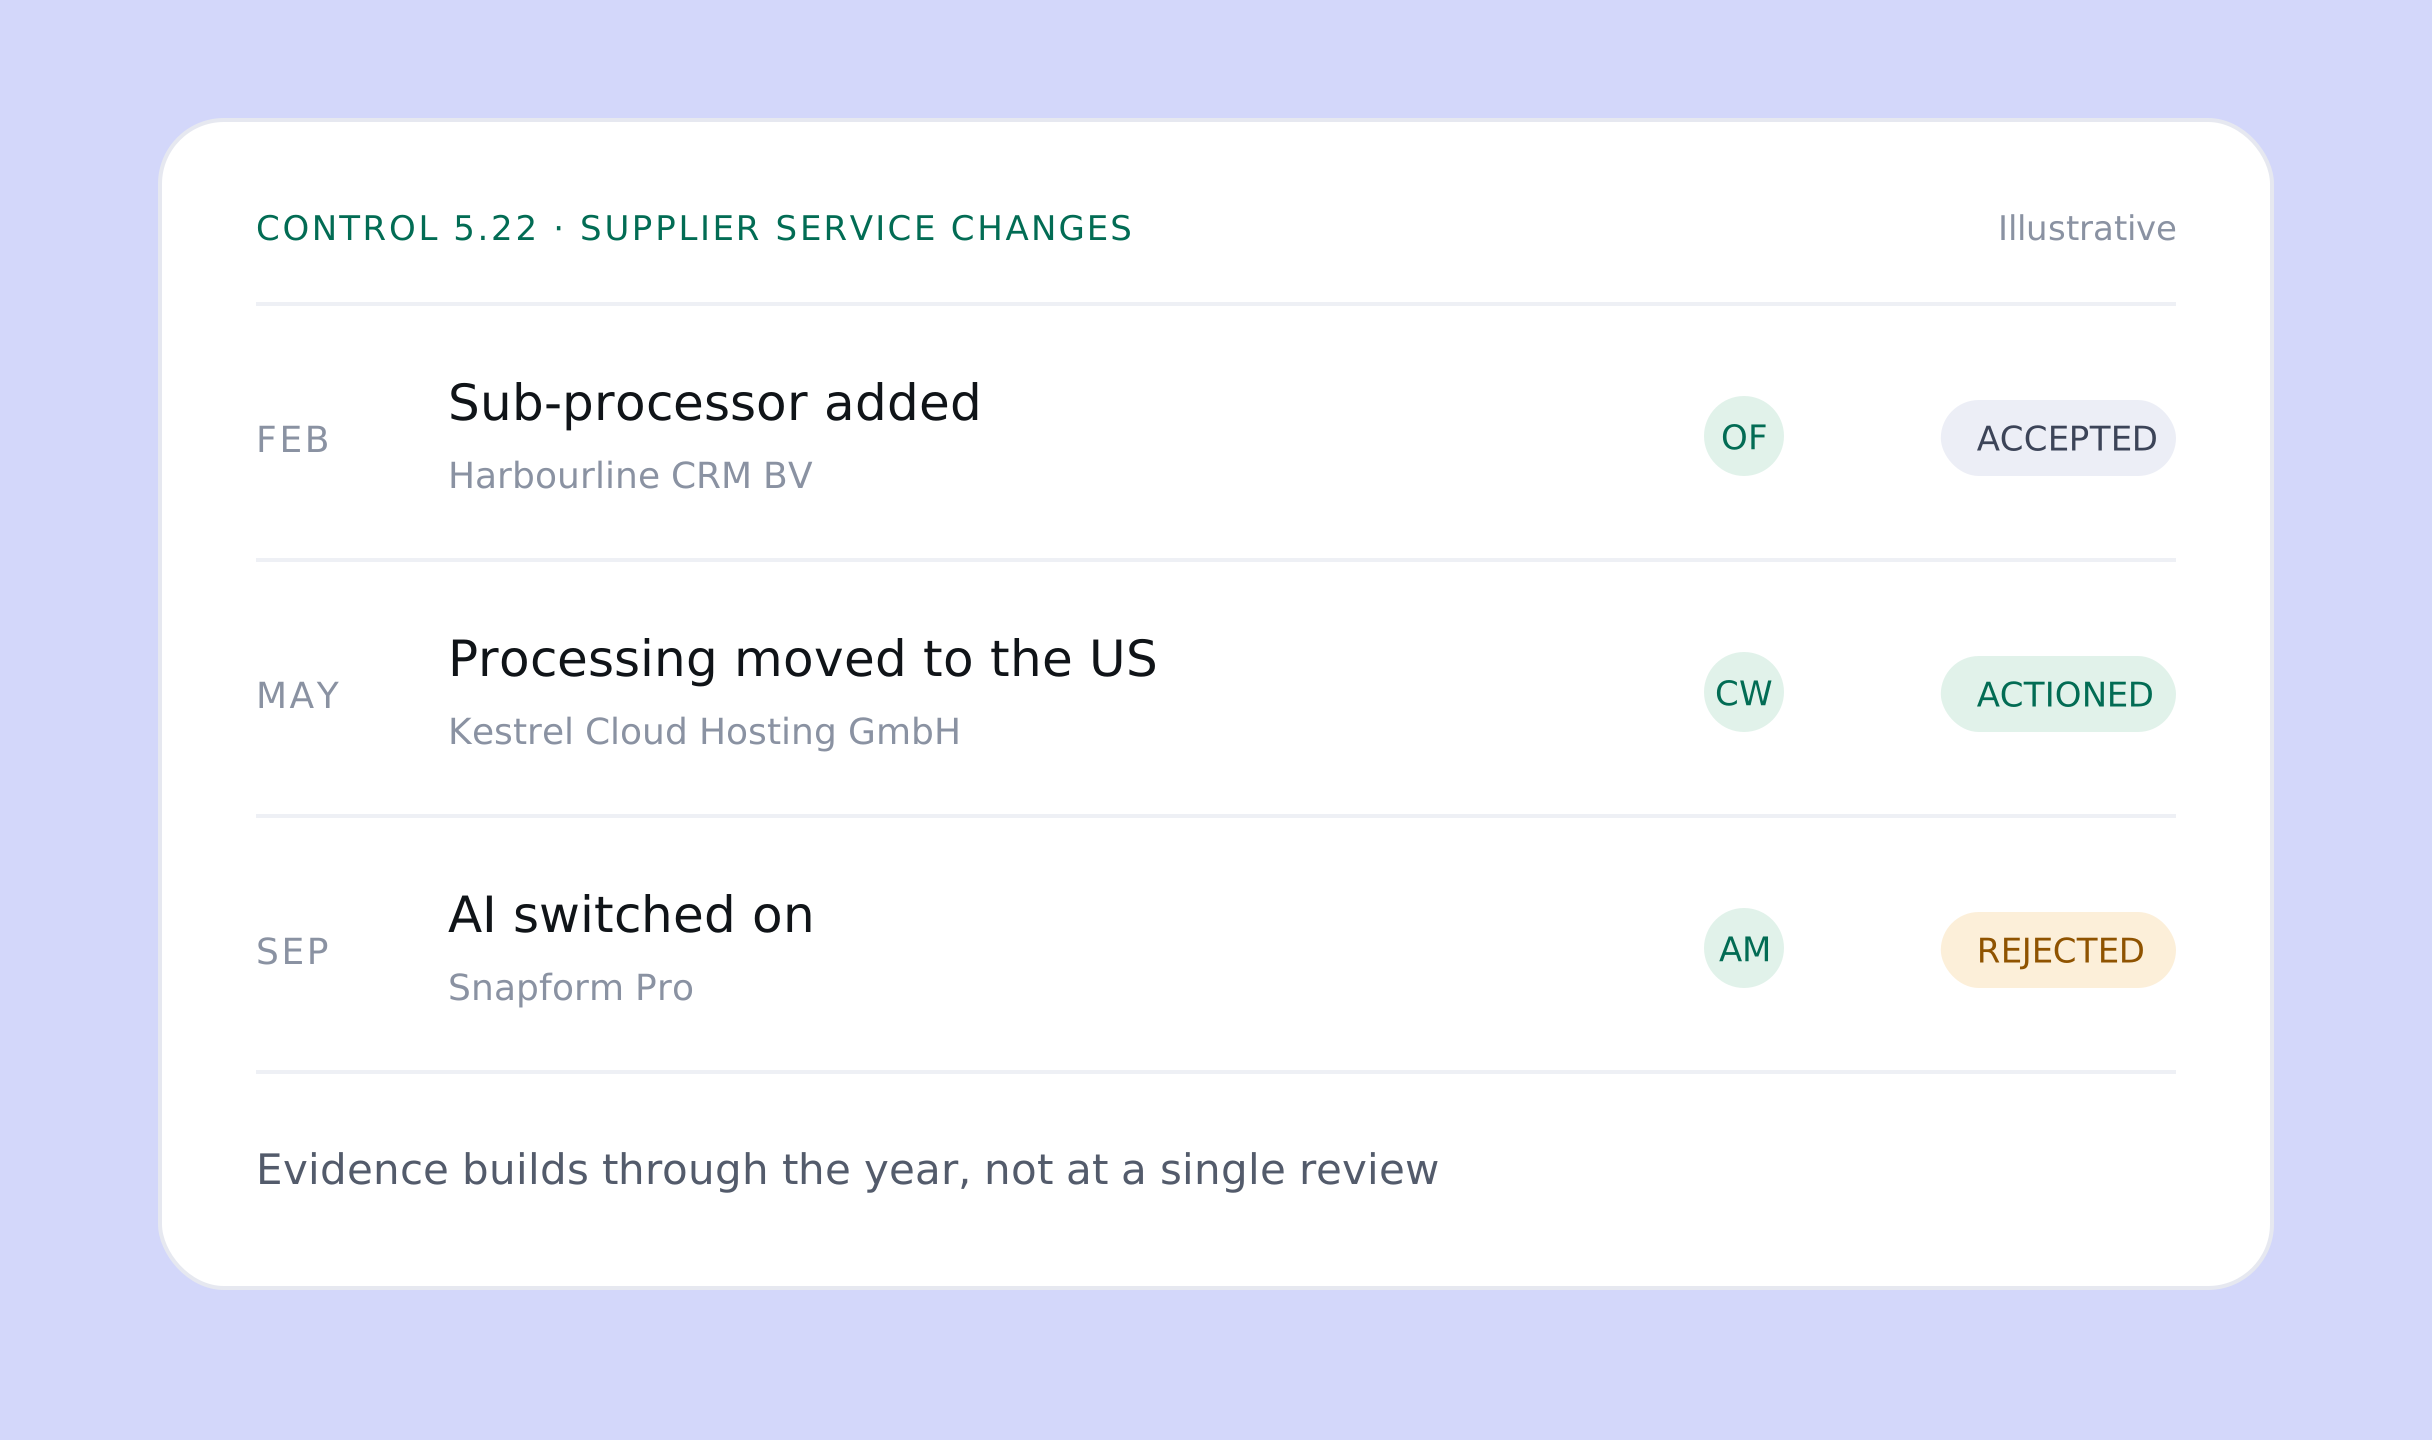
Control 5.22 asks you to monitor supplier services and manage changes to them, so evidence builds over the year rather than at a single review.
How Montro helps
Montro picks up supplier changes from your sign-in, finance and cloud accounts and from suppliers’ own published pages, and keeps the evidence your supplier controls rely on.
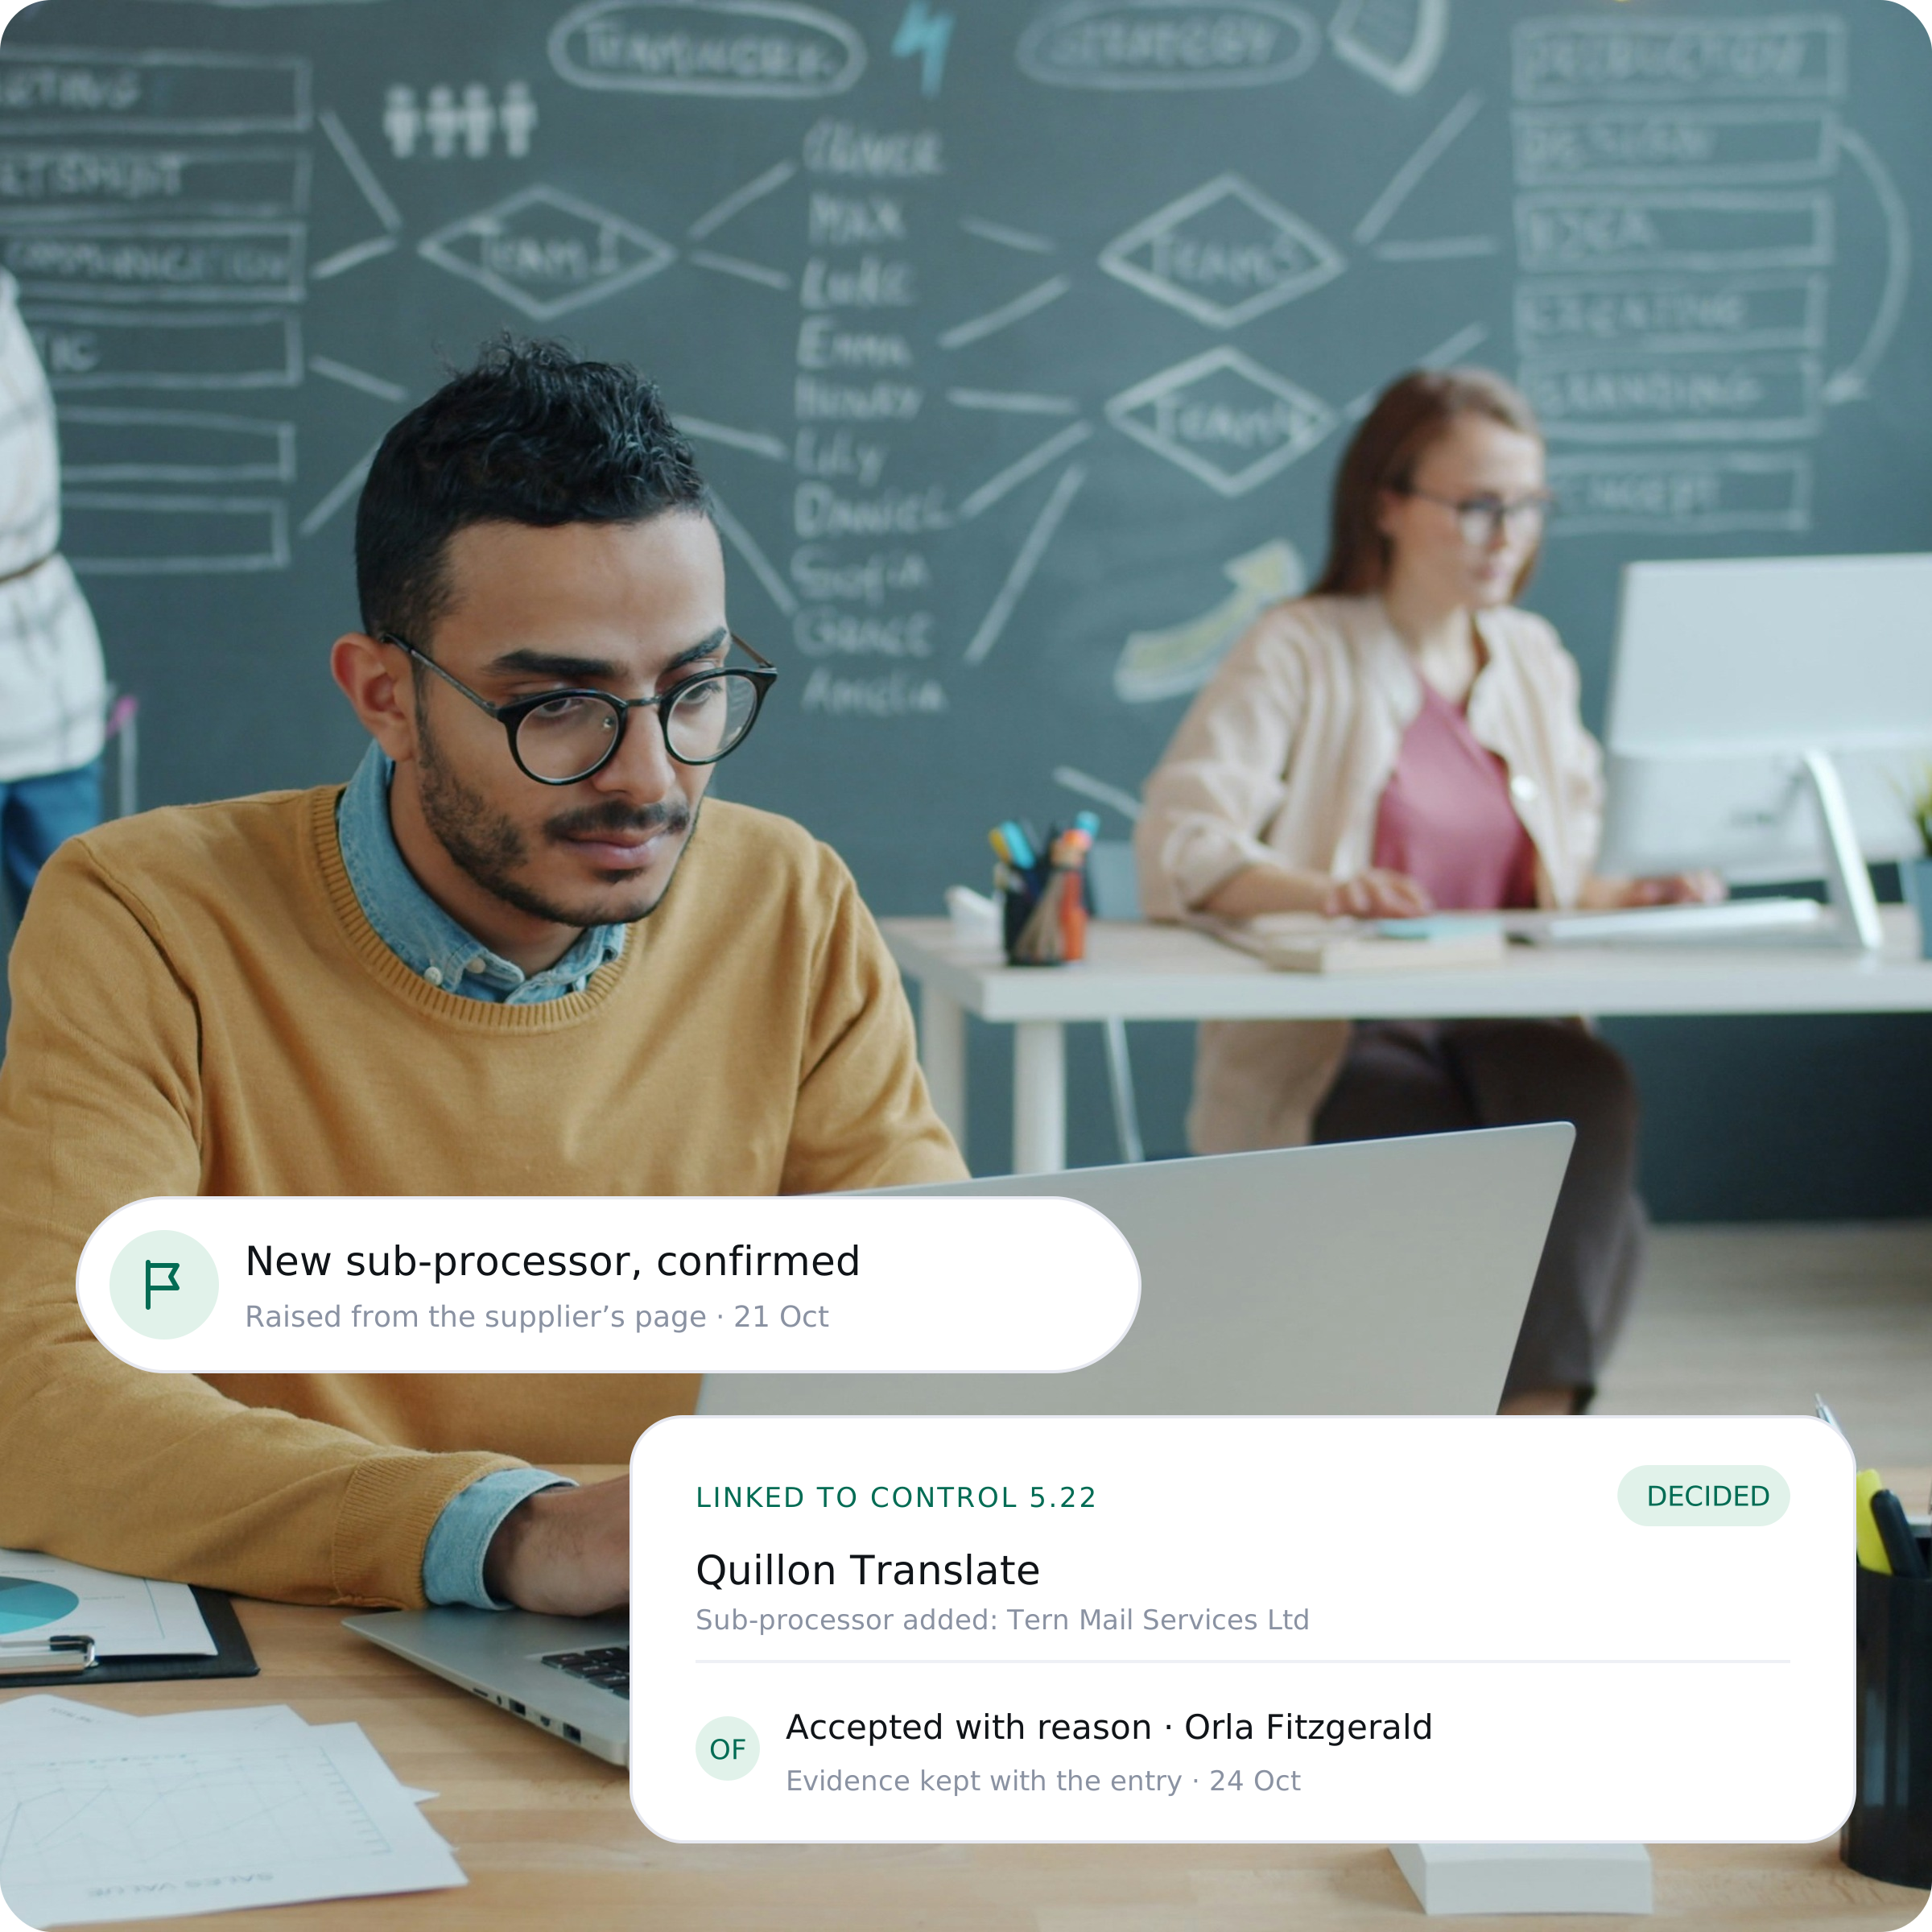
A new supplier arrives as a candidate. Your team records its security requirements and agreement before it enters the register, which is what controls 5.19 to 5.21 look for.
A new sub-processor, processing moved to another country or AI switched on is checked with the supplier and decided by your team, as control 5.22 expects.
When a cloud service stops being used, Montro raises it so your team can re-tier it or plan the exit under control 5.23, with its history kept.
What you get
Where the register helps through the year, not only at the audit.
Agreements
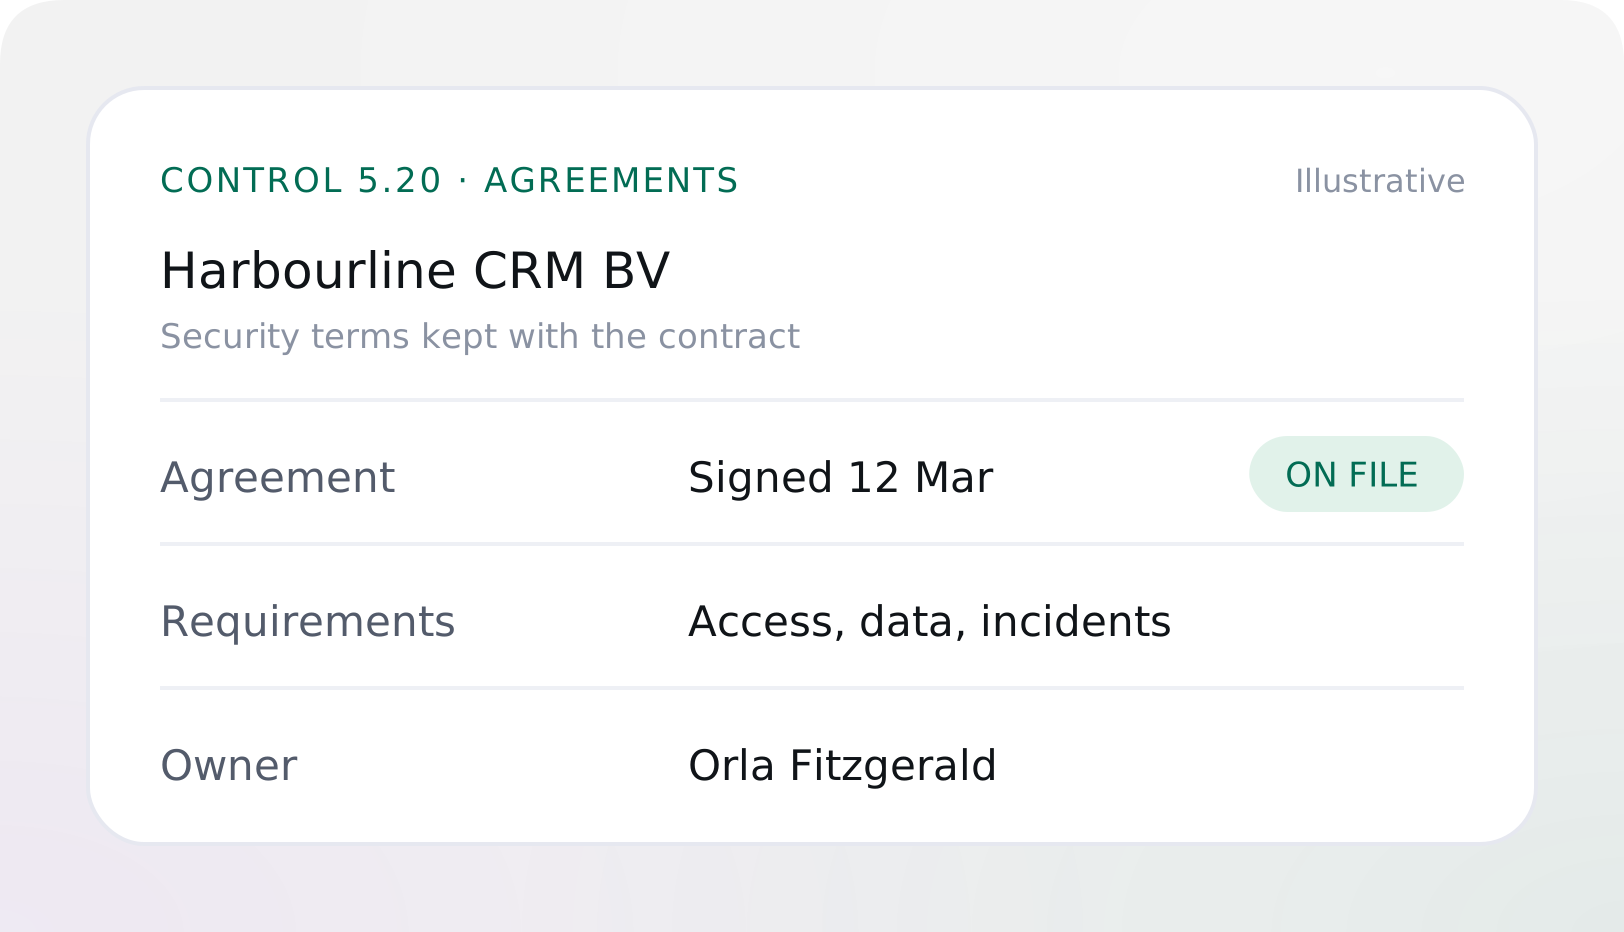
The security requirements agreed with each supplier sit with its entry, so control 5.20 has its evidence in one place.
Sampling
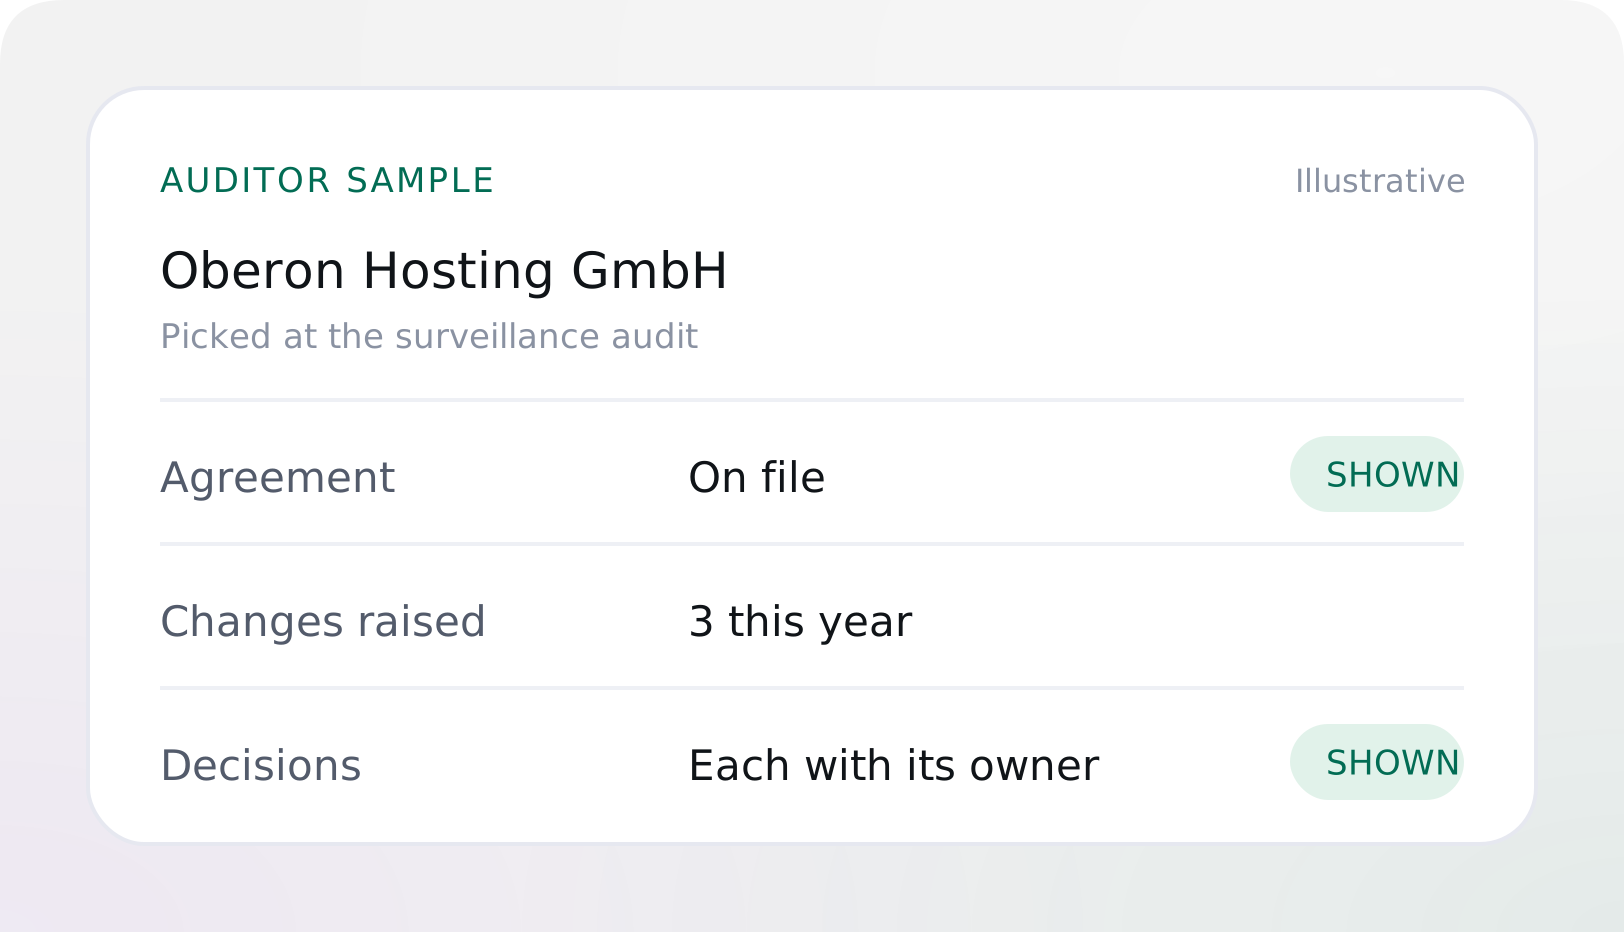
When an auditor picks a supplier, its entry shows the agreement, the changes raised and what your team decided on each.
Review
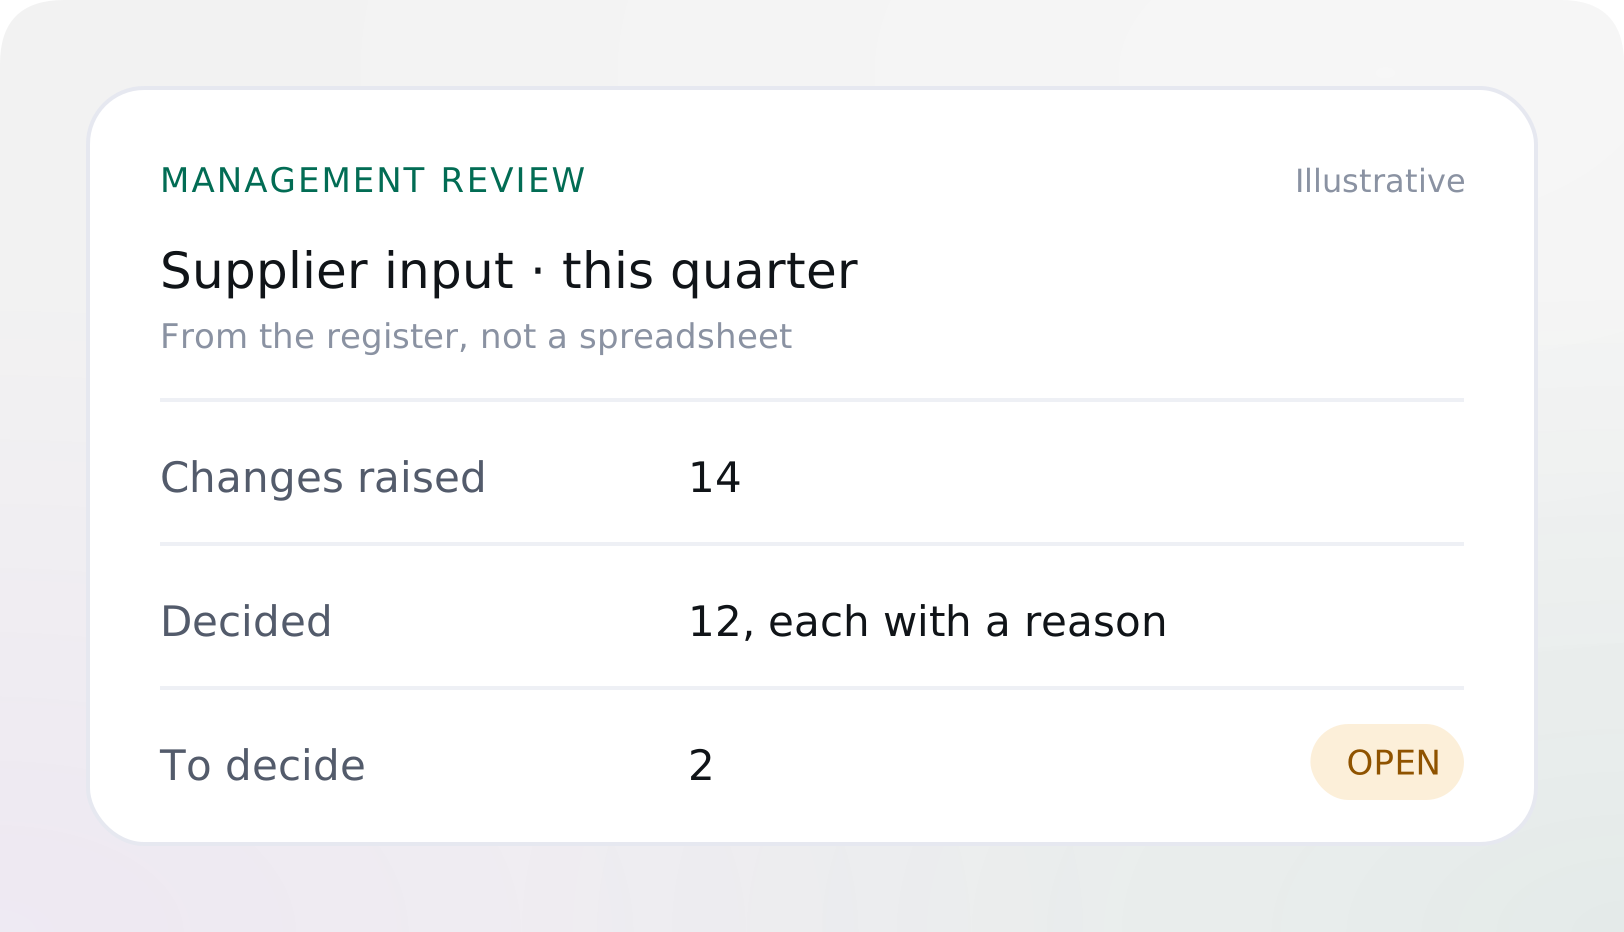
Management review looks at security performance and what has changed. The register gives a current view of supplier changes and the decisions taken on them.
Certificates
Scope
A certificate applies to the scope written on it. Check that the service you buy sits inside that scope, not just the supplier’s name.
Validity
Certificates run for three years, with surveillance audits each year. Check that it is current and comes from an accredited certification body.
The record
Montro keeps each supplier’s certificate scope and expiry with its entry, and raises a lapse for your team to review.
Questions about ISO 27001, and how Montro supports the supplier side of your ISMS.
Keep reading
The same supplier evidence often serves more than one framework. These pages cover the closest.

Supply-chain security under Article 21 asks for much of the same evidence as Annex A.
Read more
The AI management standard, built on the same clauses, for the AI tools in your register.
Read moreSuppliers that send a SOC 2 report instead of a certificate, and what the report tells you.
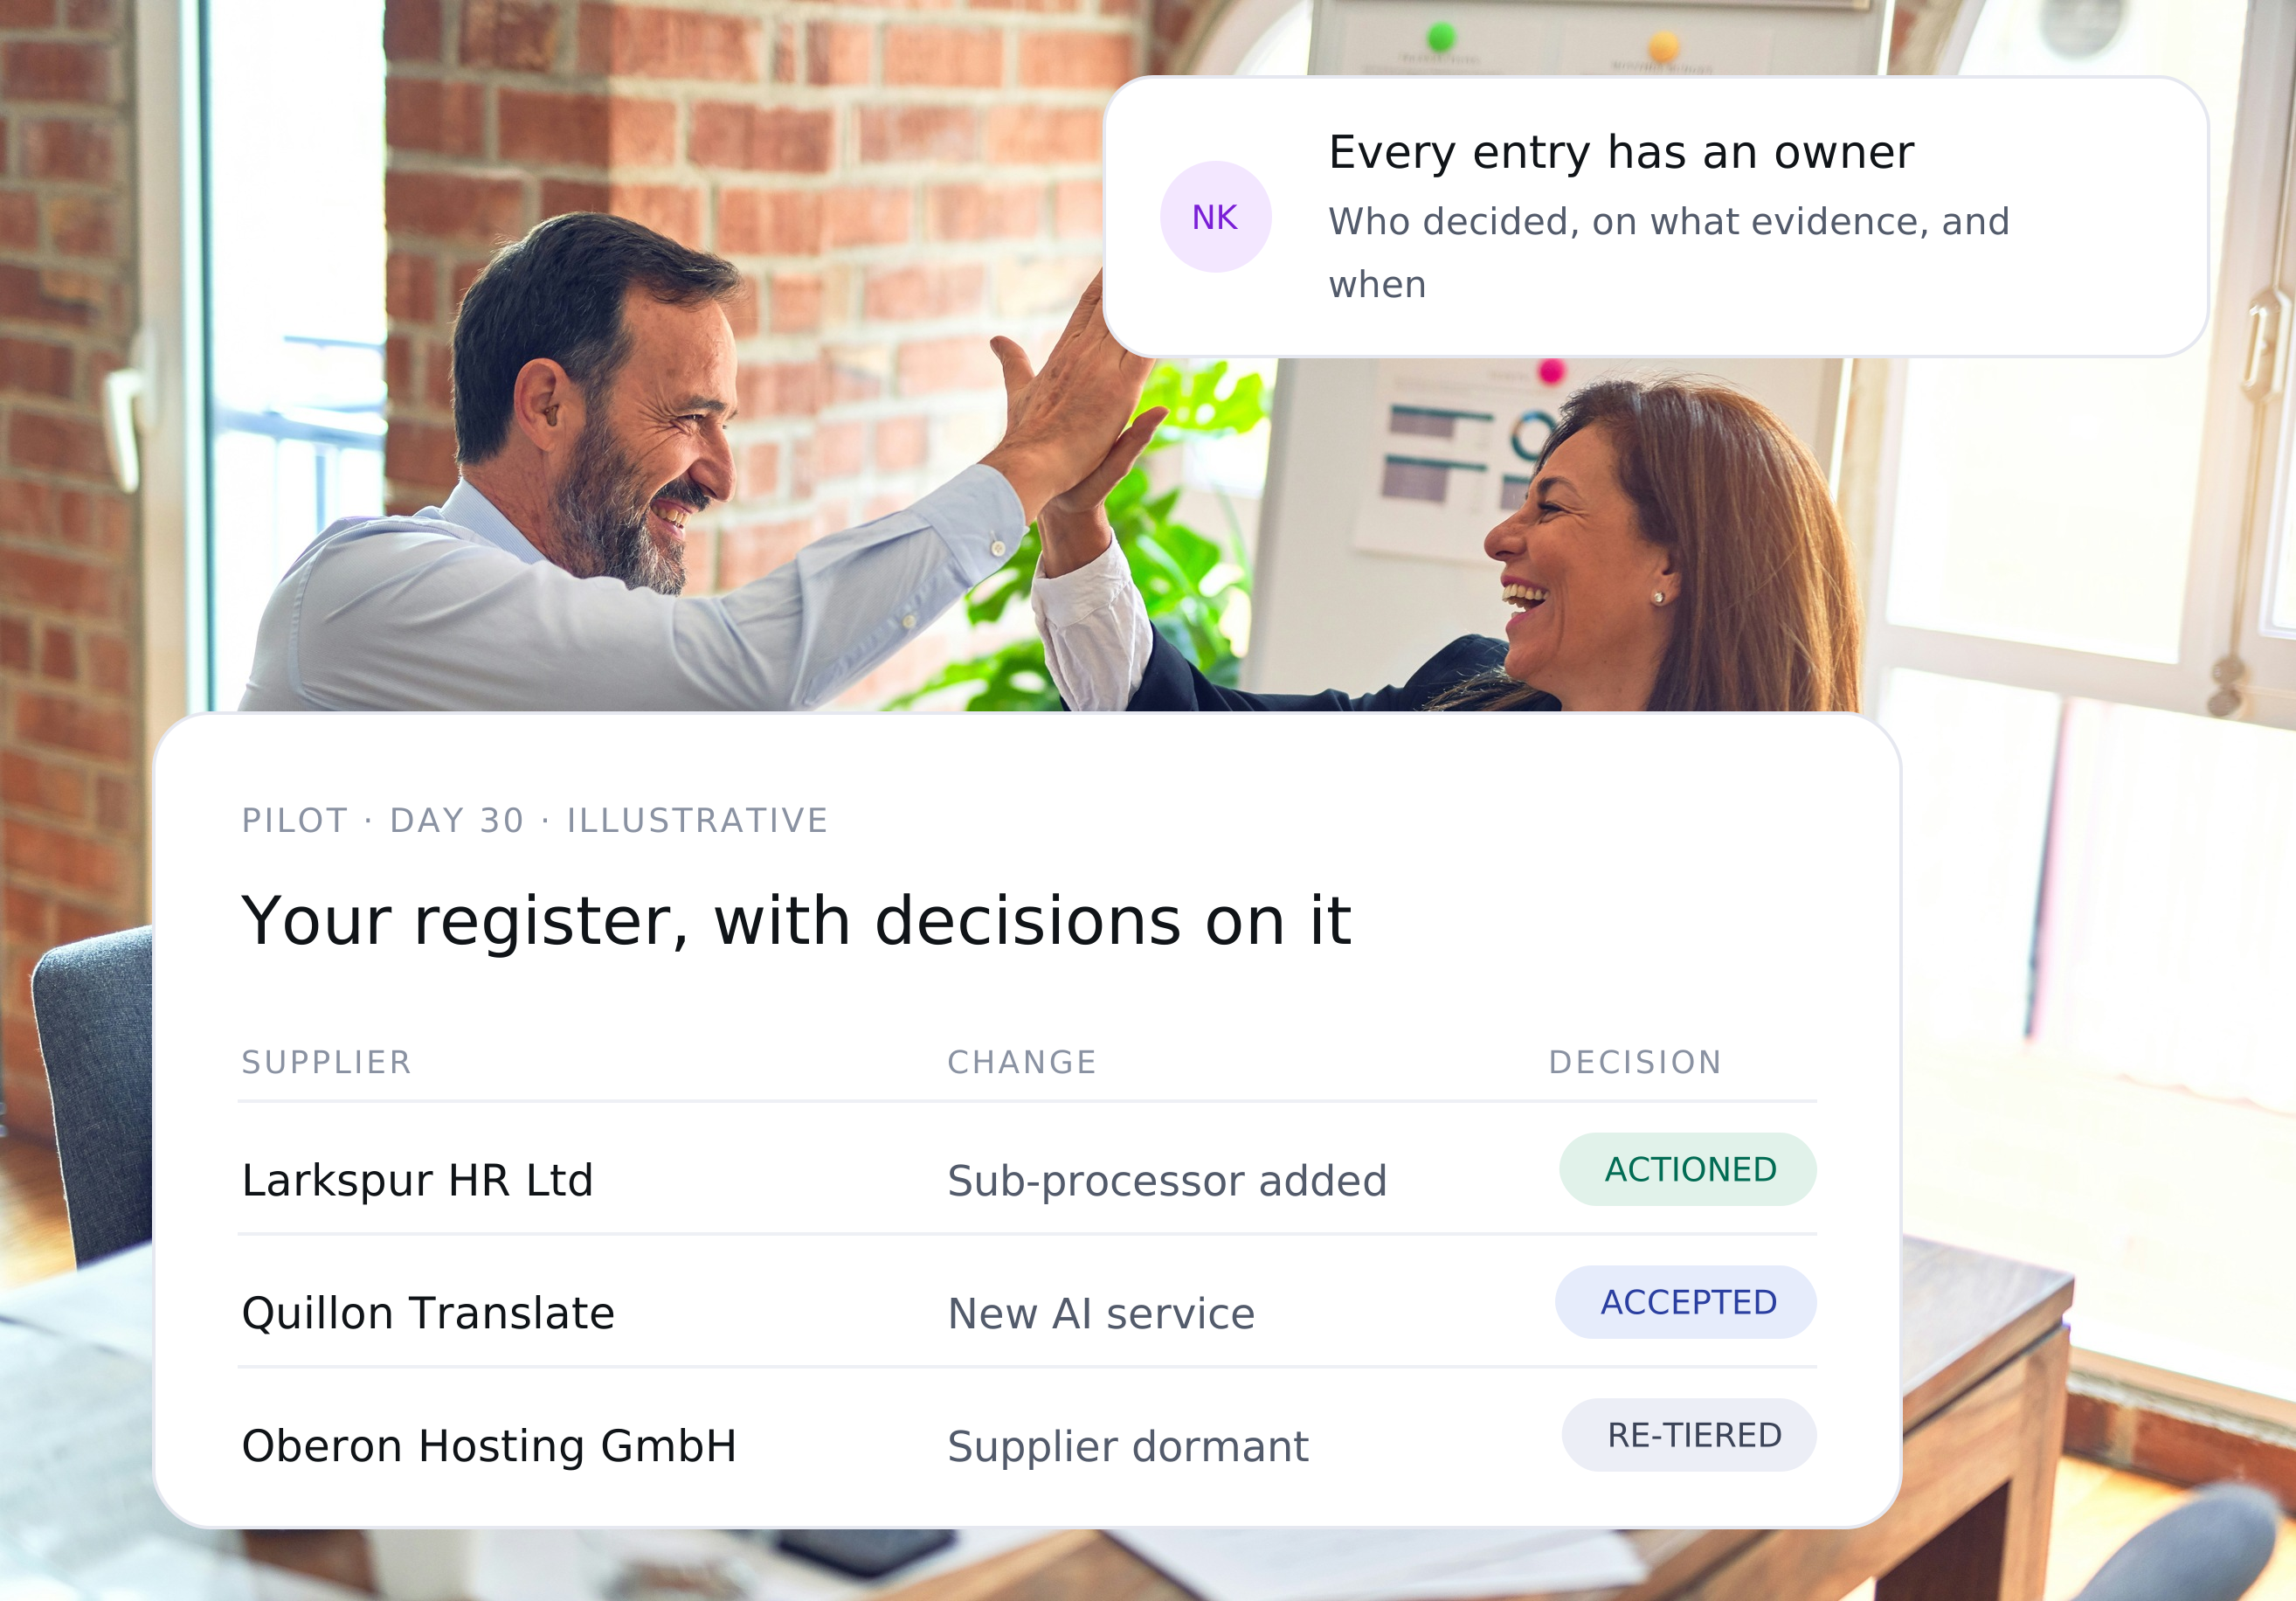
Read moreThird-party records are becoming decision logs. The firms that get this right will be the ones that can show who decided, on what evidence, and when.
A read-only connection, about an hour to set up, and a named person who can say yes to a decision.
Priced to scope — never per seat, never per supplier. Upgrade only when the evidence earns it.