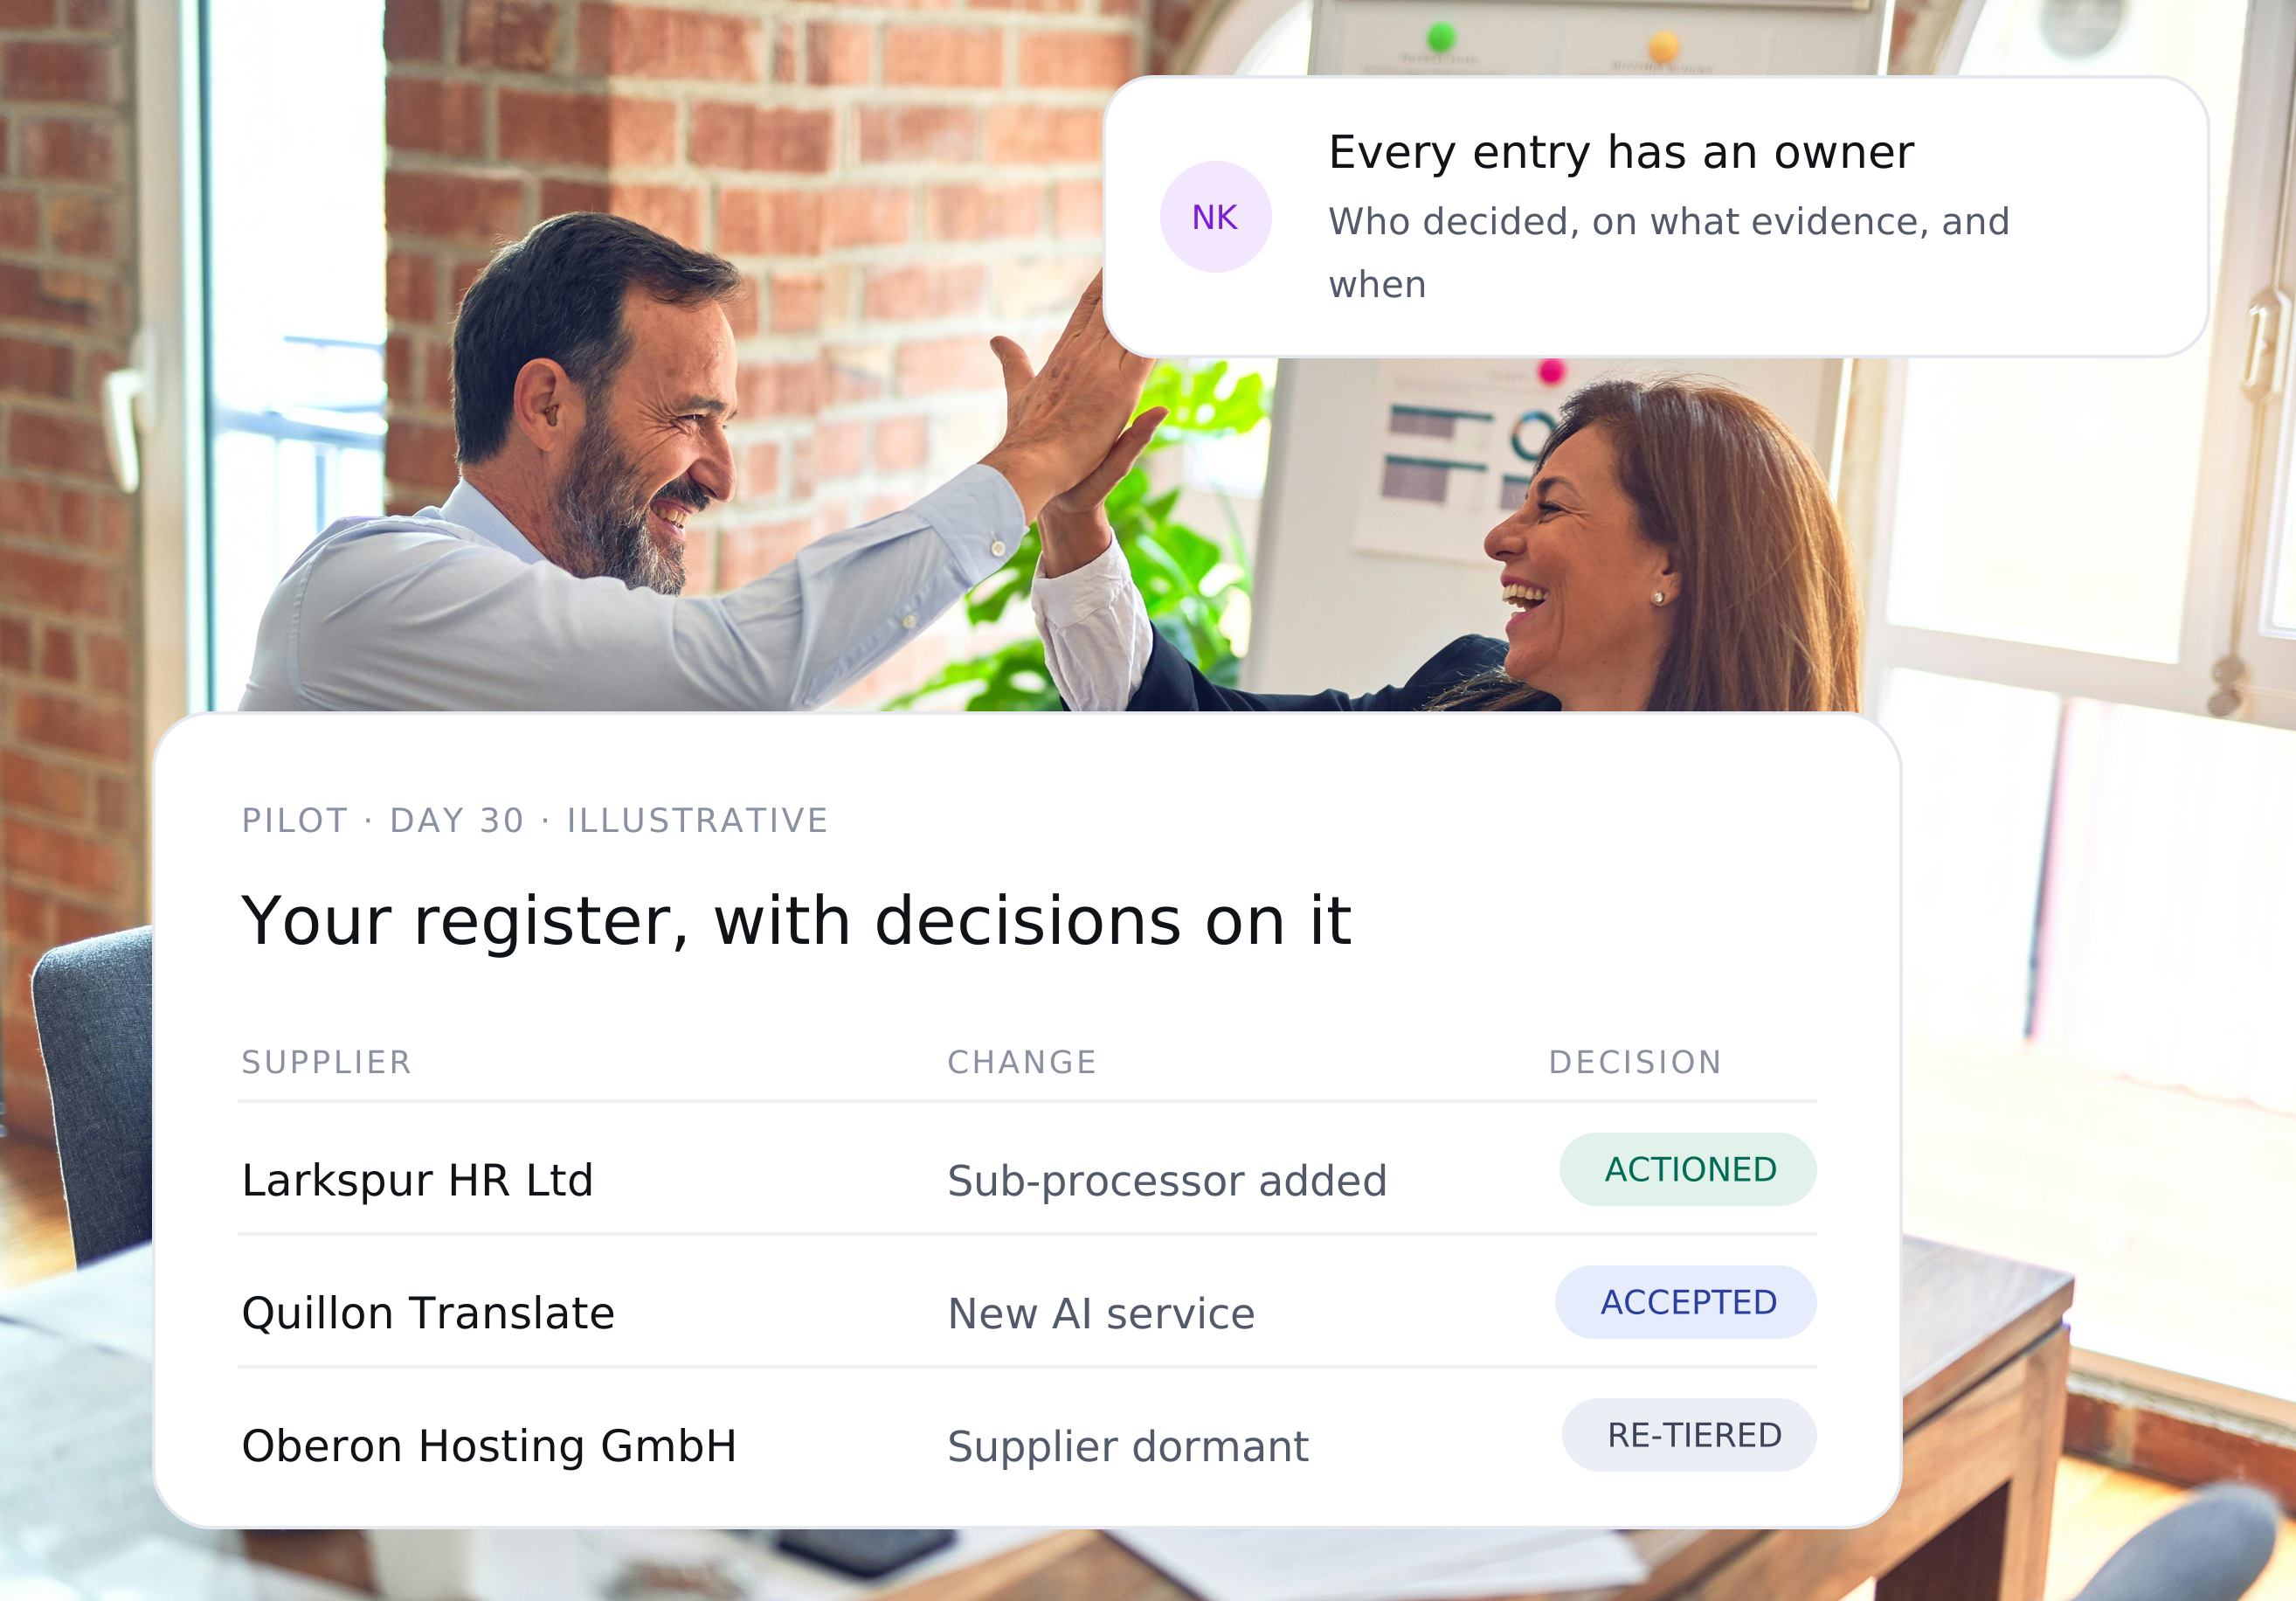
Findings pile up without owners
A security tool can flag a supplier change. It cannot tell you who owns the decision, or record what they decided.
Montro keeps one register of the suppliers and AI services your organisation depends on. Changes reach you as a roll-up with the exceptions that need a decision, each with its source and an owner, so you can show who decided, on what evidence, and when.
The problem
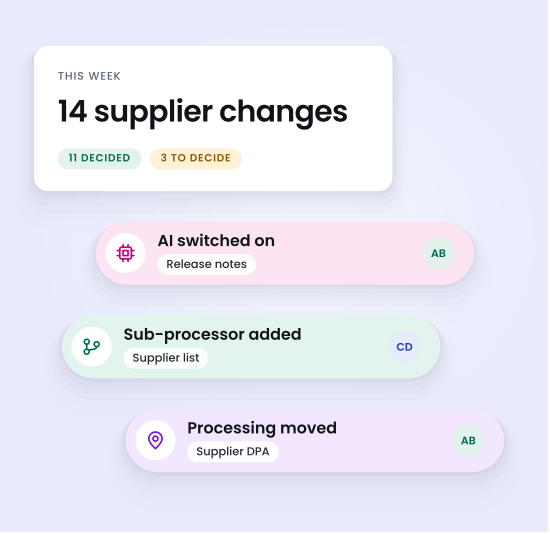
Watching suppliers is easy now. Showing what was decided about each change is not.
A security tool can flag a supplier change. It cannot tell you who owns the decision, or record what they decided.

A supplier switches on an AI feature, and the approval you gave last year no longer covers what the tool does.

A list of every alert does not answer whether your suppliers are in a state you can defend.
How Montro helps
Three steps that turn a list of suppliers into evidence.
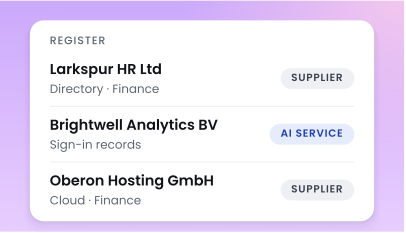
Register
Built read-only from sign-in, directory, finance and cloud data.
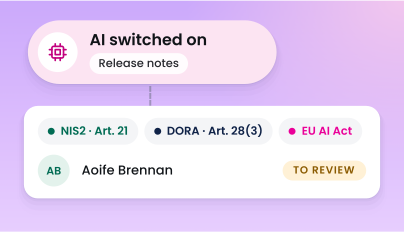
Changes
Mapped to the NIS2, DORA and EU AI Act articles it touches, for its owner to review.
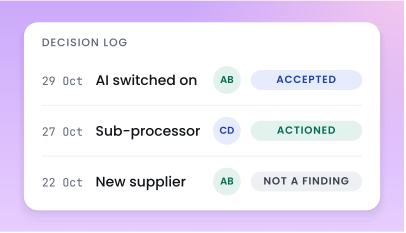
Decisions
A roll-up for the board, and the trail behind each answer for the examiner.
Setup
An admin approves read-only access. Montro starts building the register straight away, and your team decides on what it raises.
Microsoft Entra ID, Google Workspace or Okta, approved by an admin. No agents to install.
Suppliers and AI services found so far, each raised with its source for its owner to review.
Owners decide on each candidate, and entries are mapped to GDPR, the EU AI Act, DORA and NIS2.
New changes are raised as they appear, dormant suppliers are re-tiered, not removed, and every entry keeps its owner.
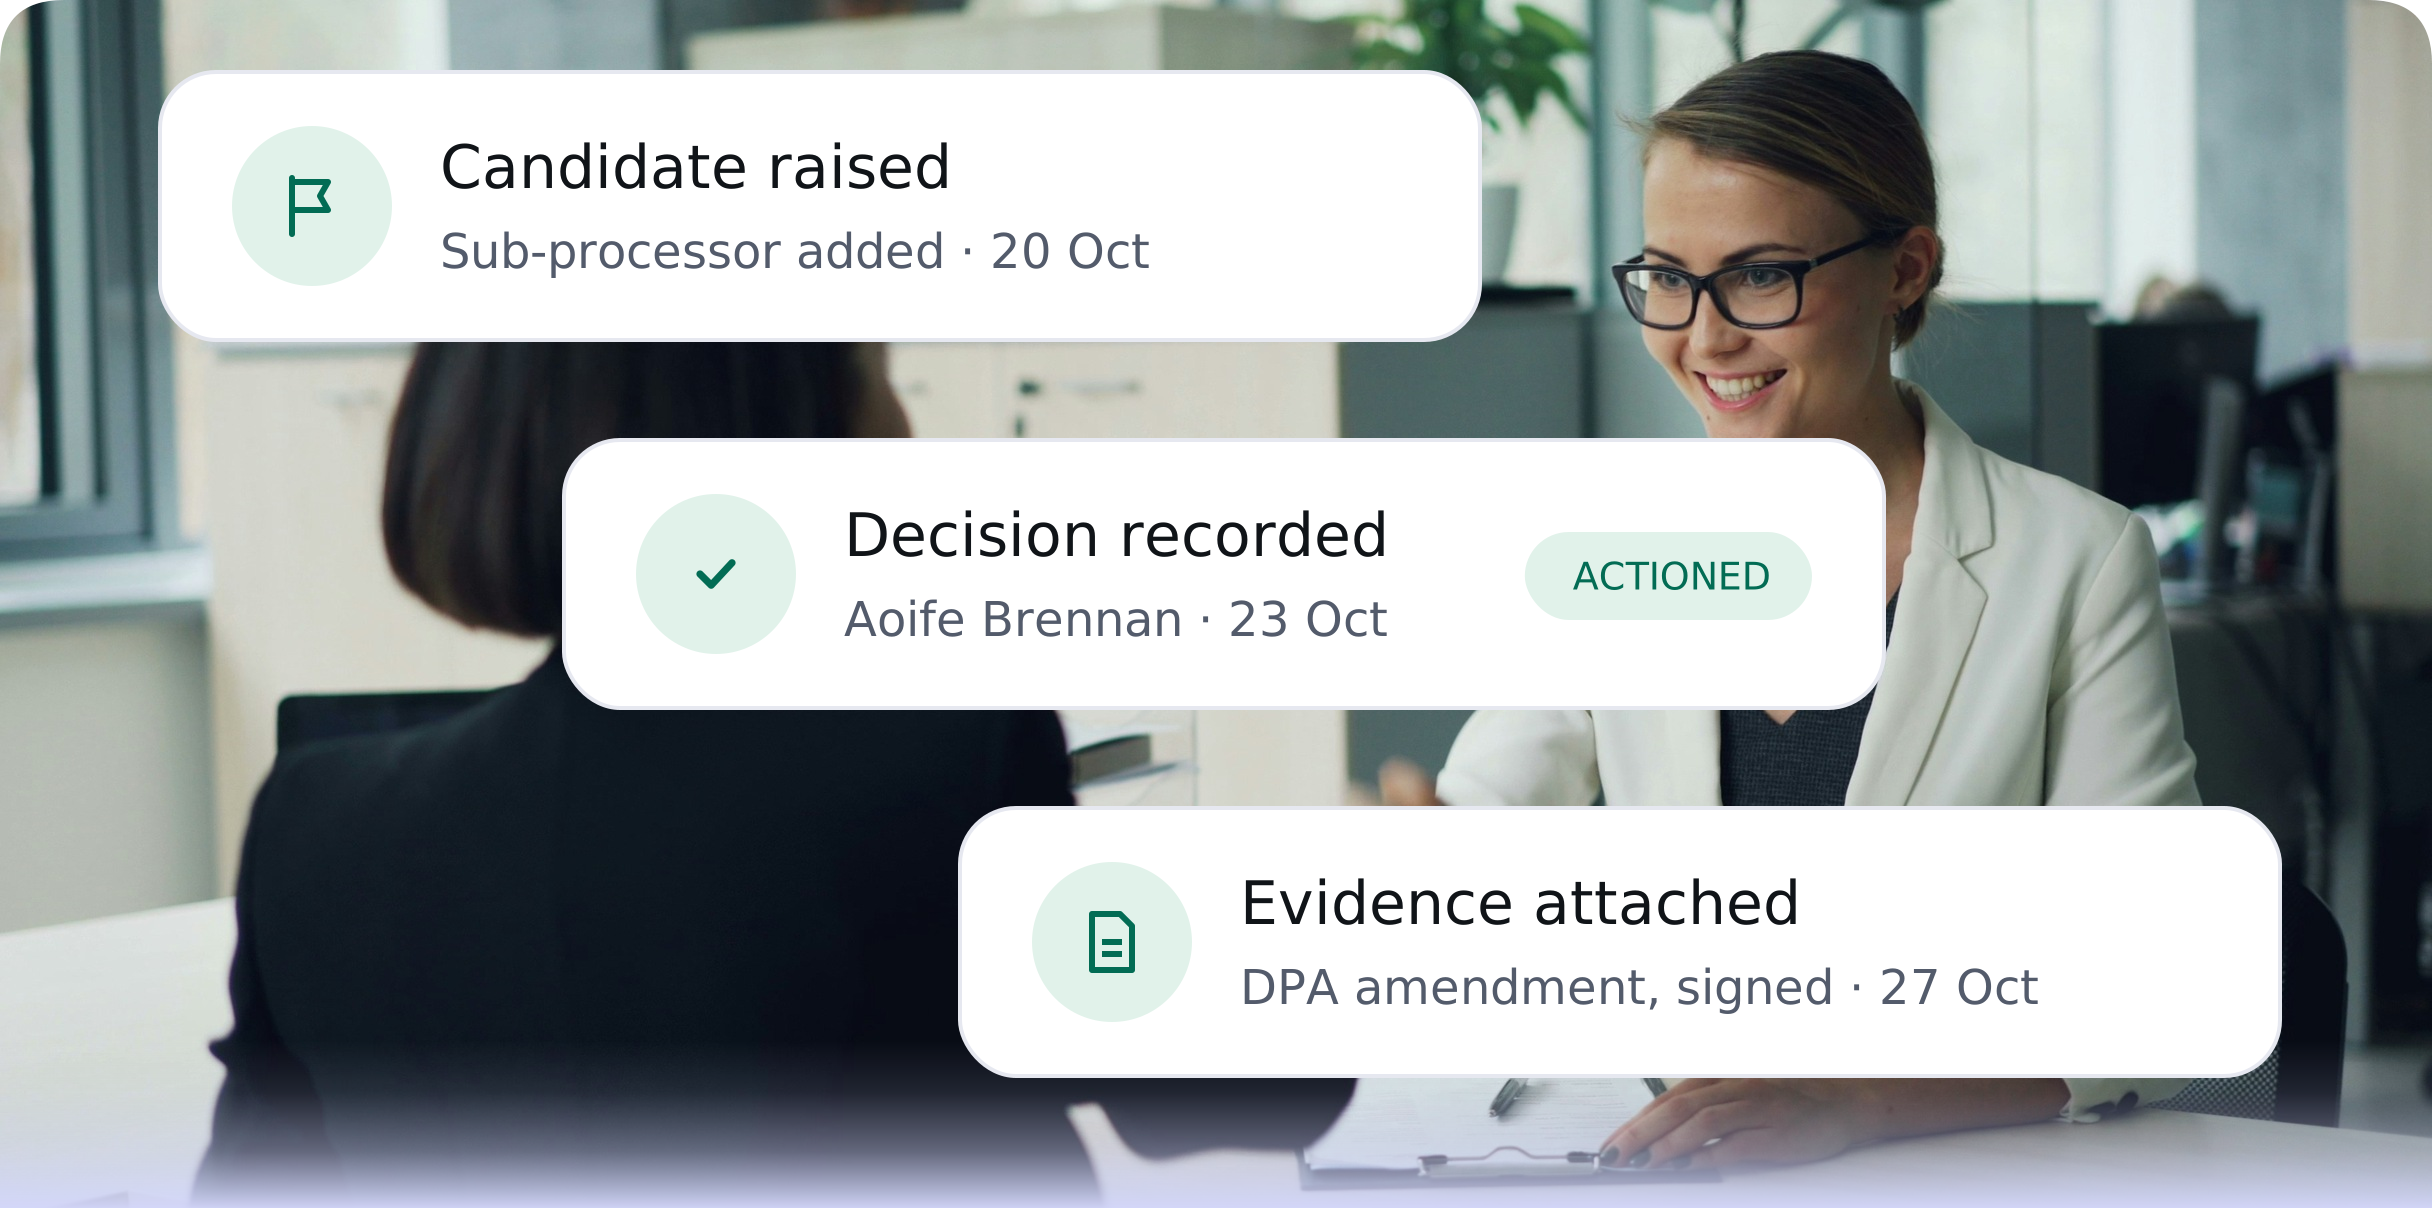
Outcome
A register with a decision behind every entry, in place of spreadsheets and screenshots.
Obligations
DORA, NIS2 and the EU AI Act each ask for their own record. Montro keeps all three from the same read-only intake, so a change is reviewed once and reflected in every record it touches.
Article 28(3), for financial entities. Each ICT contract, the function it supports, whether that function is critical or important, and the exit plan, kept current for your filing.
Learn moreArticle 21. The suppliers behind your network and information systems, each with an owner and a decision on every change.
Learn moreThe AI systems you use as a deployer, recorded in the same register as your suppliers, so one review covers both.
Learn moreKeep reading
One register serves every seat at the table. See what it gives your colleagues.

Sub-processor changes reach your DPO confirmed by the supplier, so the Article 30 record stays true.
Read more
IT decides which candidates cross into the register, and sees unused licences before renewal.
Read more
The register of information, current and with a decision behind every entry, ready for the examiner.
Read moreThe questions CISOs ask before they connect anything.
Third-party records are becoming decision logs. The firms that get this right will be the ones that can show who decided, on what evidence, and when.
A read-only connection, about an hour to set up, and a named person who can say yes to a decision.
Priced to scope — never per seat, never per supplier. Upgrade only when the evidence earns it.