
Your teams are already using AI.Do you know which ones?
Montro discovers shadow AI tools your IT team doesn't know exist — then maps them to EU AI Act, DORA, NIS2 and GDPR before the auditor arrives.
Free 30-day AI Discovery Audit. No commitment.
The reality
Why one platform matters
Most European organisations don't know which AI tools their teams are using. One shadow AI tool can trigger violations across four separate EU regulations simultaneously.
26 of 50
Top shadow apps are AI
€35M
Maximum EU AI Act Fine
82%
DPOs use spreadsheets for RoPA
Features
One platform. Four regulations. Zero spreadsheets.
Montro connects shadow AI discovery to EU compliance outputs — so your team spends less time finding tools and more time governing them.
Discover. Map. Own.
Every AI tool your organisation is using — including the ones IT doesn't know about
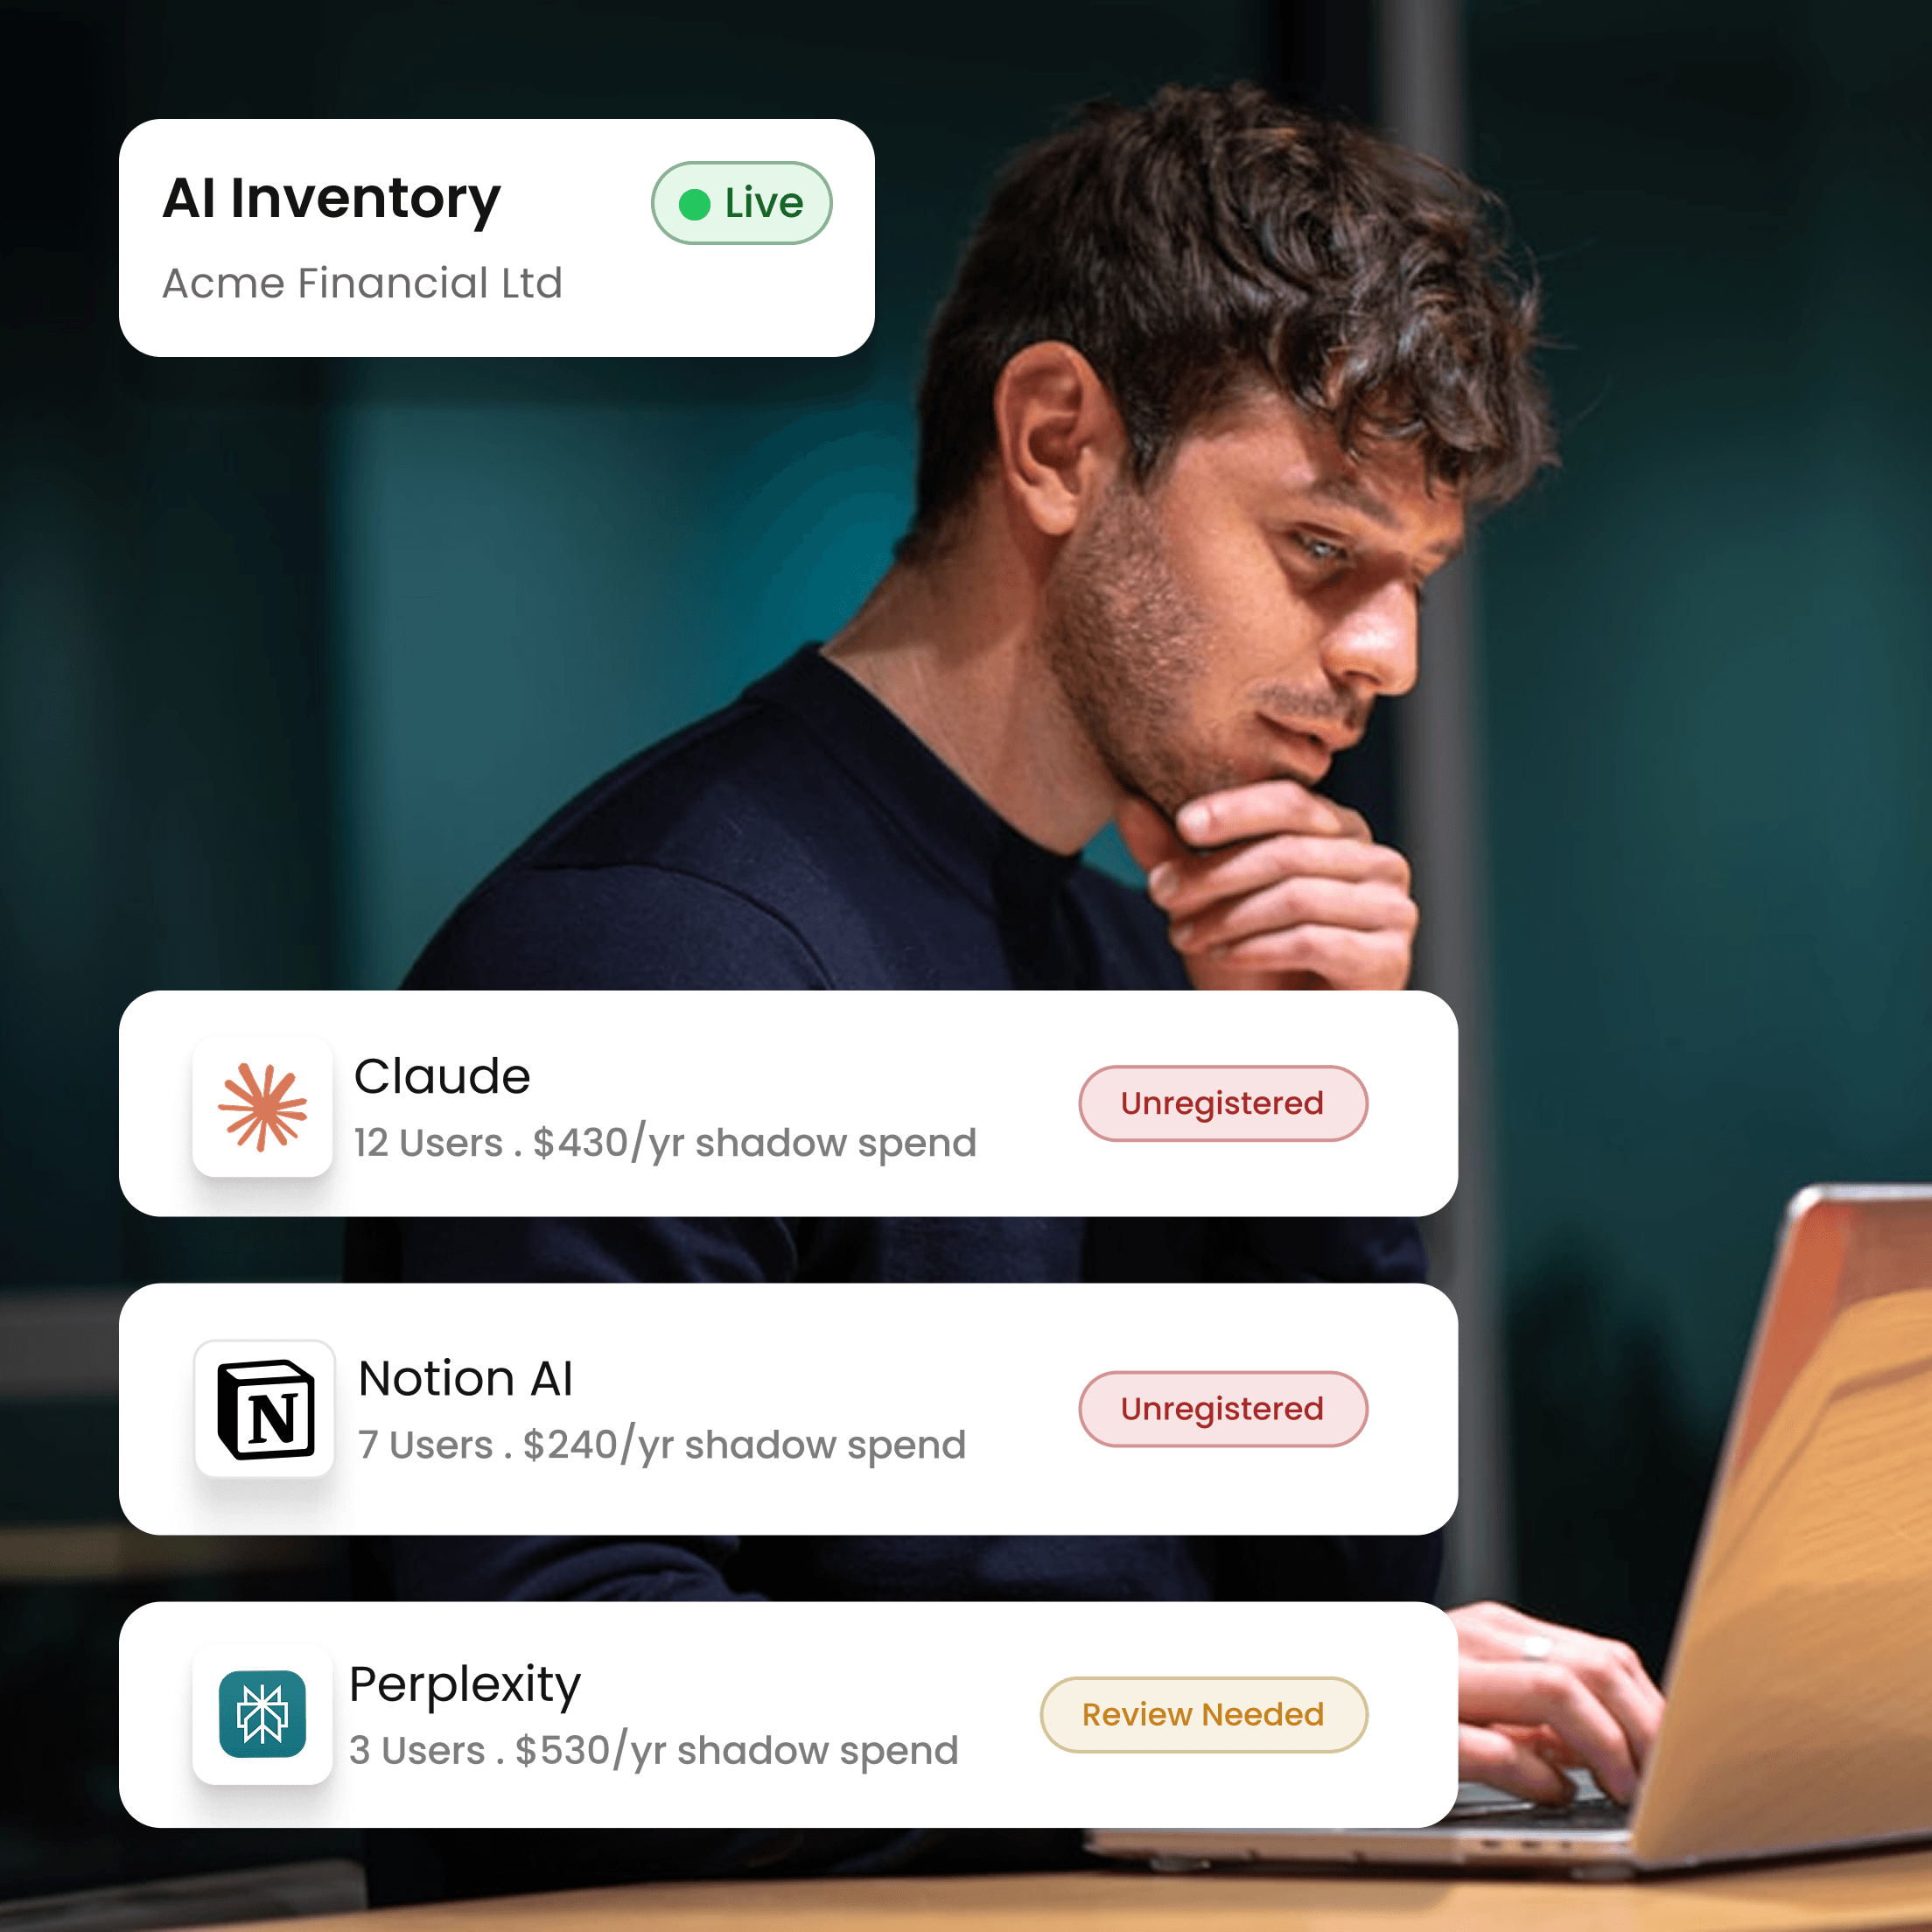
Montro scans your SaaS and cloud environment and builds a complete AI inventory from day one. Every tool is catalogued, owner-assigned, and mapped to the employees using it. You'll also see shadow subscriptions and unauthorised spend — because ungoverned tools and wasted budget are the same problem.
Regulatory
Four regulatory clocks
Four regulations. Four deadlines. One shadow AI tool can violate all of them.
January 2025
DORA goes live
Financial firms have four hours to report a major ICT incident once it's classified. No spreadsheet will catch that deadline.
January 2025
DORA goes live
Financial firms have four hours to report a major ICT incident once it's classified. No spreadsheet will catch that deadline.
Expected late 2026 (Ireland)
NIS2 incident reporting
Ireland is expected to transpose NIS2 by end of 2026, pulling an estimated 4,500 organisations into scope. You'll have 24 hours to file an early warning, 72 for a full report. Montro tracks every AI tool and SaaS app that touches your systems.
Expected late 2026 (Ireland)
NIS2 incident reporting
Ireland is expected to transpose NIS2 by end of 2026, pulling an estimated 4,500 organisations into scope. You'll have 24 hours to file an early warning, 72 for a full report. Montro tracks every AI tool and SaaS app that touches your systems.
Ongoing
GDPR breach notification
You have 72 hours to notify the DPC once you're aware of a personal data breach. Every unmanaged SaaS app and AI tool is a breach waiting to happen.
Ongoing
GDPR breach notification
You have 72 hours to notify the DPC once you're aware of a personal data breach. Every unmanaged SaaS app and AI tool is a breach waiting to happen.
2 December 2027
EU AI Act - high-risk deadline
The Digital Omnibus pushed high-risk obligations (Annex III - hiring, credit, essential services) to December 2027. But transparency rules still bite from August 2026. If you haven't started your AI inventory, you're already behind.
2 December 2027
EU AI Act - high-risk deadline
The Digital Omnibus pushed high-risk obligations (Annex III - hiring, credit, essential services) to December 2027. But transparency rules still bite from August 2026. If you haven't started your AI inventory, you're already behind.
For the people who own compliance
Built for the people regulators hold accountable
CISOs, DPOs, and IT Directors in European mid-market organisations face enterprise-grade regulatory obligations with a fraction of the resources. Montro gives each of them exactly what they need — without spreadsheets.

CISOs
Every shadow AI tool is an unmanaged attack surface and a regulatory exposure. Montro gives you a live inventory of every AI connection in your environment — so you're never the last to know.
Learn more
DPOs
Your RoPA won't maintain itself. Montro auto-drafts GDPR records directly from your AI and SaaS inventory — so your documentation stays current without a manual update cycle before every audit.
Learn more
IT Directors
You can't govern what you can't see. Montro surfaces every AI tool employees are using — including shadow subscriptions — and maps each one to your EU compliance obligations before IT is asked to explain it.
Learn more
CFOs
Your organisation is bleeding money on software nobody uses and deploying AI tools nobody has approved. Montro finds both, quantifies the cost, and helps you act before regulators do.
Learn more
European
Built where the regulators are
Montro runs on EU infrastructure and answers to European data protection law. Your compliance register stays in Europe — built by people who understand how the DPC, BaFin, CNIL, and ICO actually enforce these rules.

Data stays in Europe
All data is stored in the EU. No US cloud. No data transfers. Full compliance with GDPR and the EU AI Act.

Built for European regulators
Designed by people who understand how the DPC, BaFin, CNIL, and ICO actually work. Not a US platform retrofitted for Europe.
Find every AI tool running in your organisation
In 30 days. For free. No credit card. No long-term commitment. Just visibility.
Free 30-day AI Discovery Audit. No commitment.

FAQ
Questions about implementation, data residency, and how Montro keeps your compliance register audit-ready.
Works Across the Tools You Already Rely On
Montro discovers AI tools across your existing stack — no agents, no manual imports. Connect once and your inventory stays current.
People
Built in Dublin
We have spent years transforming how large enterprises adopt technology and ensuring financial institutions did it compliantly. Montro exists because those two jobs have never been in the same room — until now

