Structure
Levels that build on each other
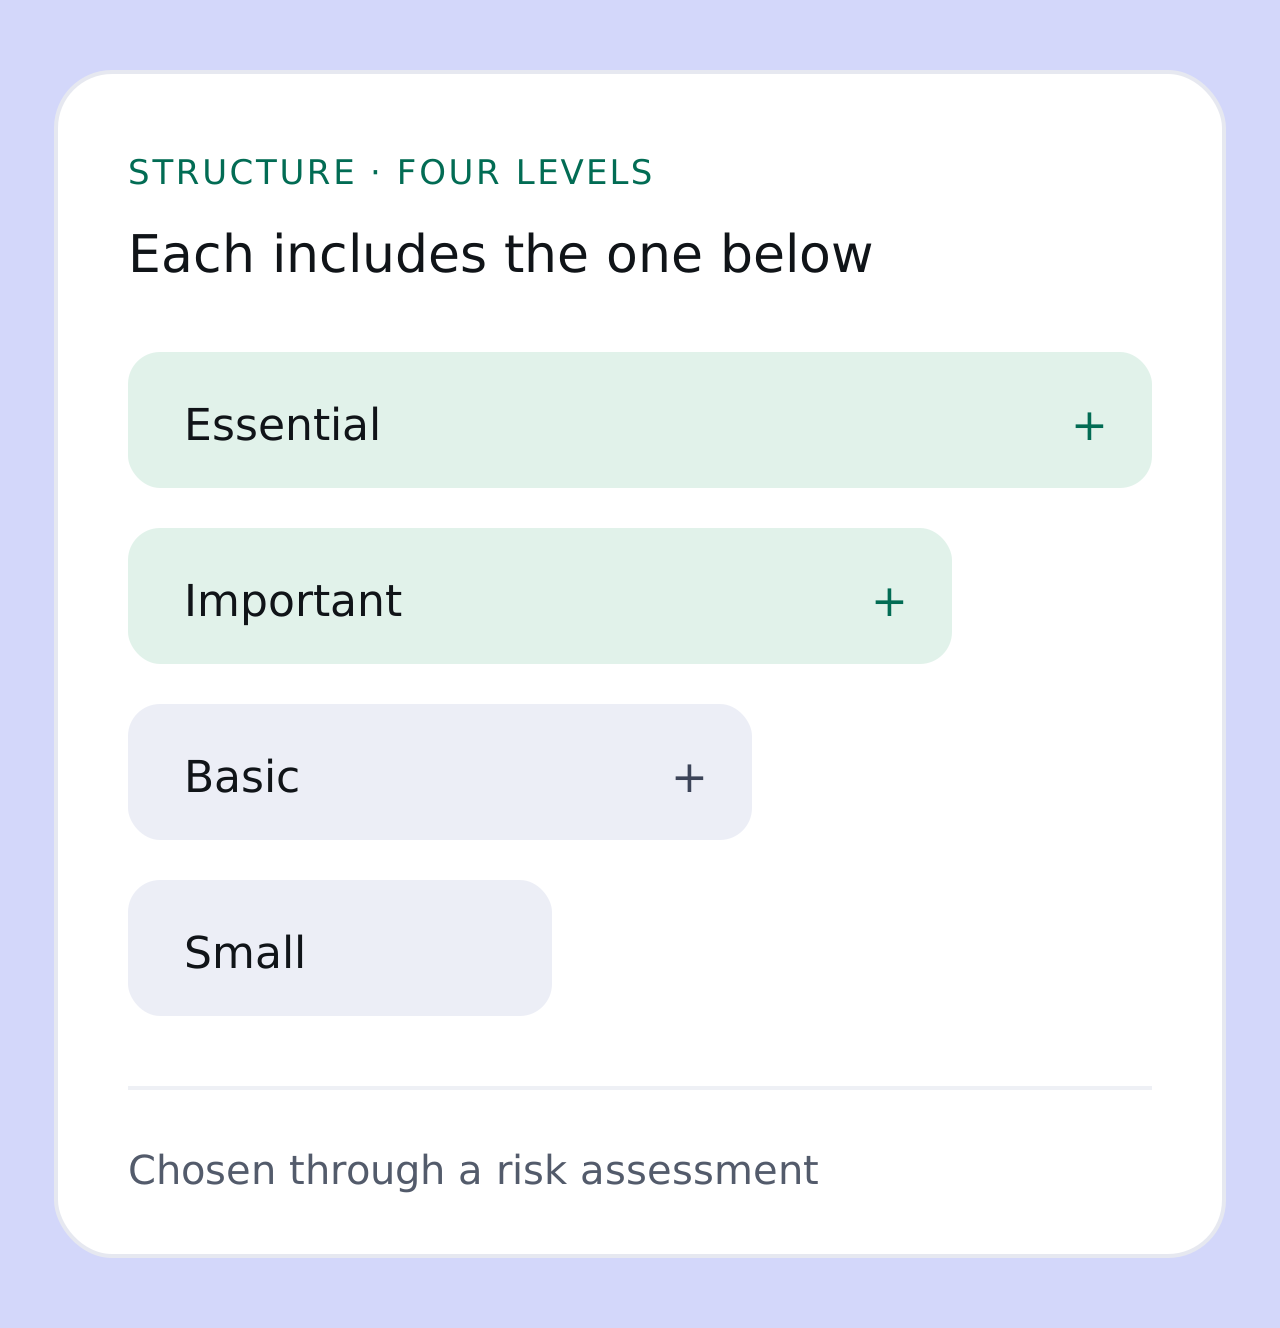
Small, Basic, Important and Essential. You choose a level through a risk assessment, and each one includes everything below it.
CyberFundamentals (CyFun) is the framework the Centre for Cybersecurity Belgium built to turn NIS2 into concrete measures. Under Belgium’s NIS2 law, a verified or certified CyFun level gives a presumption of conformity with the risk-management measures.
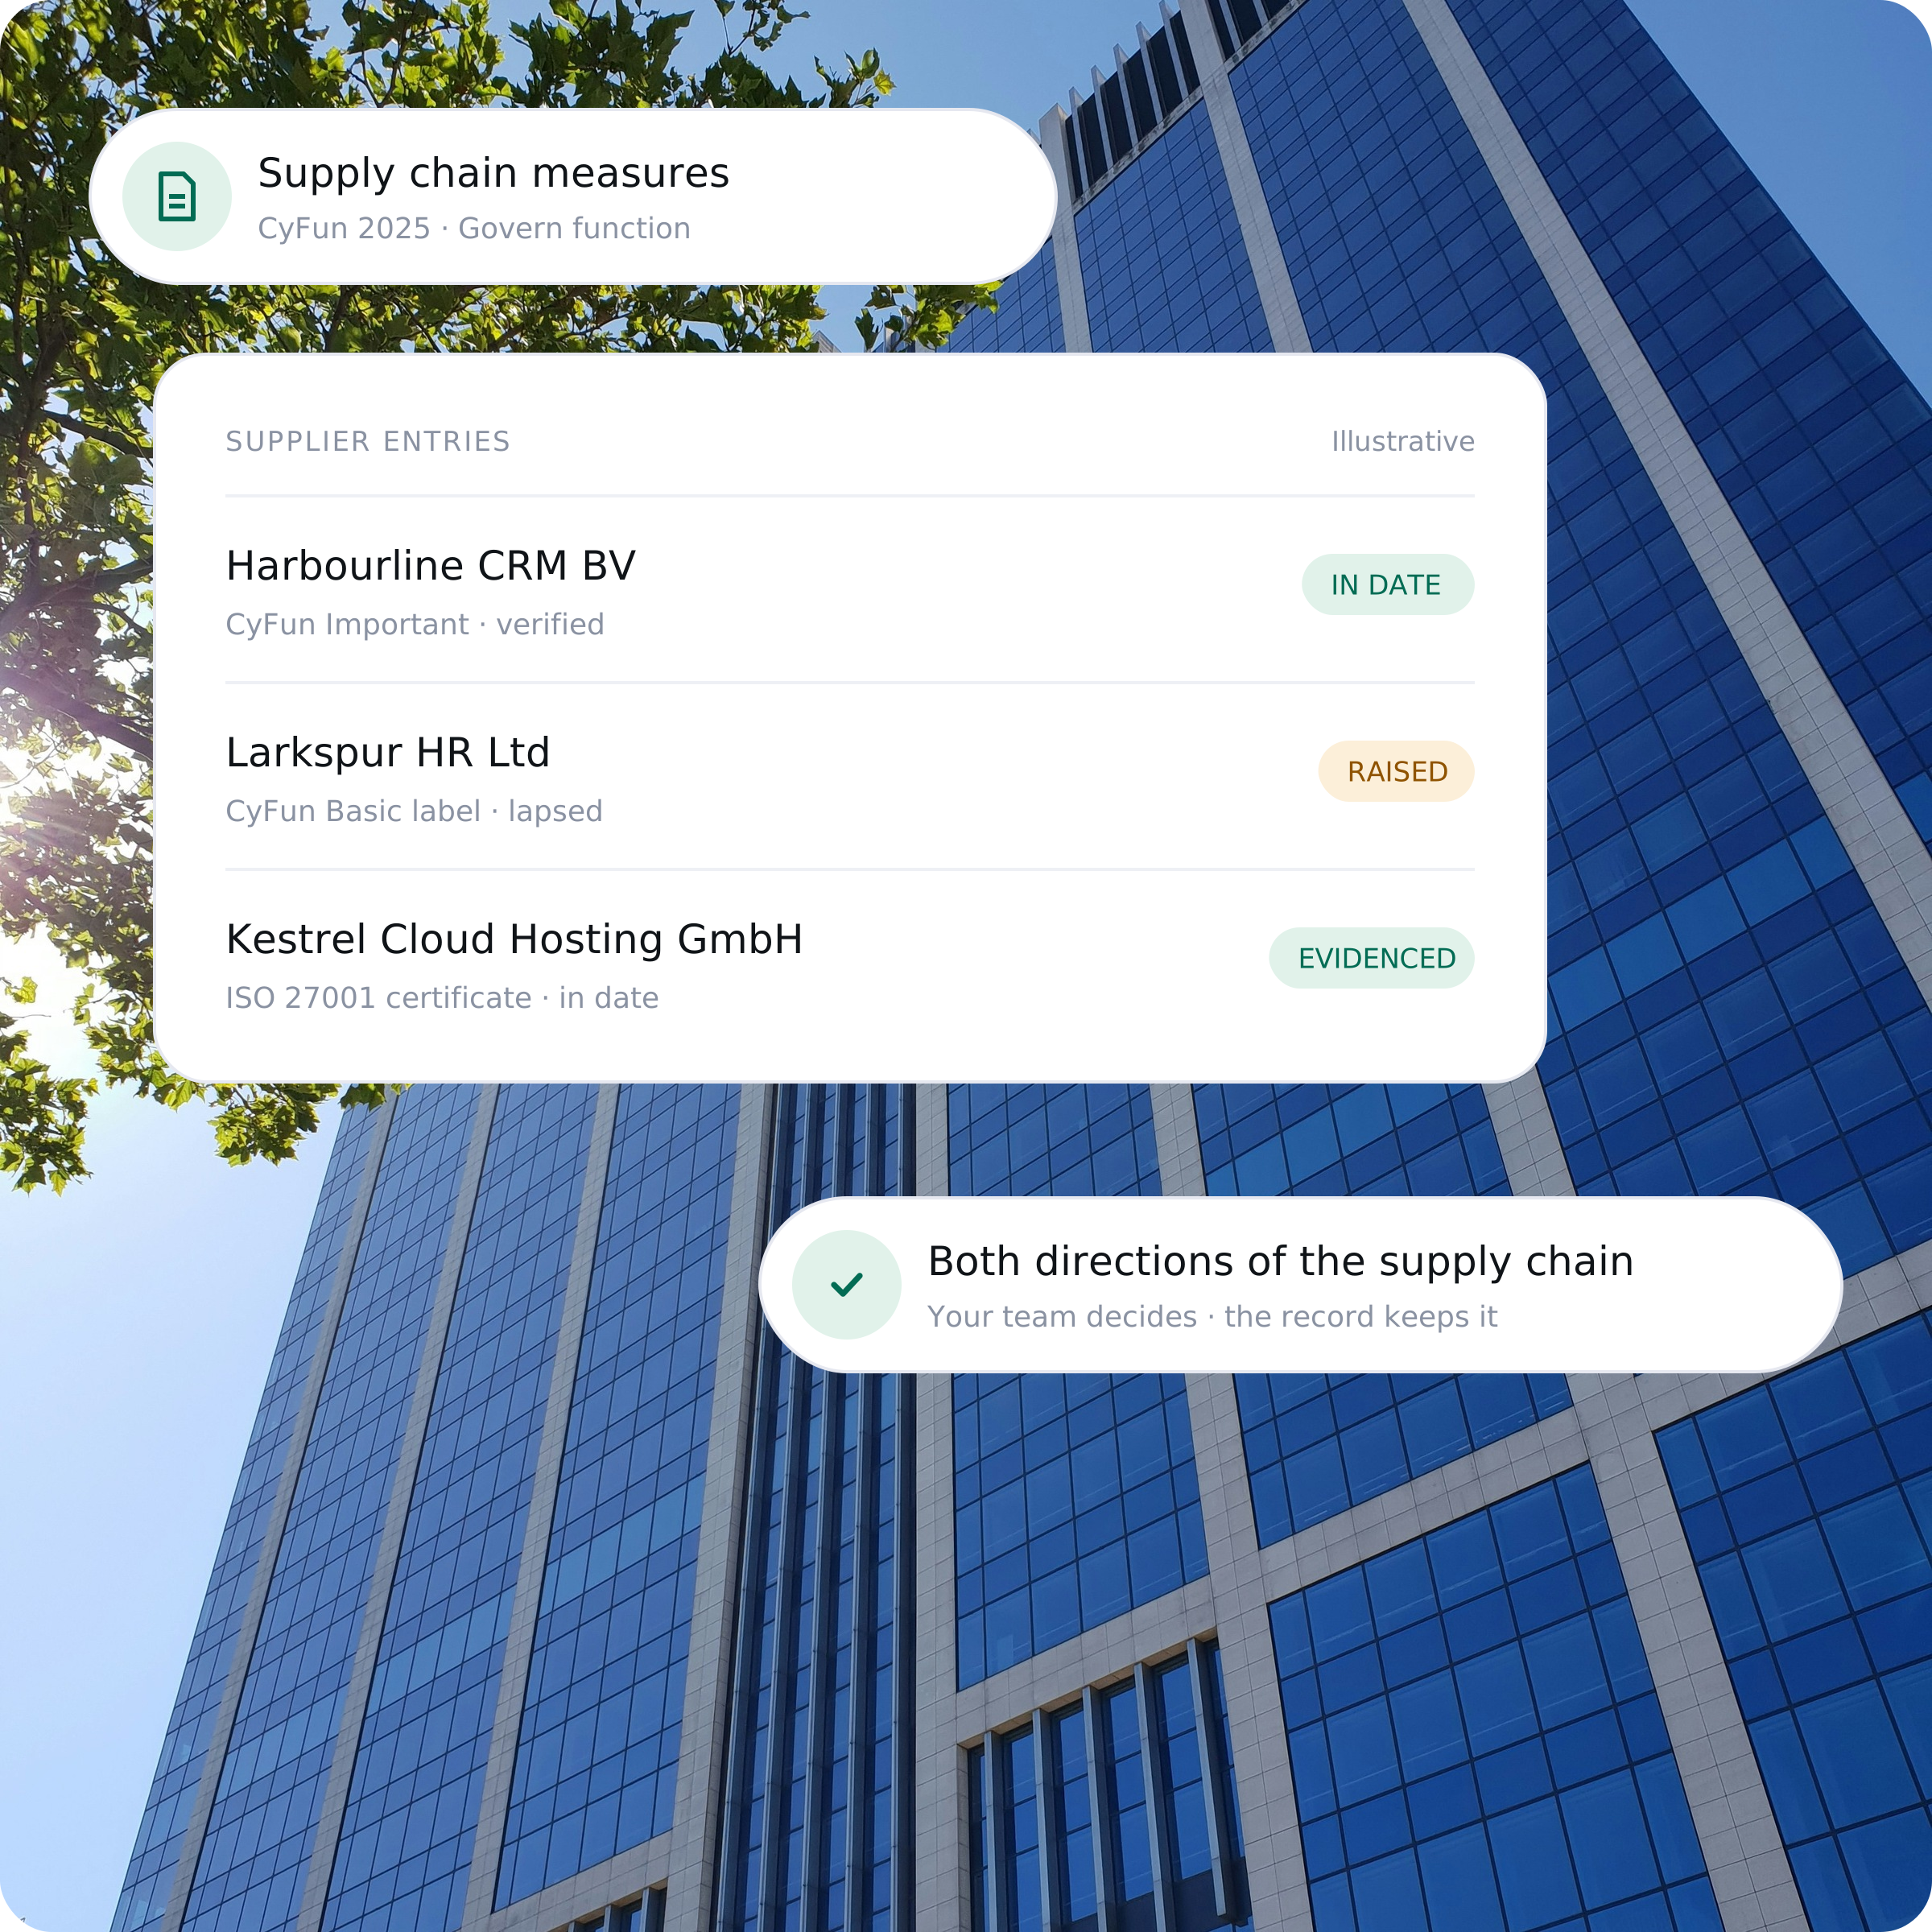
Montro keeps the supplier side of those measures in one register, and records the CyFun level your own suppliers hold, so both directions of the supply chain are on file.
Framework
CyFun 2025 is organised around the six functions of NIST CSF 2.0 and draws on ISO 27001, the CIS Controls and IEC 62443. Each level adds requirements to the one before.
Structure
Small, Basic, Important and Essential. You choose a level through a risk assessment, and each one includes everything below it.
Assessment
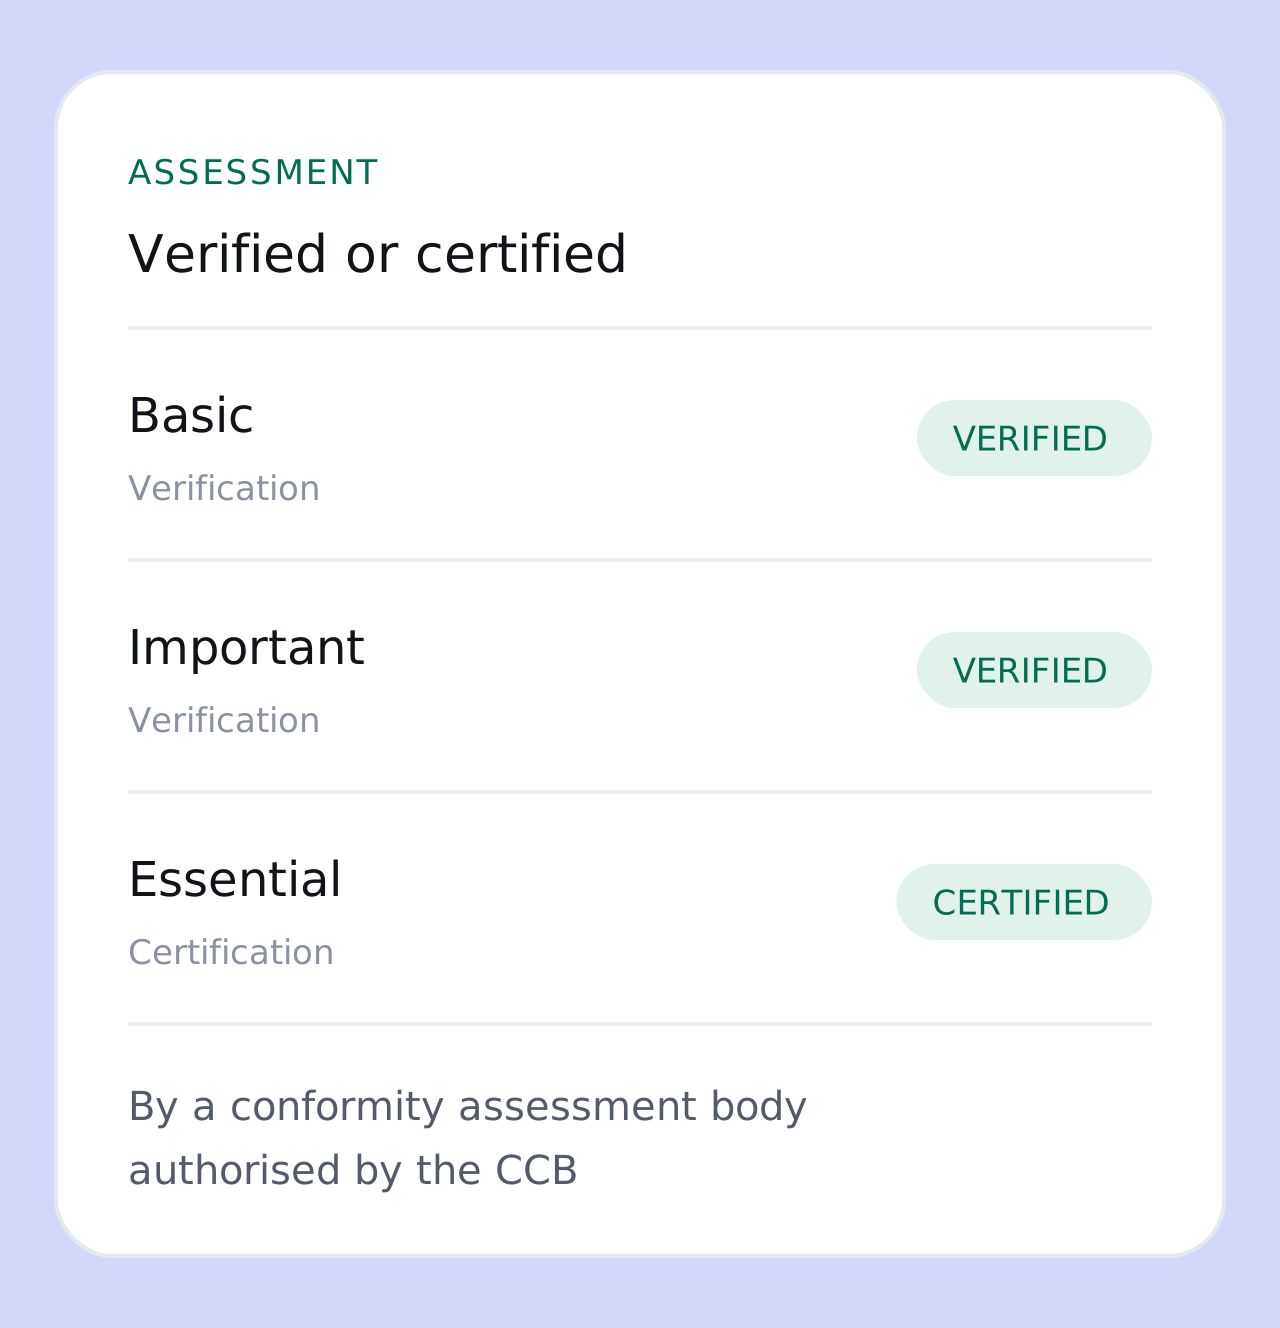
Basic and Important are verified, and Essential is certified, by a conformity assessment body authorised by the CCB.
Scope
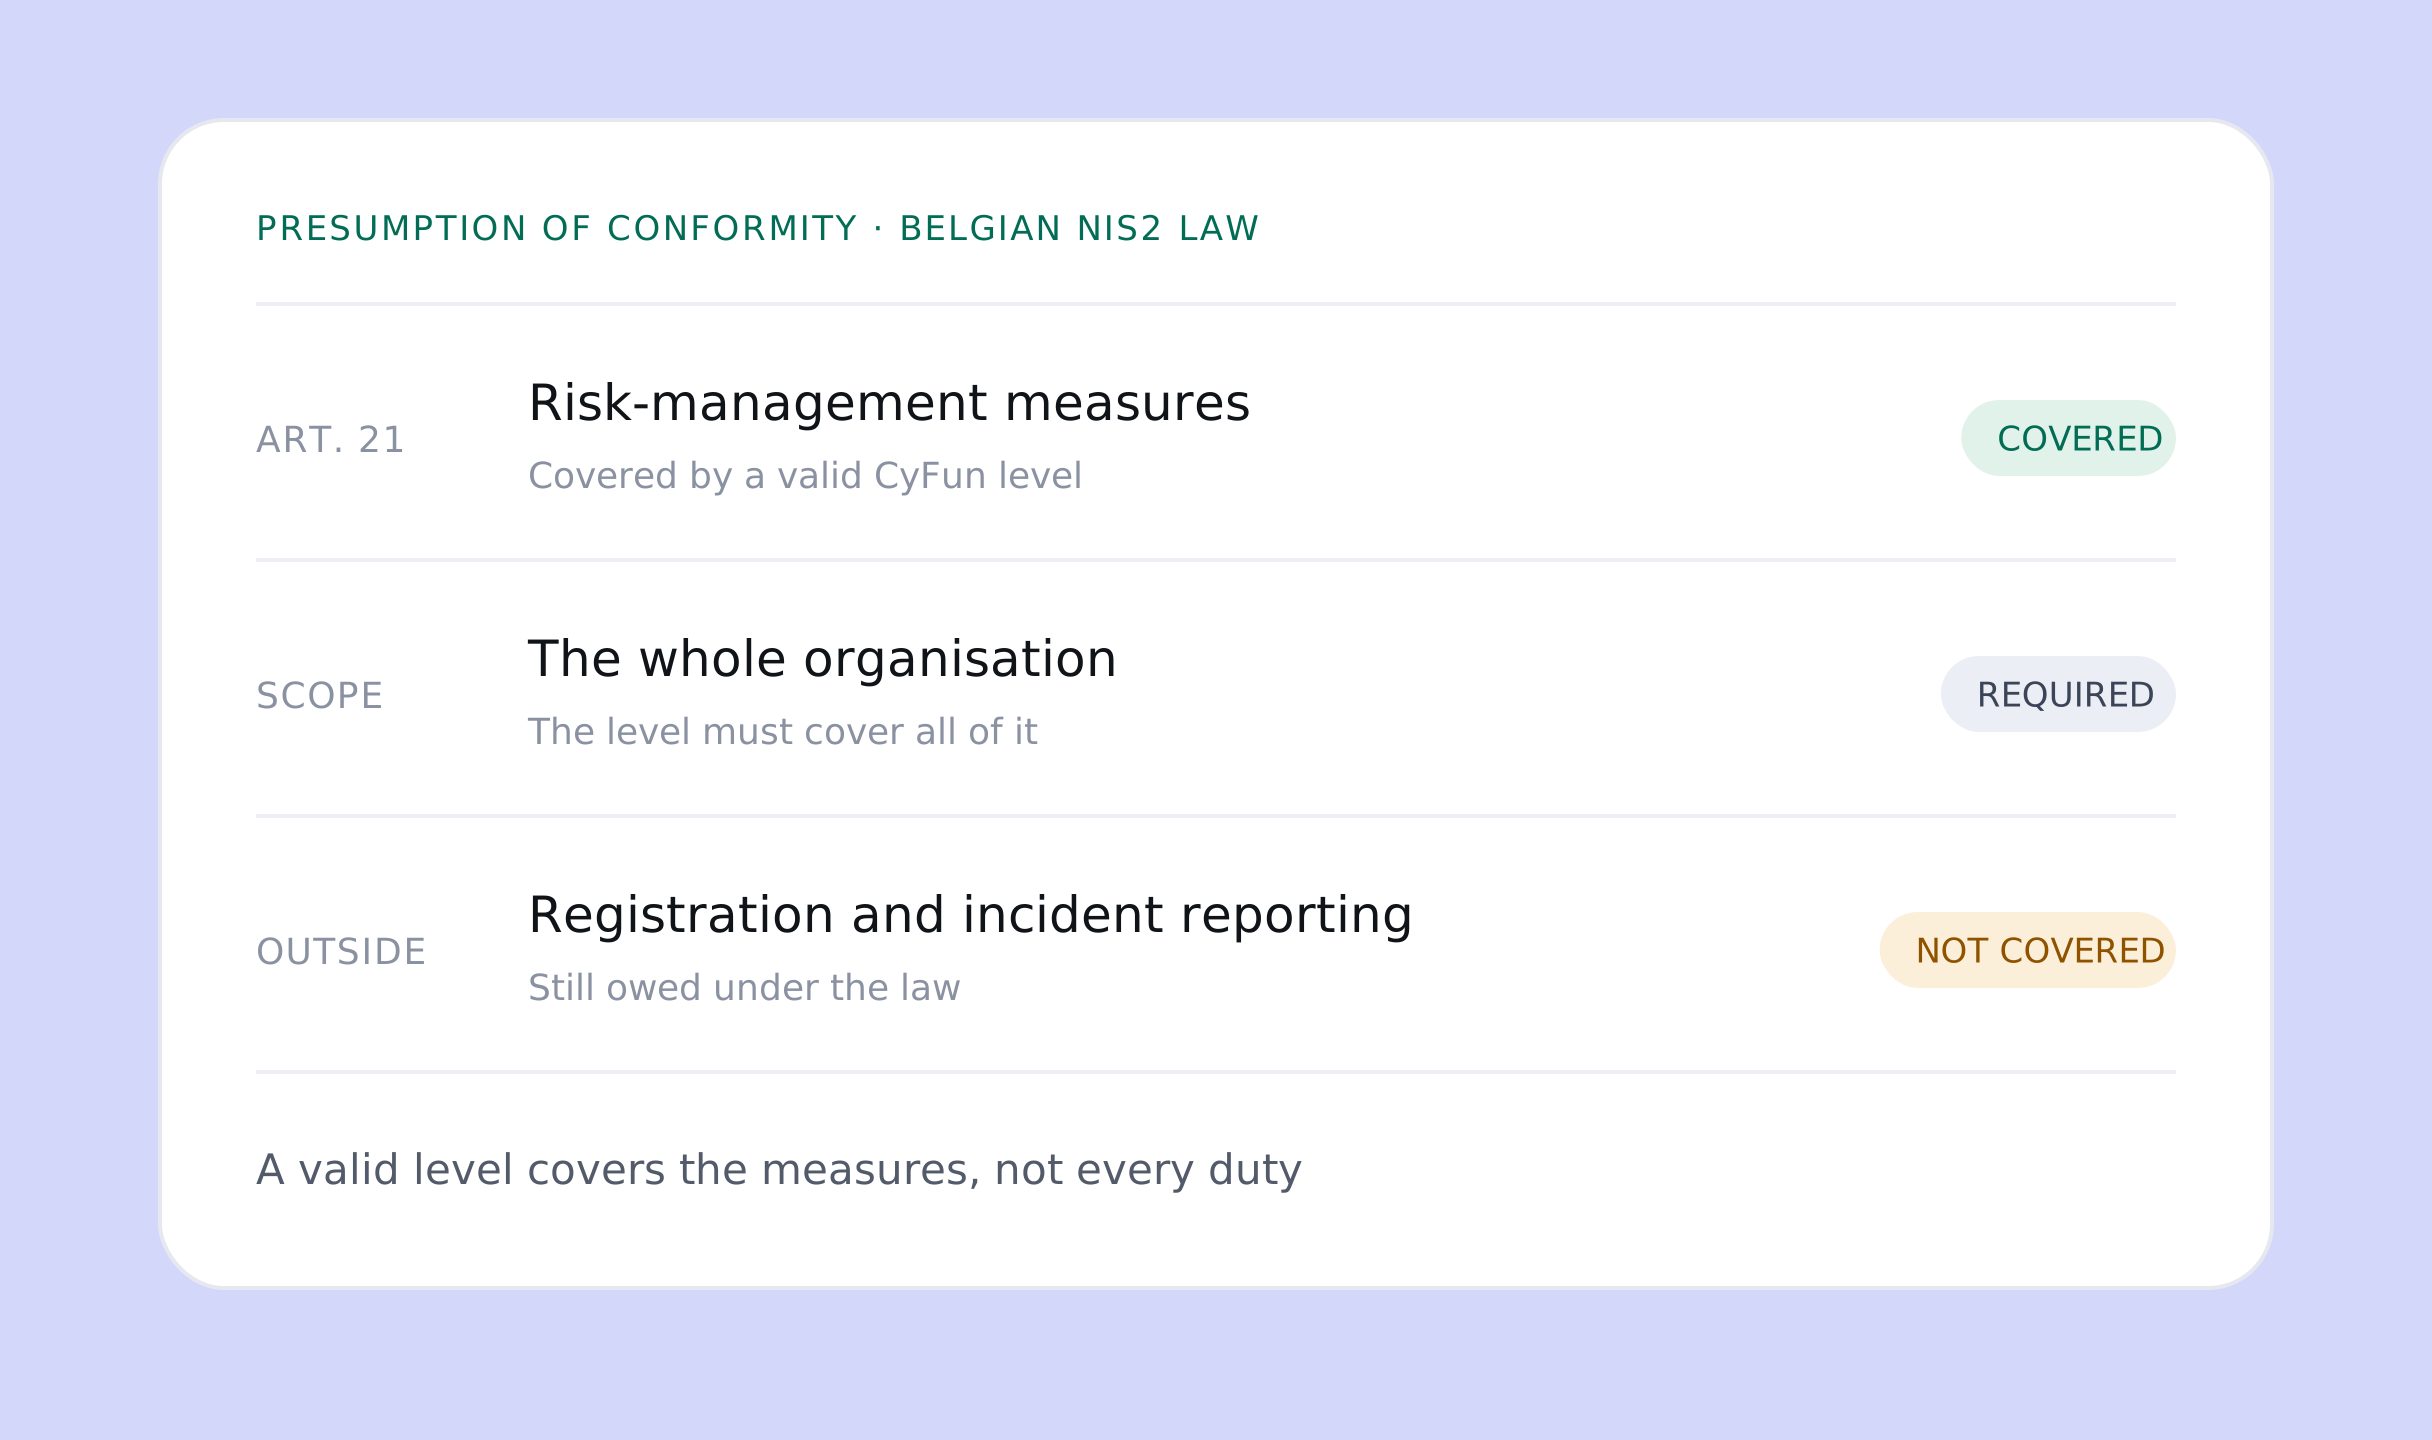
A valid level covers the Article 21 risk-management measures in Belgium’s NIS2 law, as long as its scope covers the whole organisation. Registration and incident reporting sit outside it.
How Montro helps
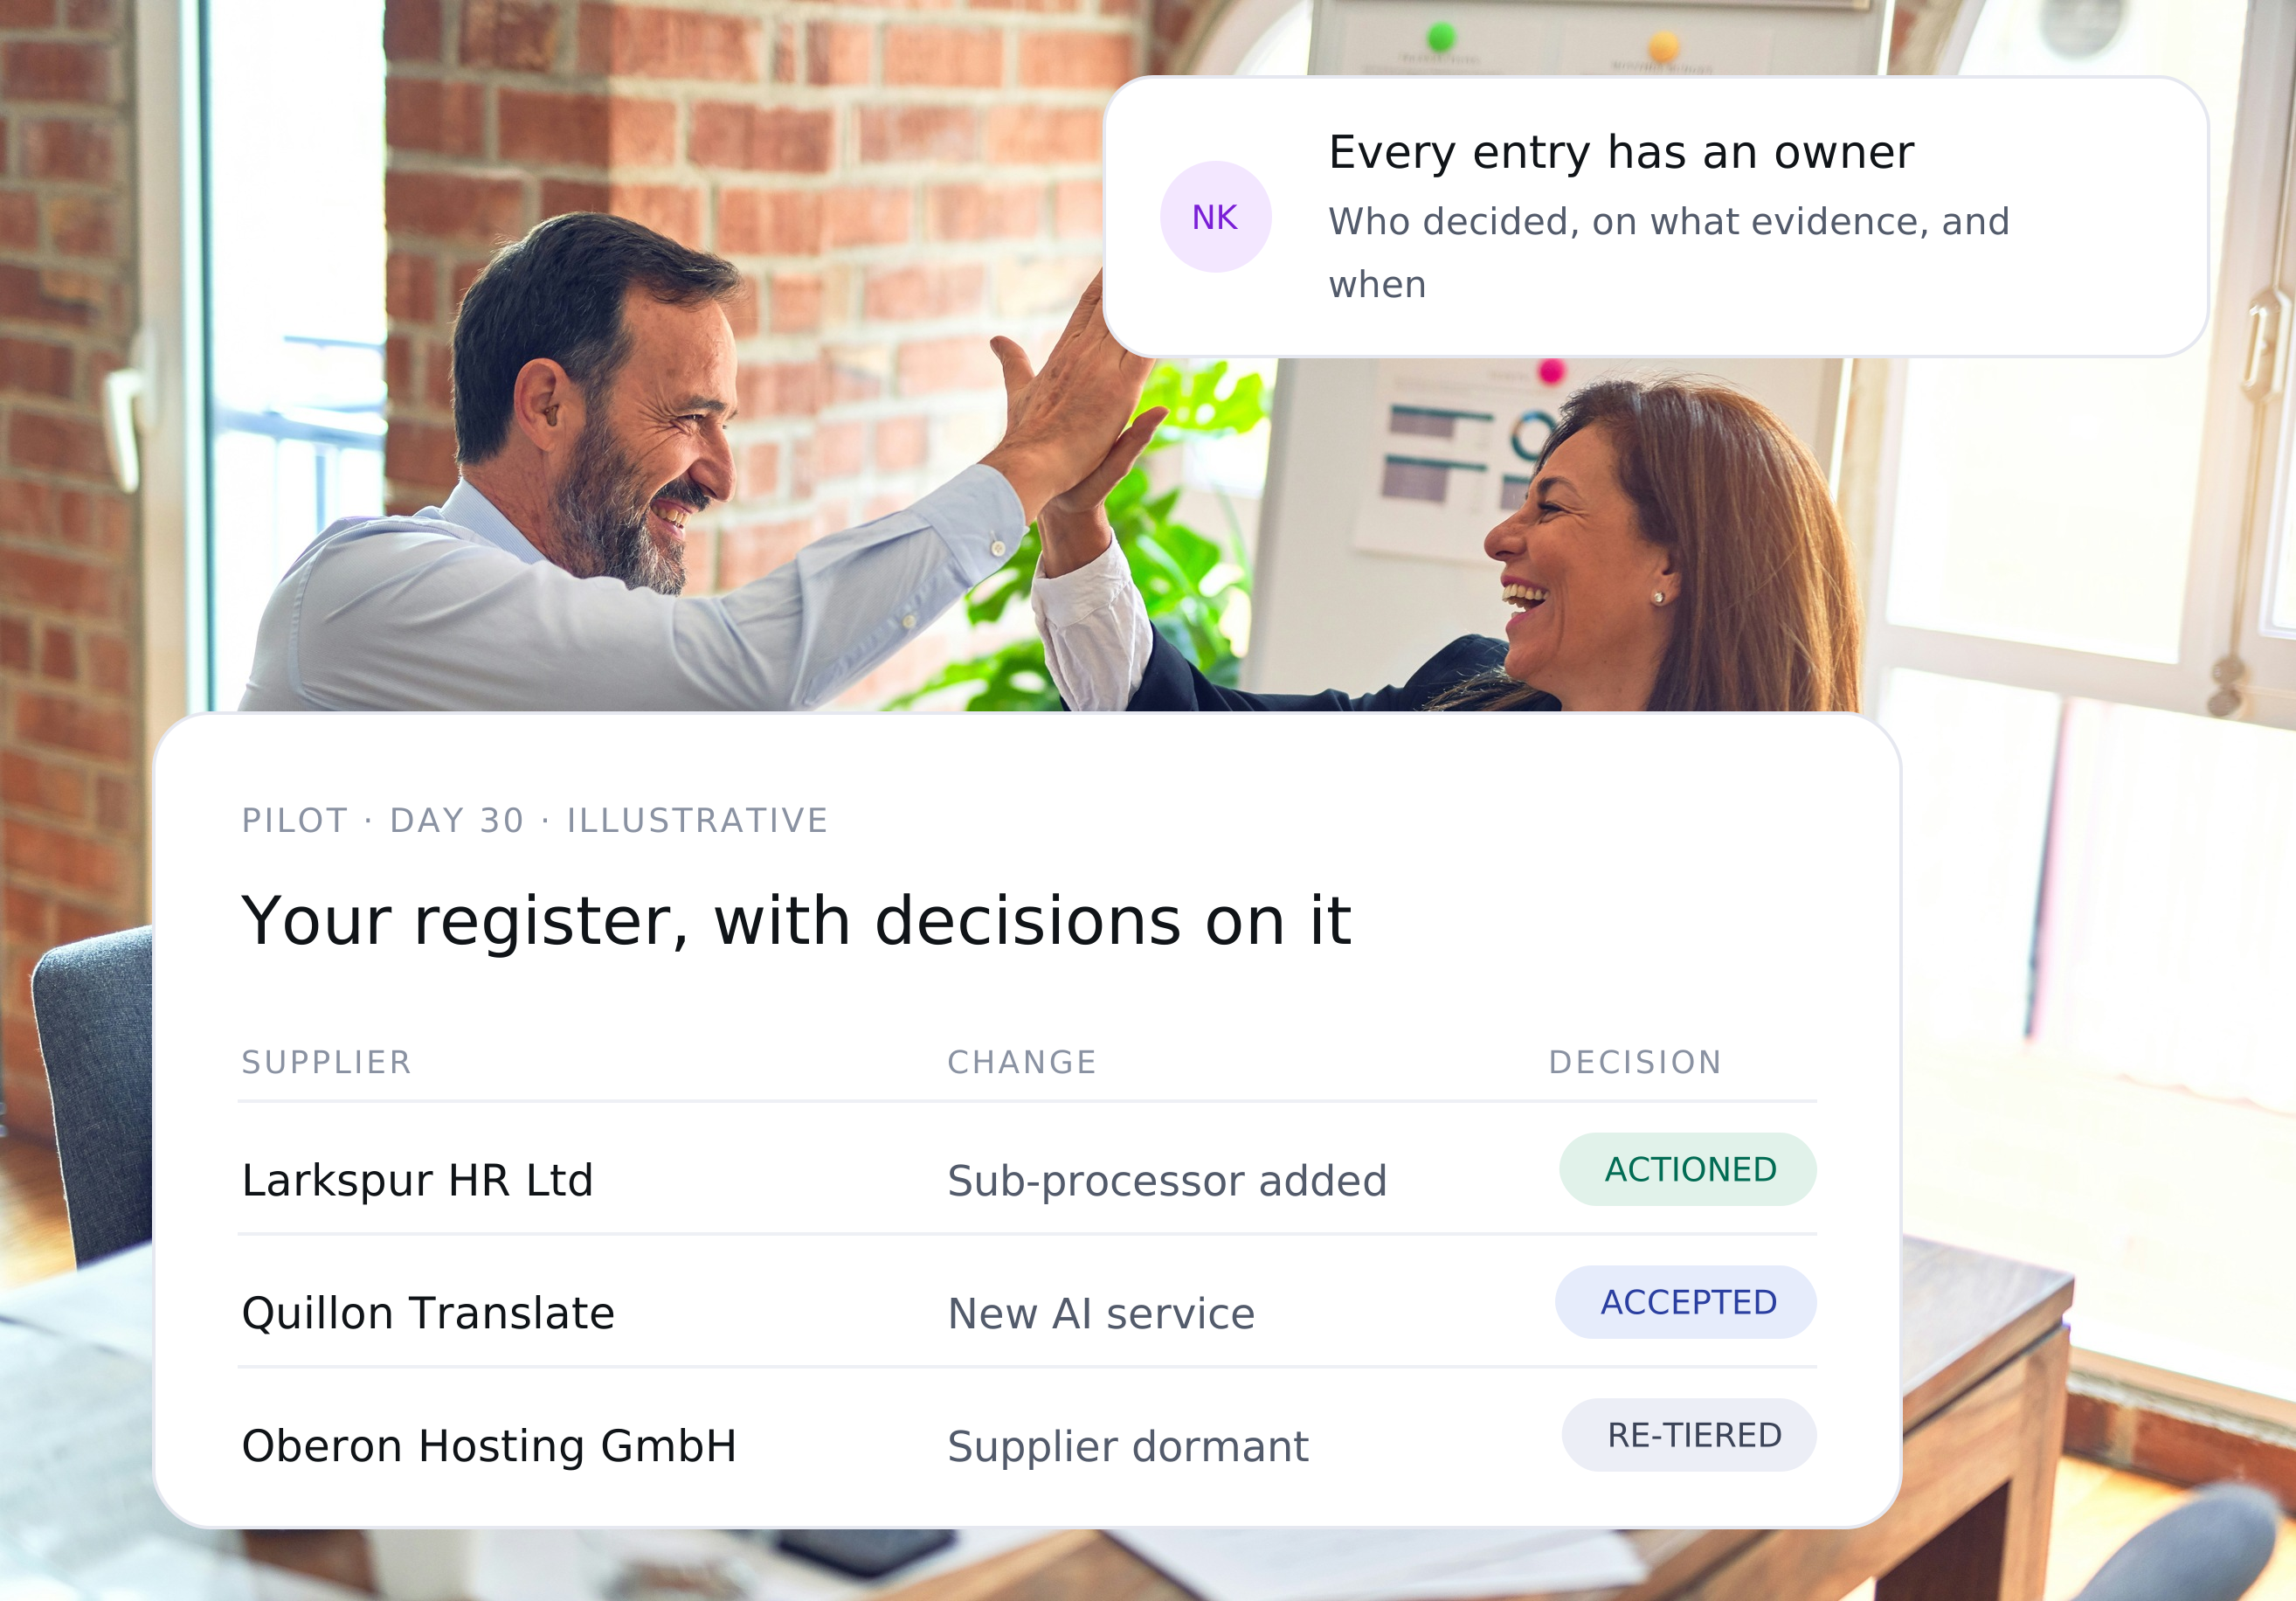
CyFun takes its supply chain measures from the Govern function of NIST CSF. Montro keeps the record those measures rely on, from the suppliers you depend on to the decisions taken on each.
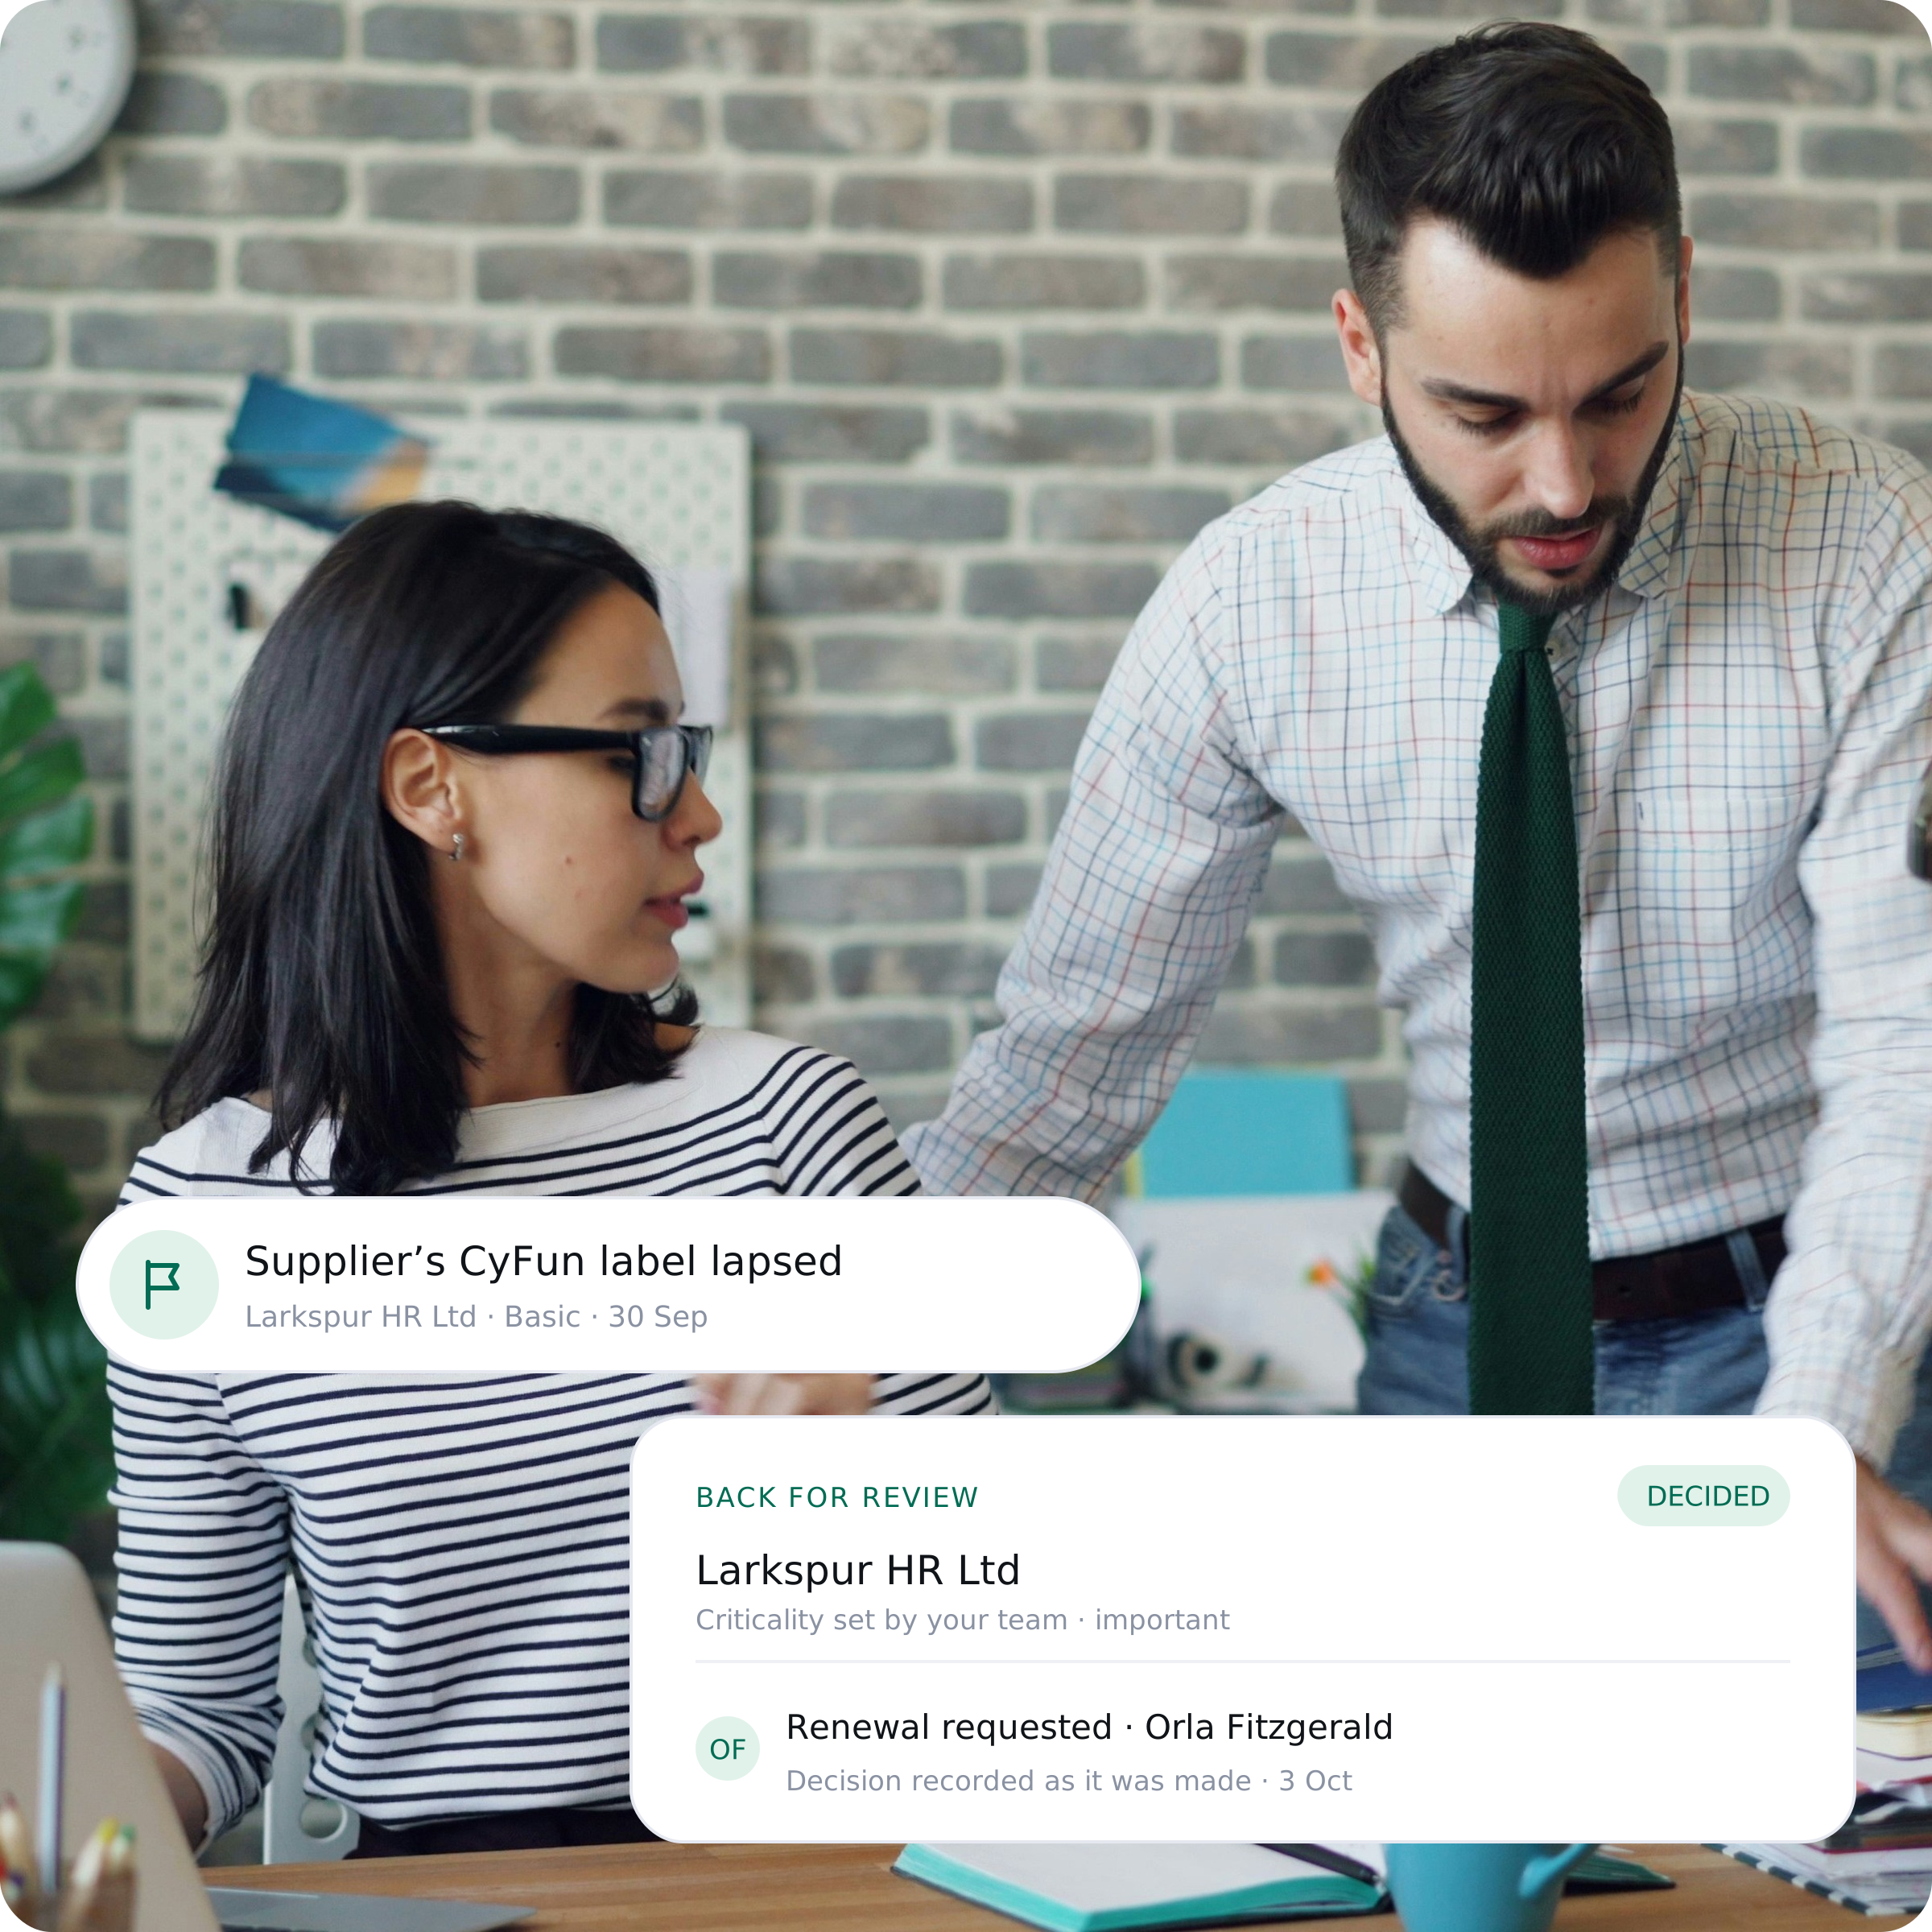
Each supplier in the register carries an owner and a criticality your team sets, so measures can be applied where they matter most.
When a supplier holds a CyFun label or an ISO 27001 certificate, its level and expiry sit with its entry, and a lapse comes back to your team for review.
CyFun looks at what is documented and what is actually done. Each supplier decision is recorded as it’s made, so the register shows the practice behind the policy.
What you get
Supplier evidence ready for verification or certification.
Reasoning
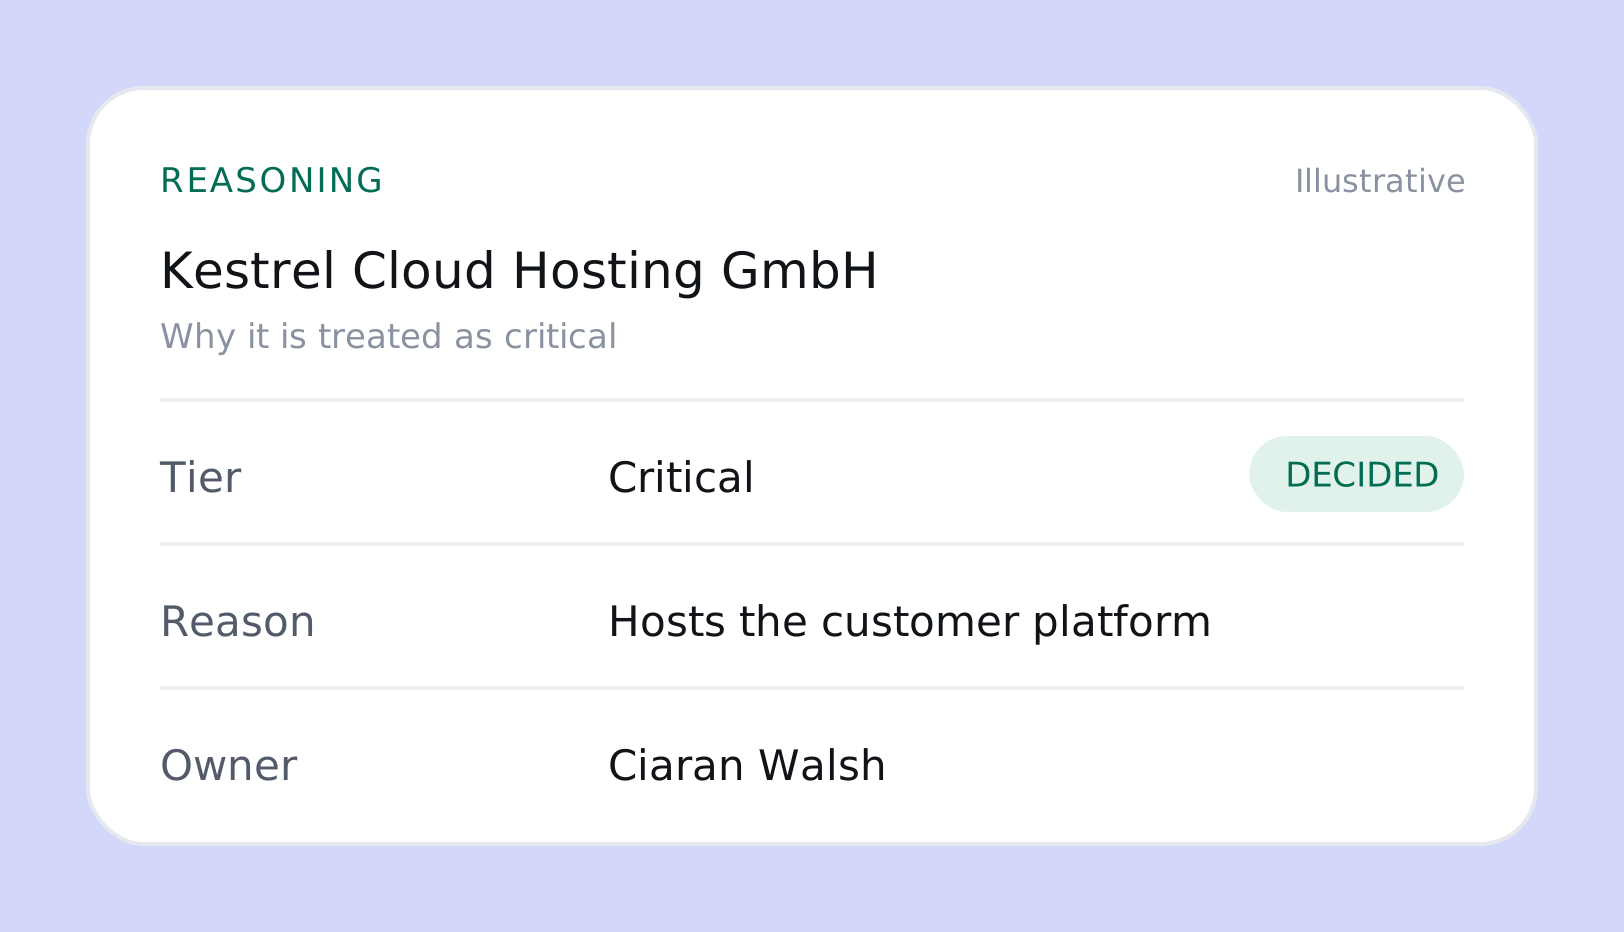
Why a supplier is treated as critical, or not, is recorded with it, so the risk-based choices behind your measures can be explained.
Across borders
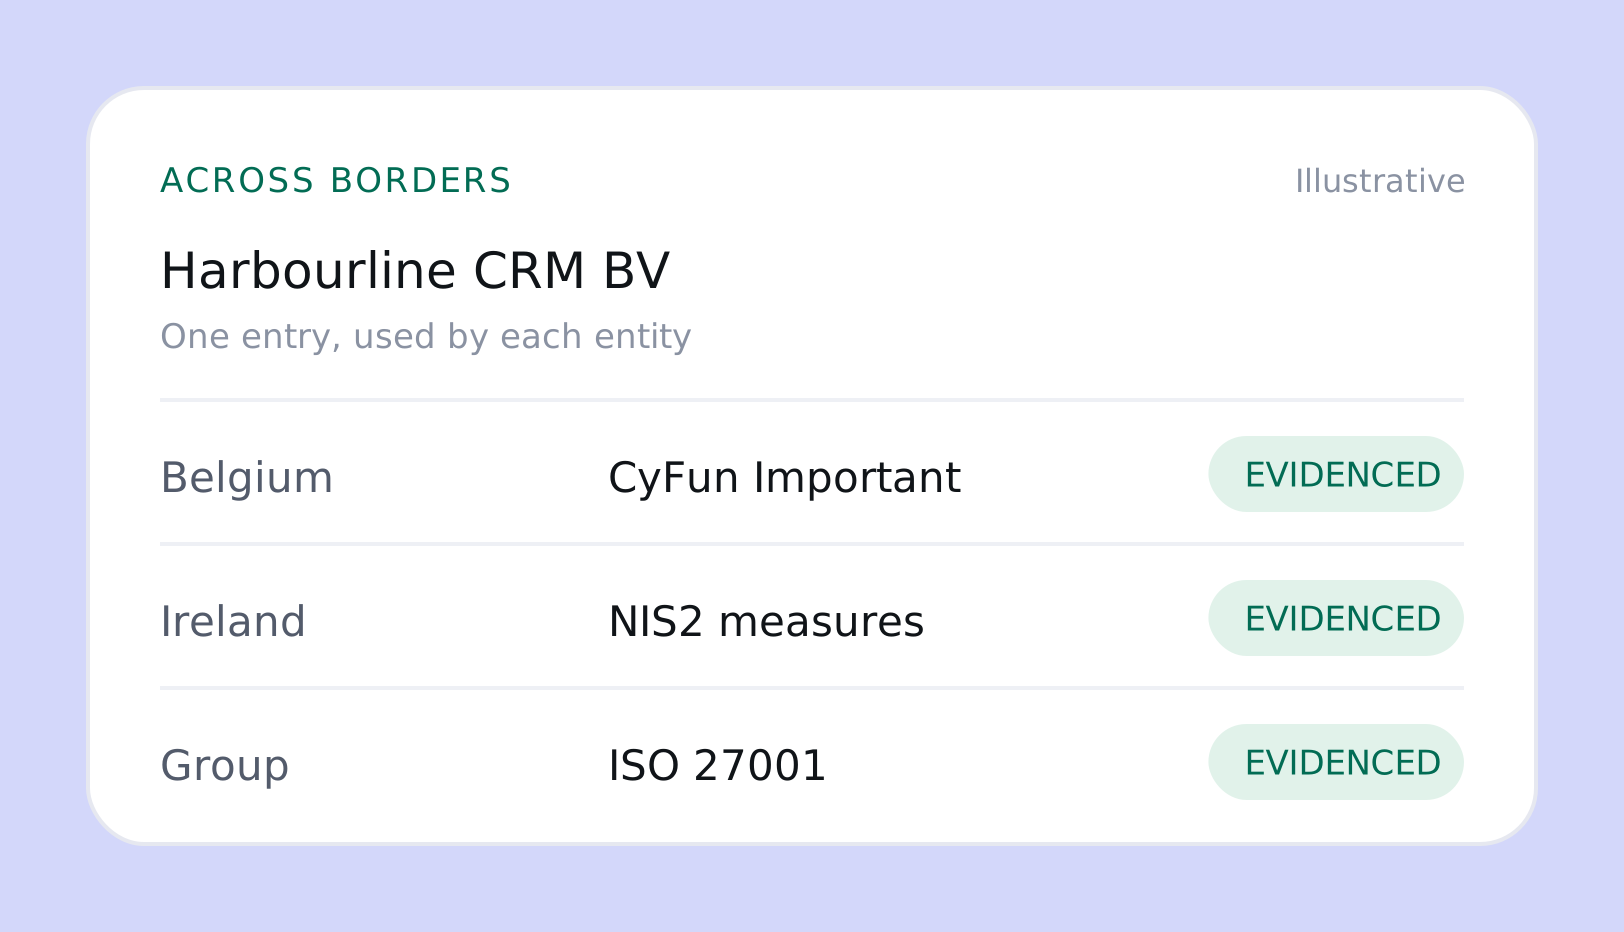
If you operate in Belgium and elsewhere, the same supplier entries can support CyFun alongside ISO 27001 and other countries’ NIS2 rules.
Reassessment
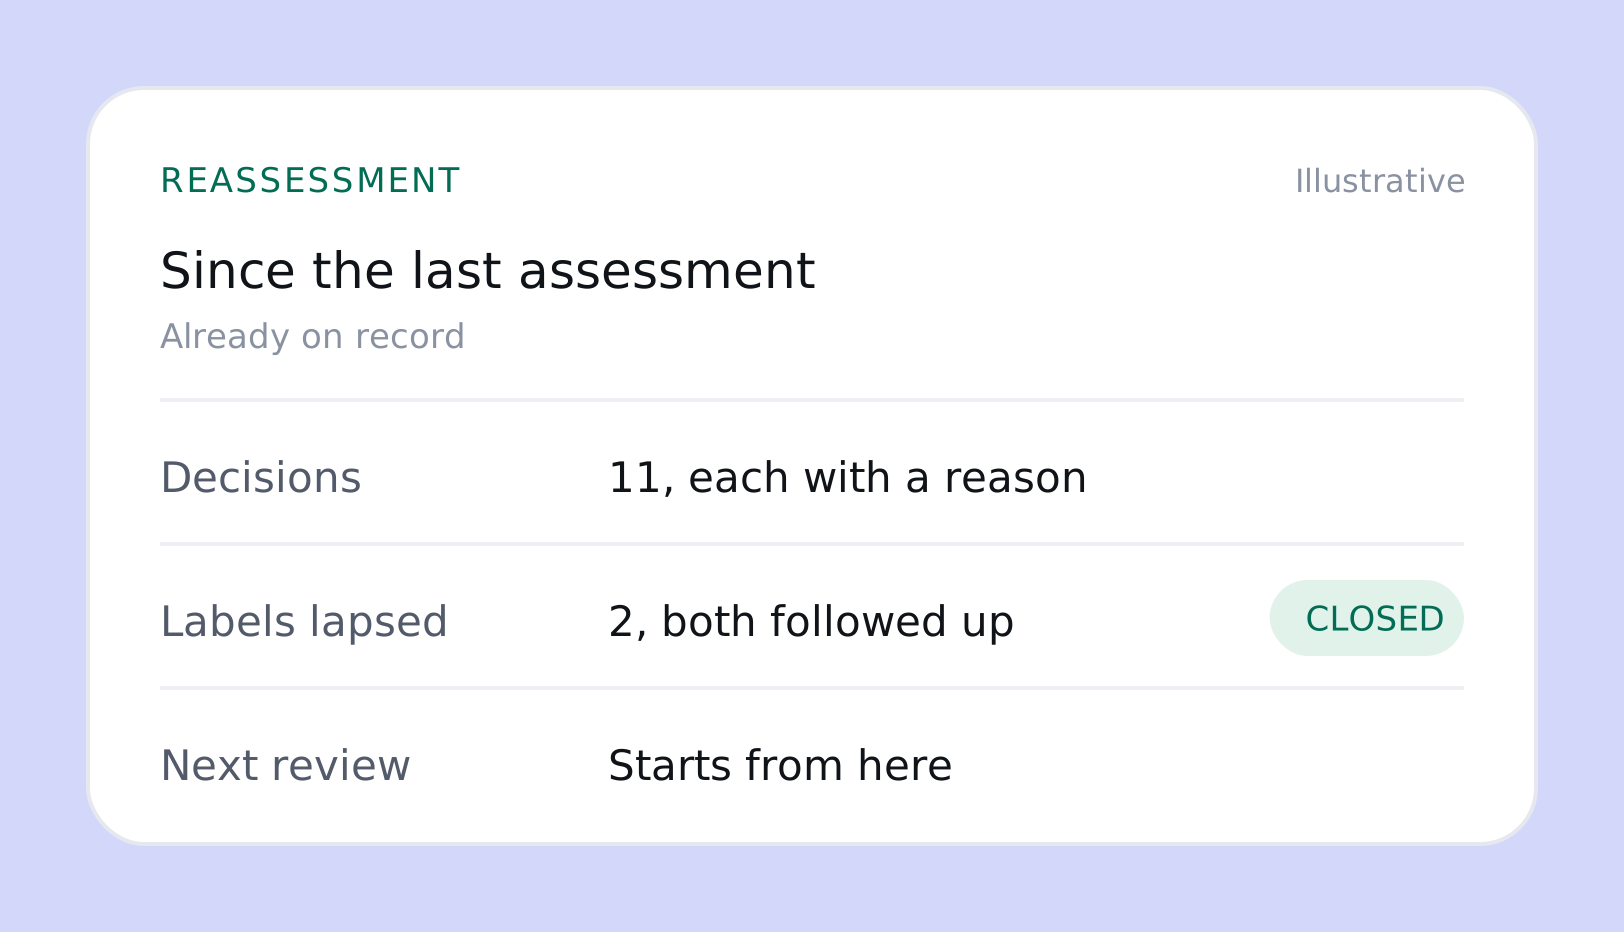
Assessments repeat. Decisions taken since the last one are already on record, so the next review starts where the last one ended.
Assurance levels
Basic
For any organisation, using measures most already have. The CCB recommends it for every company in the supply chain of a NIS2 entity.
Important
Built for attackers with common skills and resources. The level most important entities aim for.
Essential
Built for attackers with extensive skills and resources. Essential entities work towards certification at this level.
Questions about CyFun, and how Montro supports its supply chain measures.
Keep reading
CyFun is built from the frameworks below, and the same supplier evidence carries across.
Third-party records are becoming decision logs. The firms that get this right will be the ones that can show who decided, on what evidence, and when.
A read-only connection, about an hour to set up, and a named person who can say yes to a decision.
Priced to scope — never per seat, never per supplier. Upgrade only when the evidence earns it.