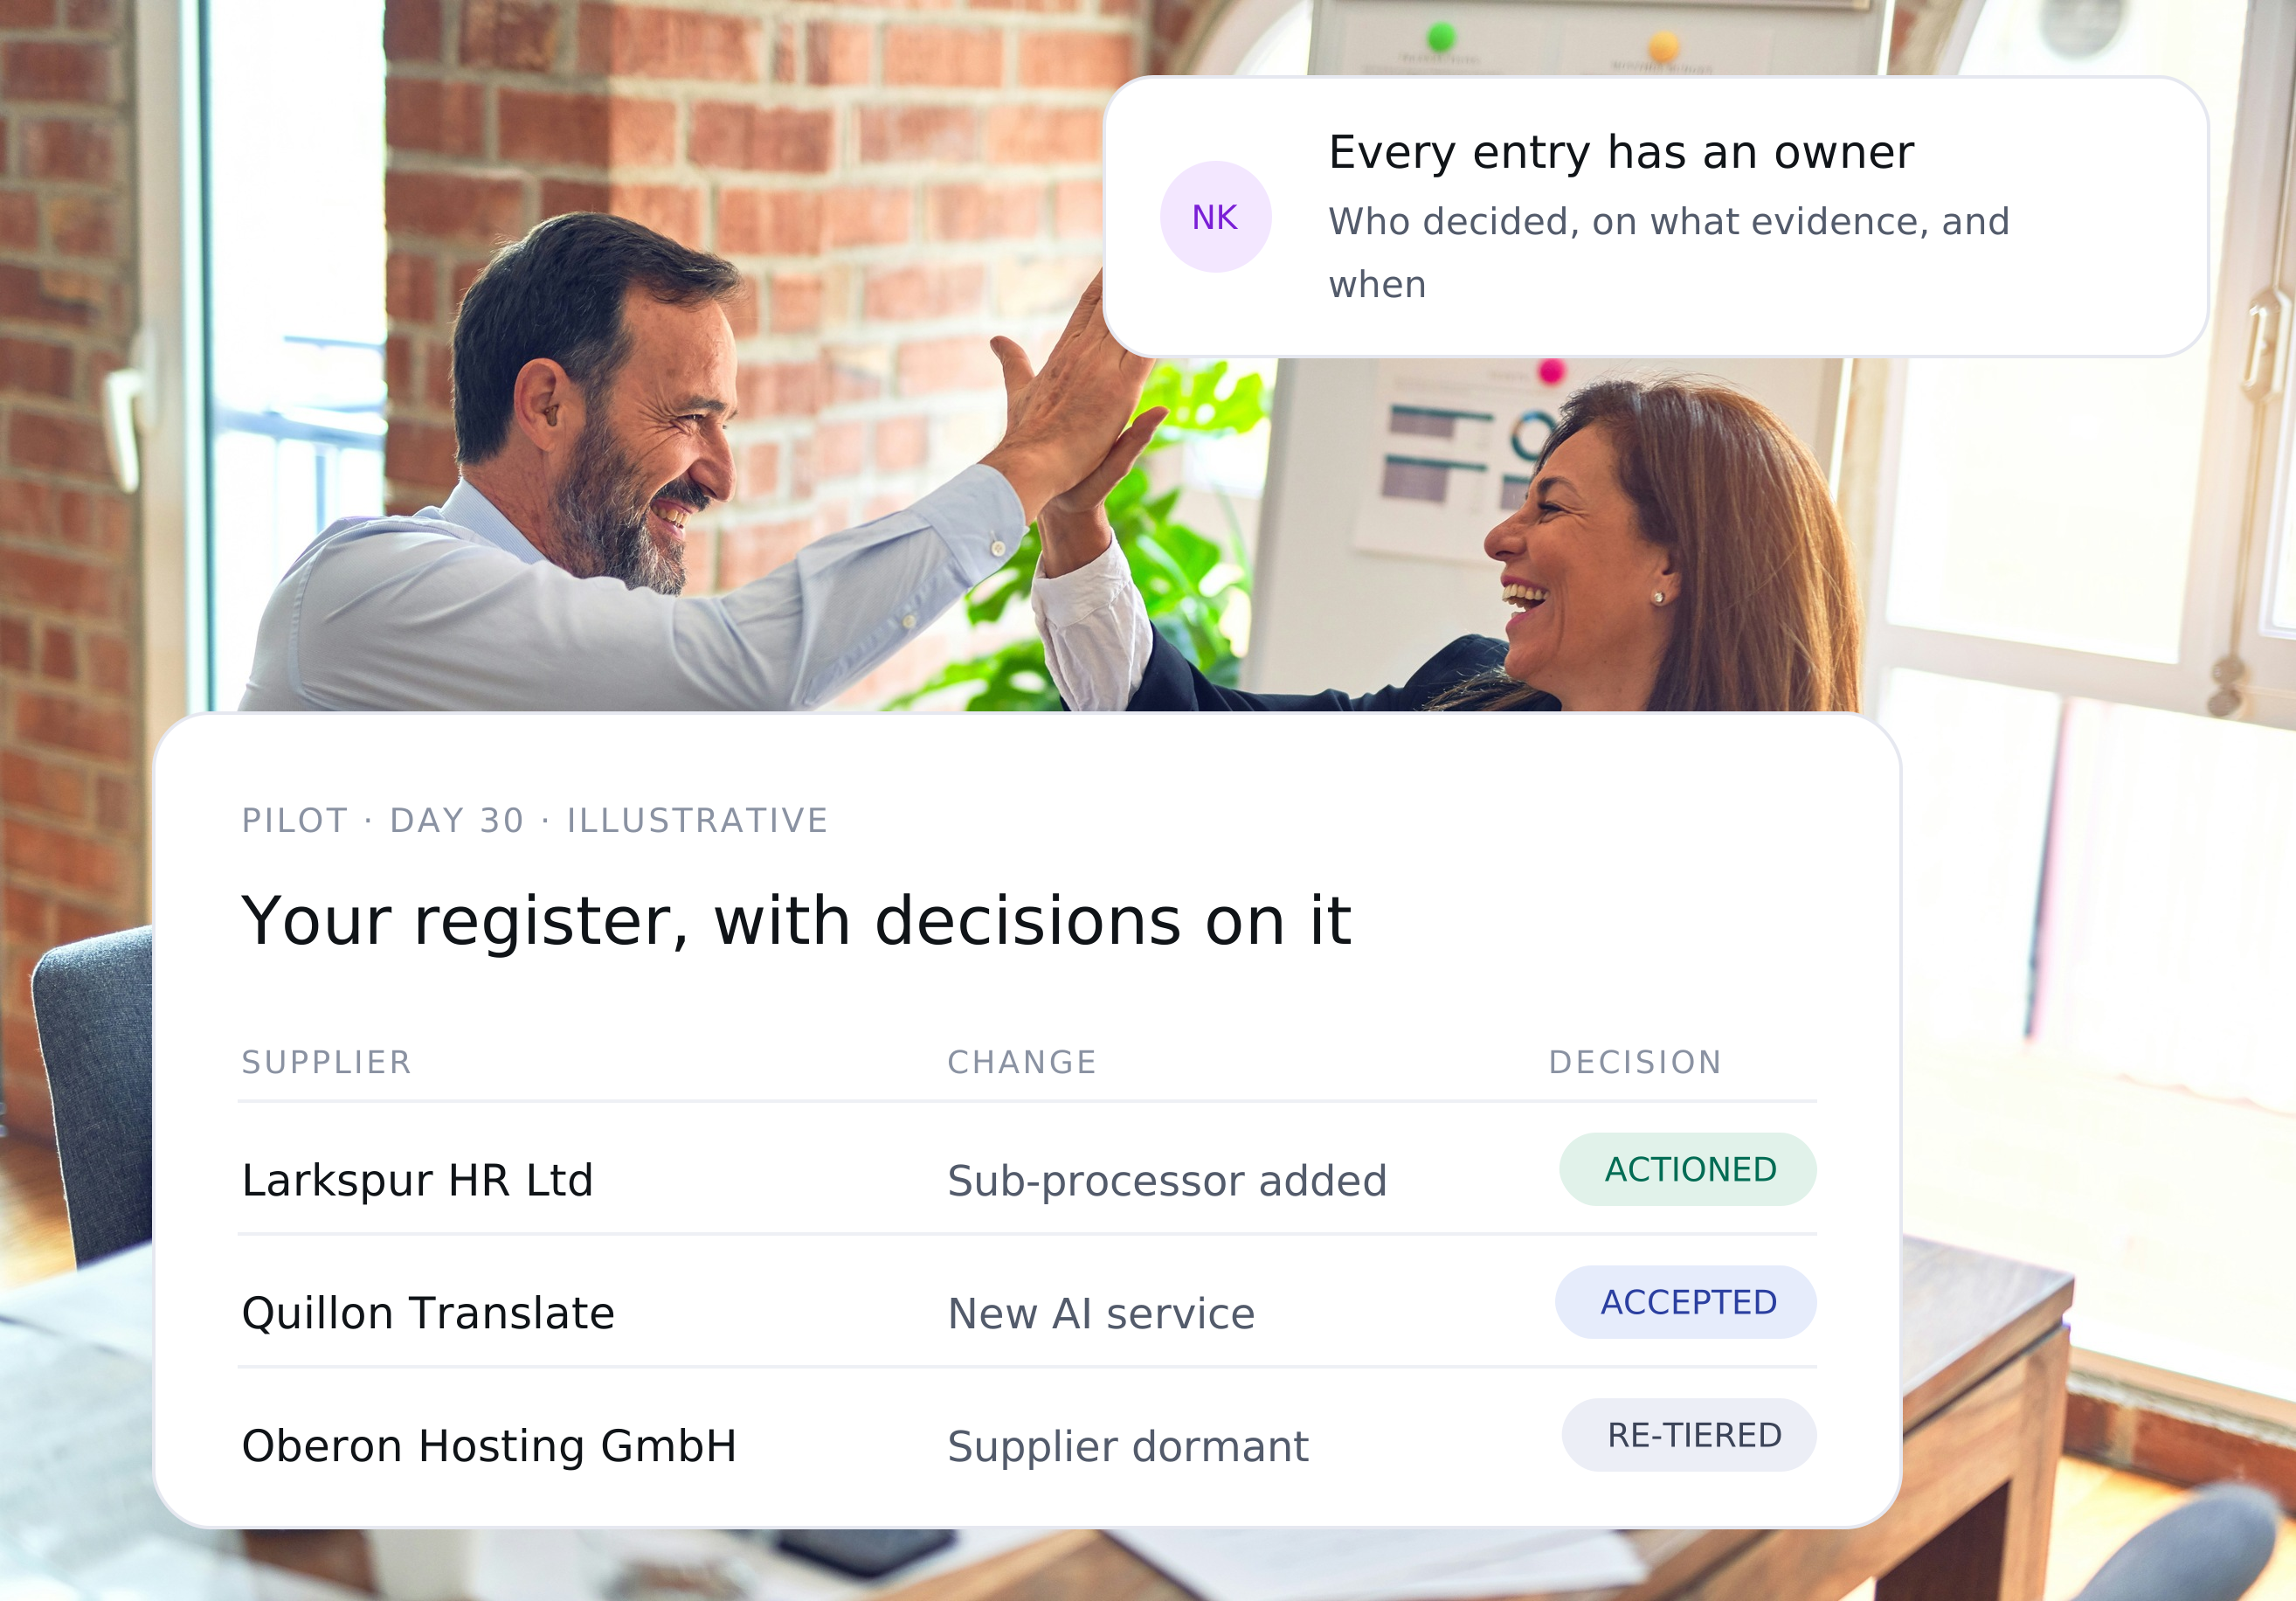
Day 1: connect in under an hour
Read-only links to sign-in, directory and finance. Nothing to install unless you add the optional browser extension.
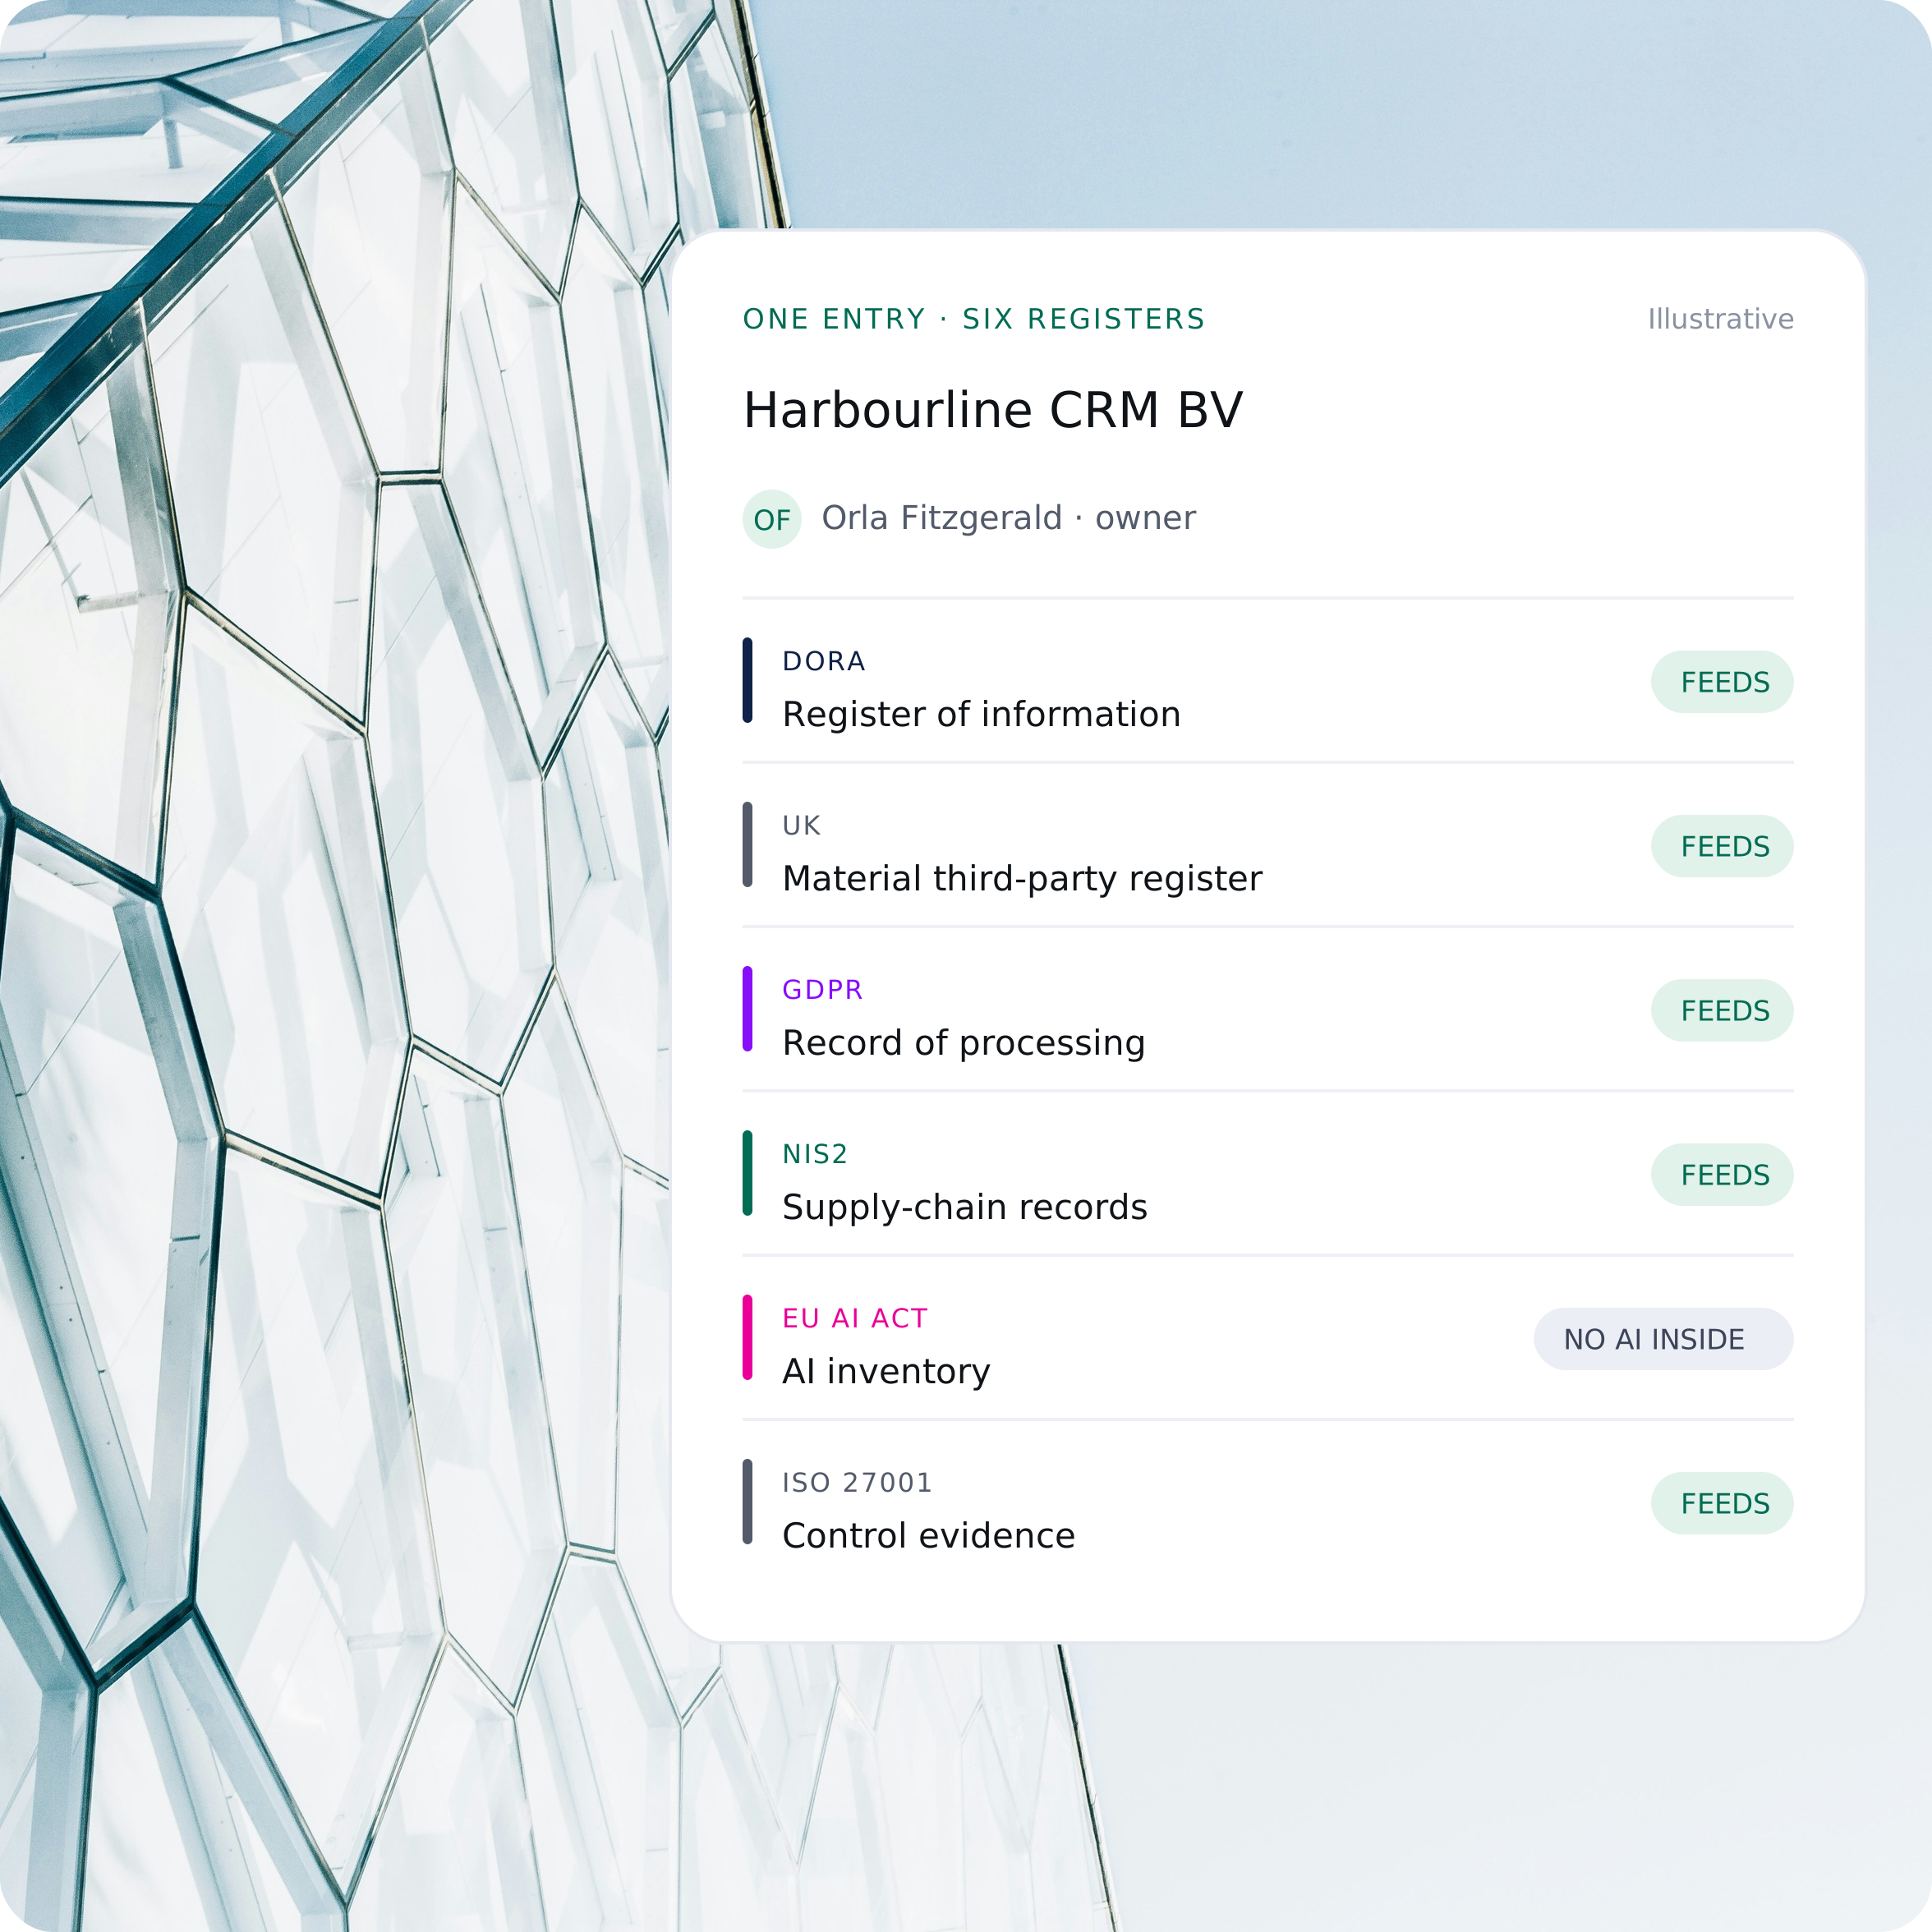
Third-party and AI rules now overlap. DORA, the UK's new third-party rules, GDPR, NIS2 and the EU AI Act each ask for their own record, often about the same suppliers, and ISO 27001 asks for evidence of the controls behind them.
Montro keeps one entry for each supplier and feeds every register from it. Changes are raised with their source, the supplier confirms, and your team decides, so your registers agree with each other.
Framework
What each regulation asks you to keep, and what Montro does to keep it true.
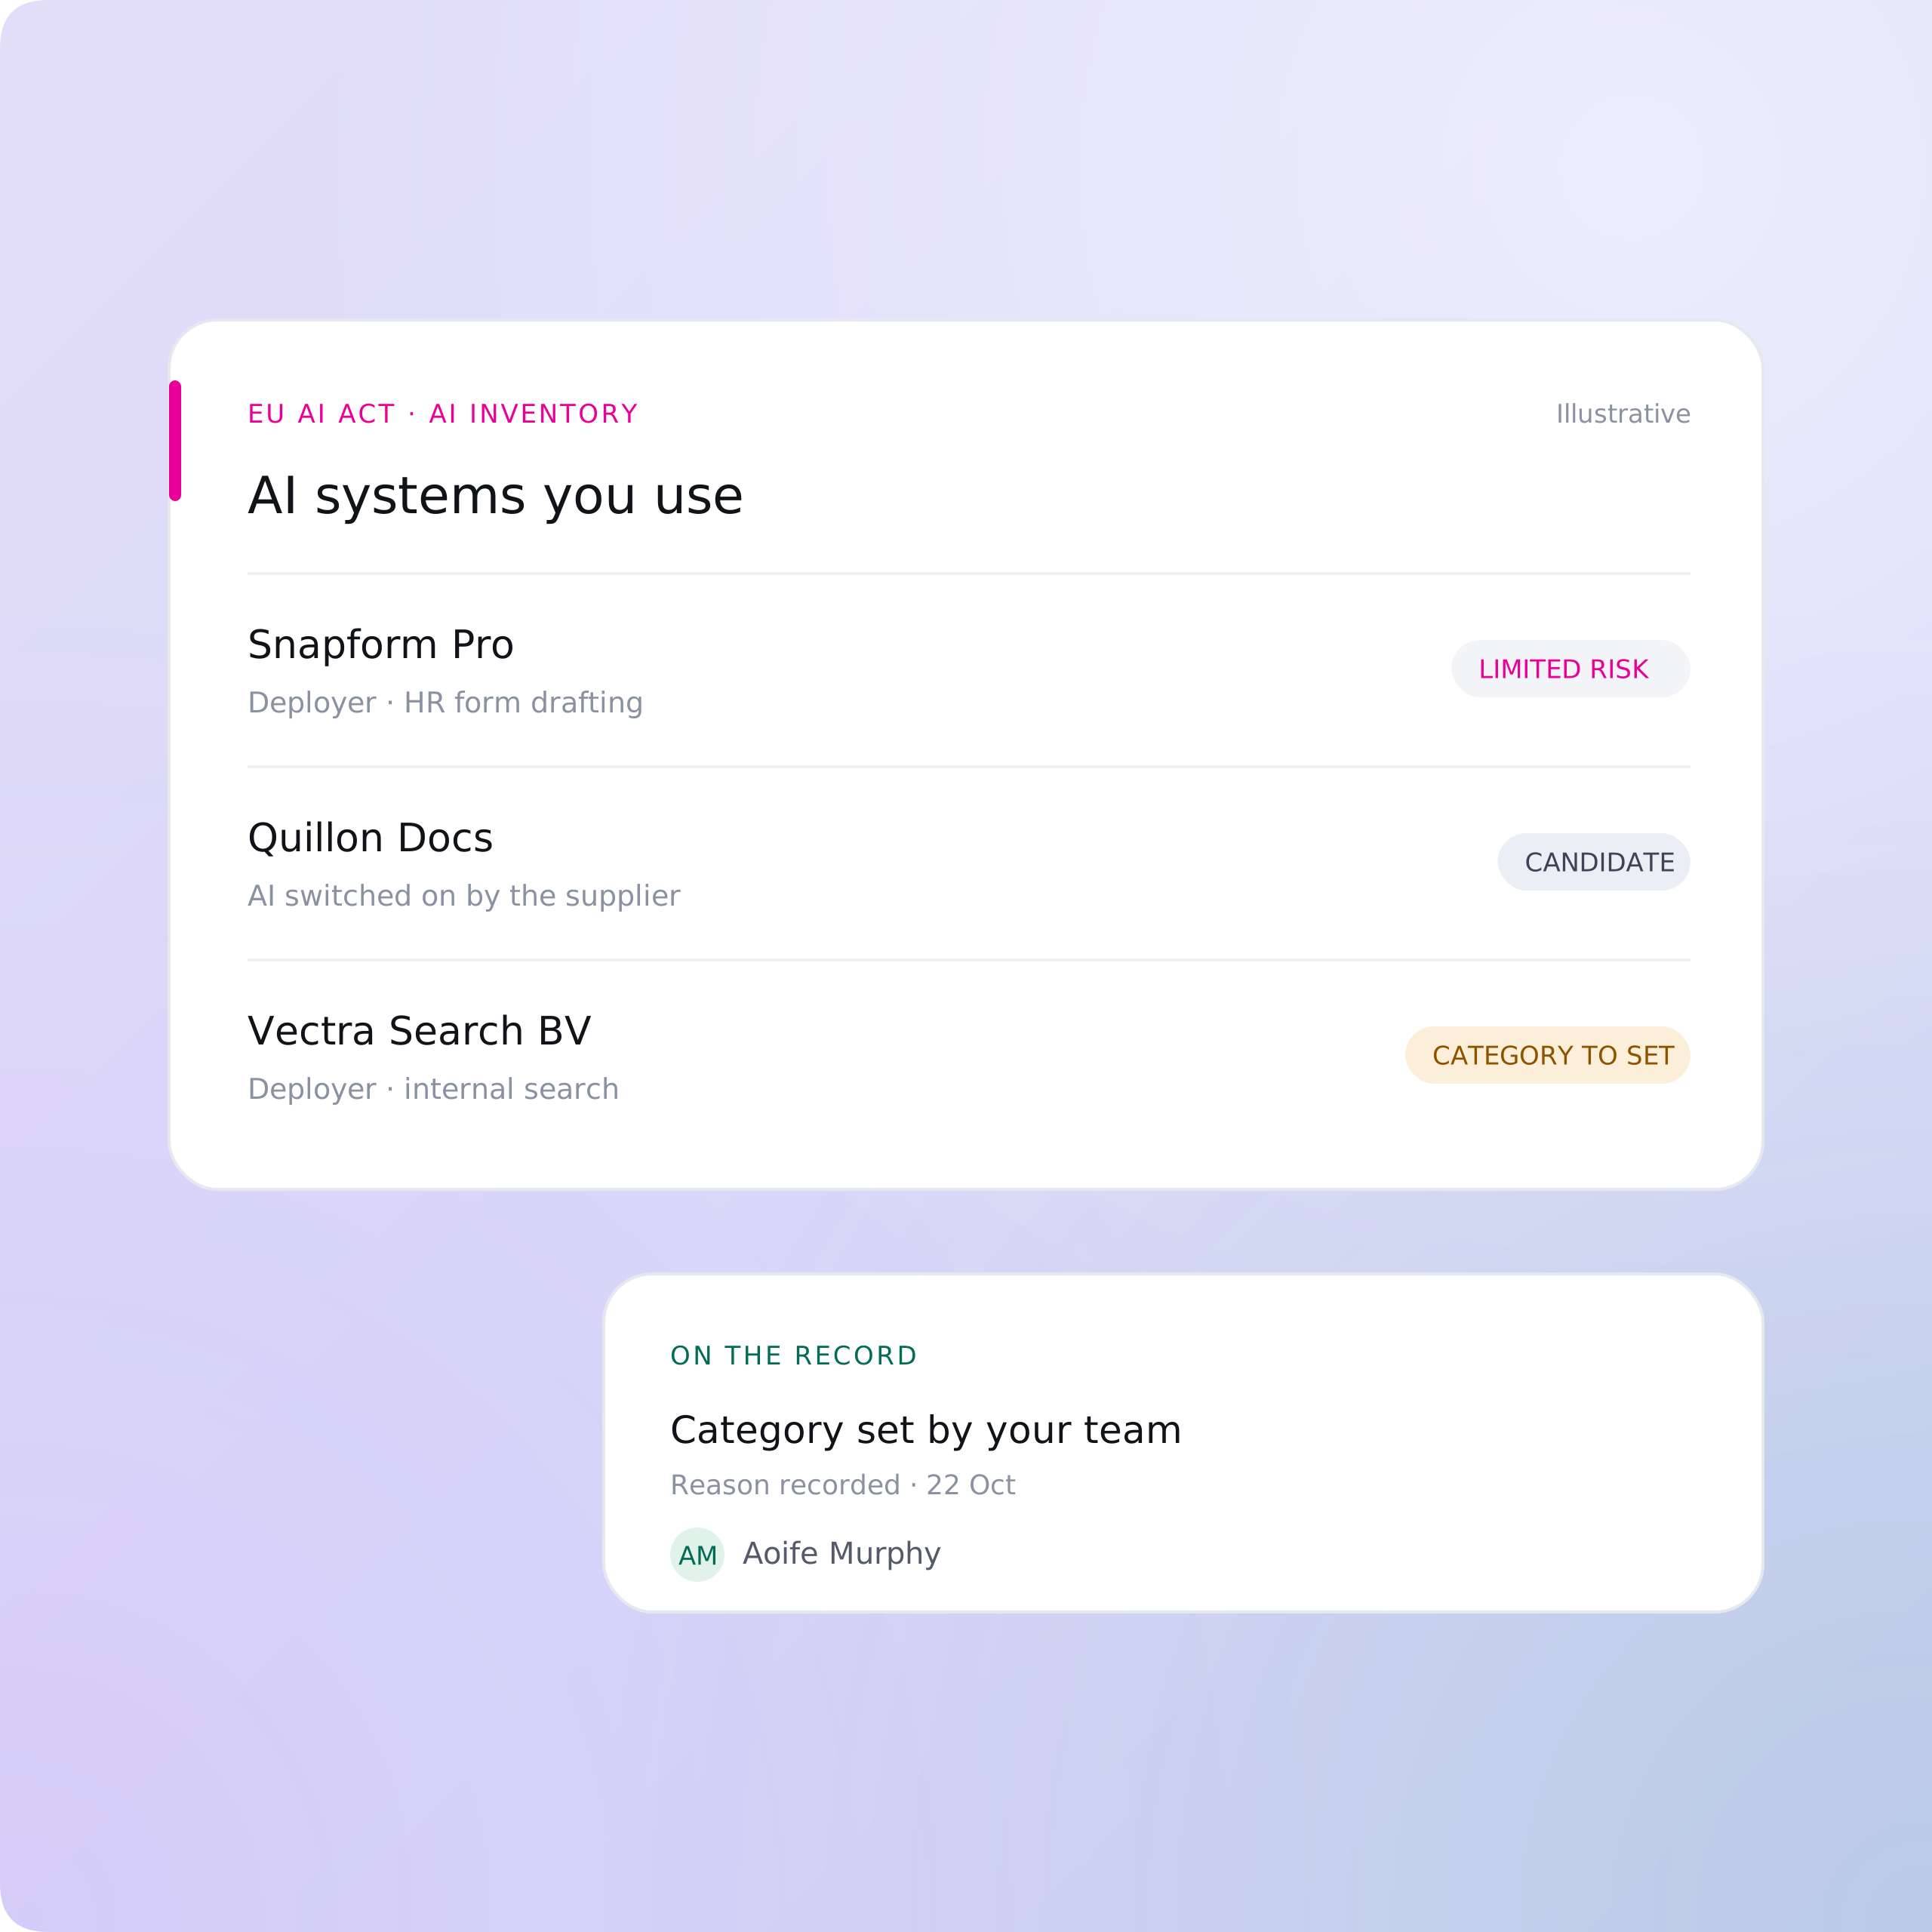
AI
A record of the AI systems you use, your role for each and the category your team sets. Montro brings in the tools it finds and keeps each decision with the entry.
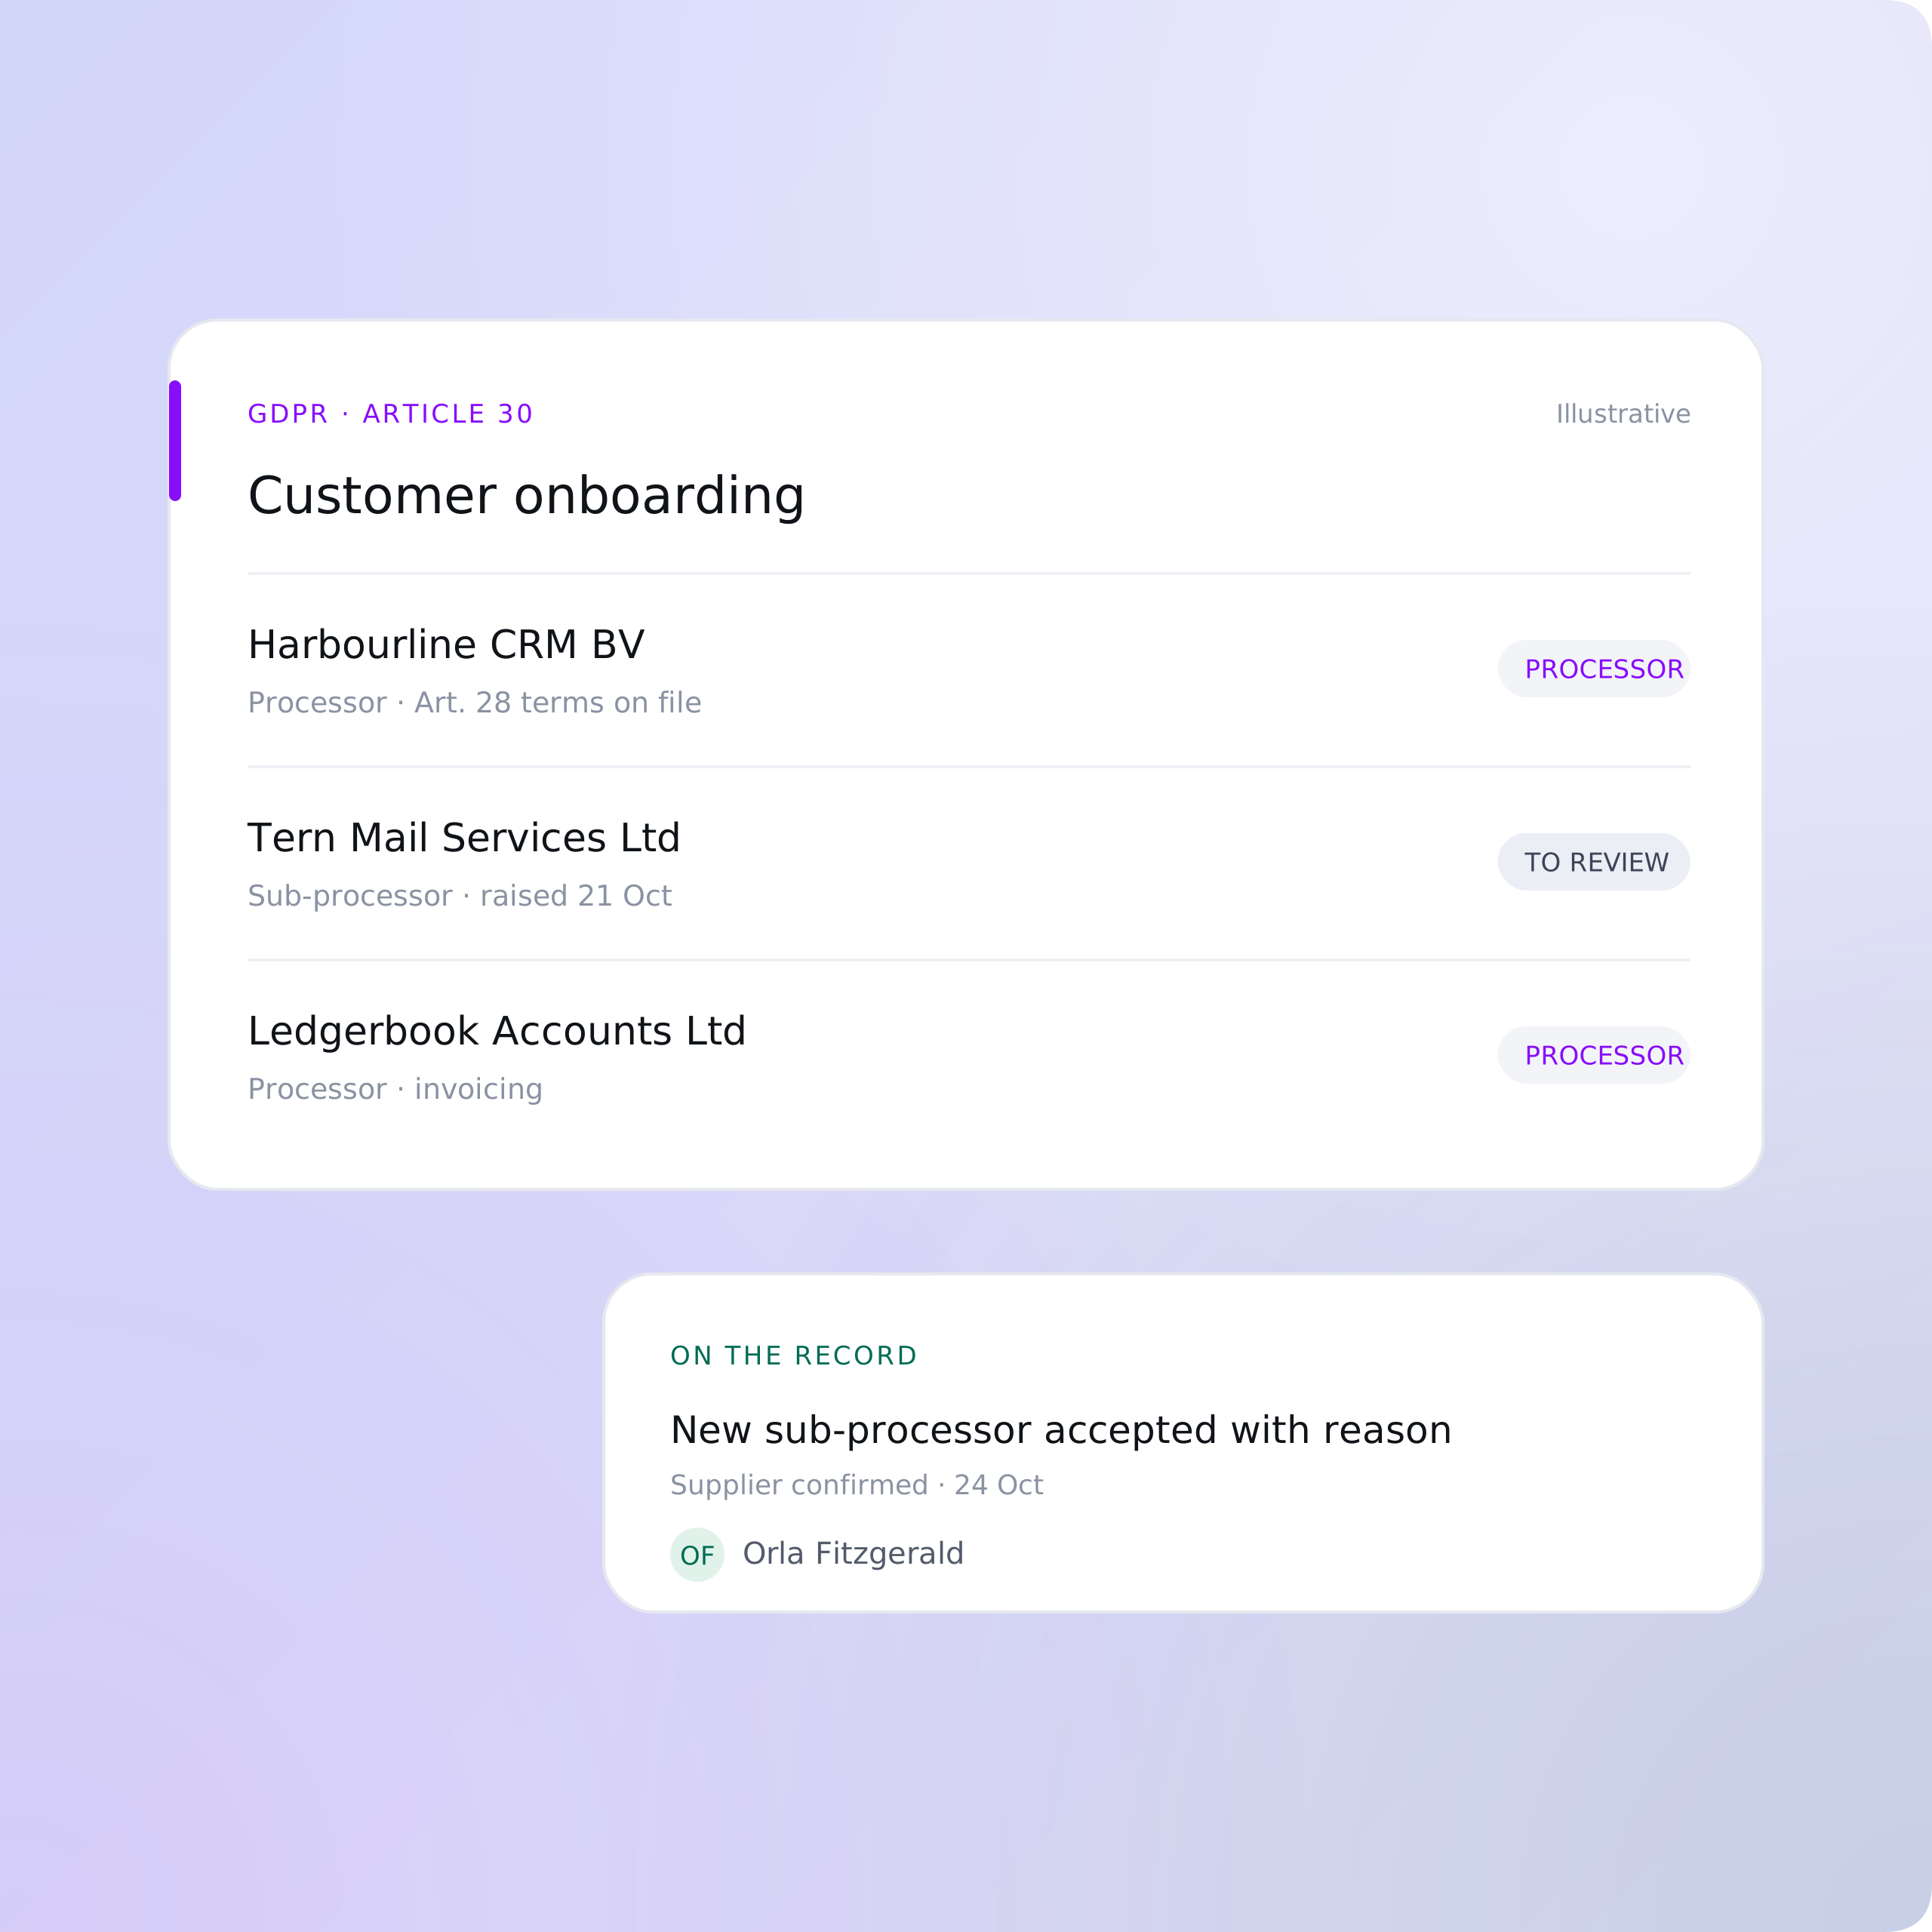
Processing
The Article 30 record, with processors and sub-processors linked to the activities they support. New sub-processors are raised for your team to review.
Third parties
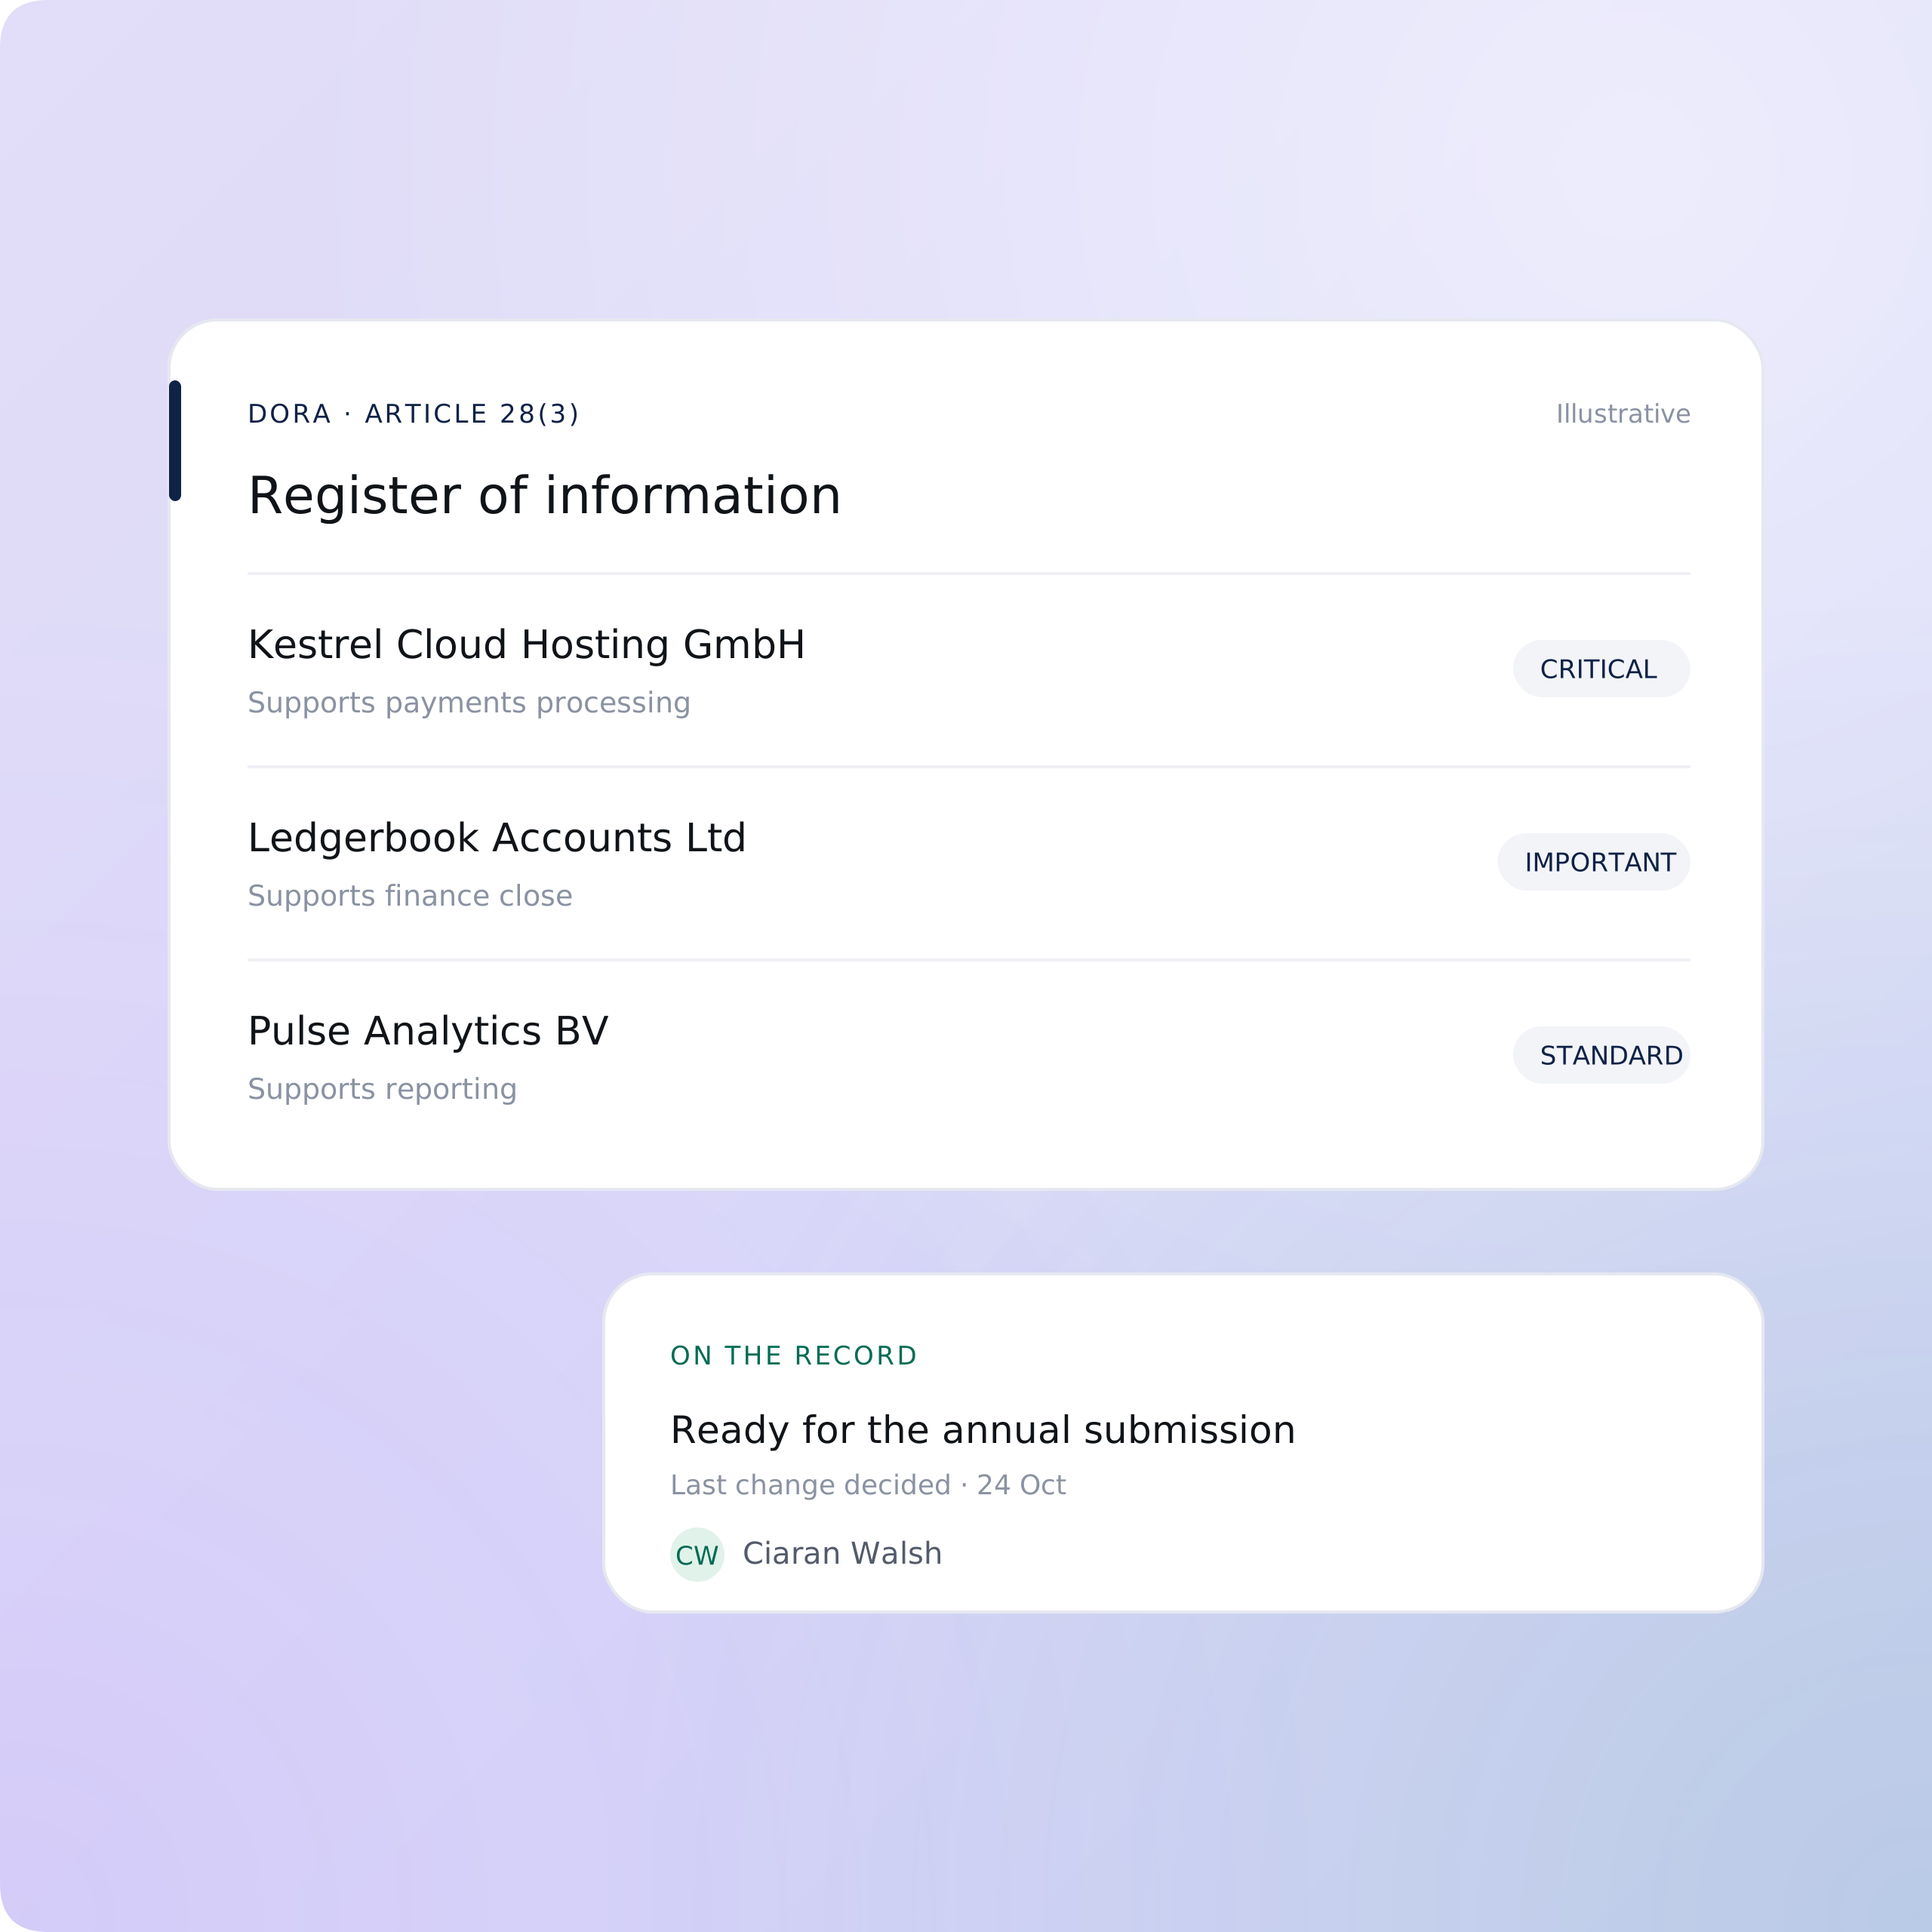
Only financial entities keep one. Montro raises supplier changes, so the register is up to date when it is submitted each year.
Supply chain
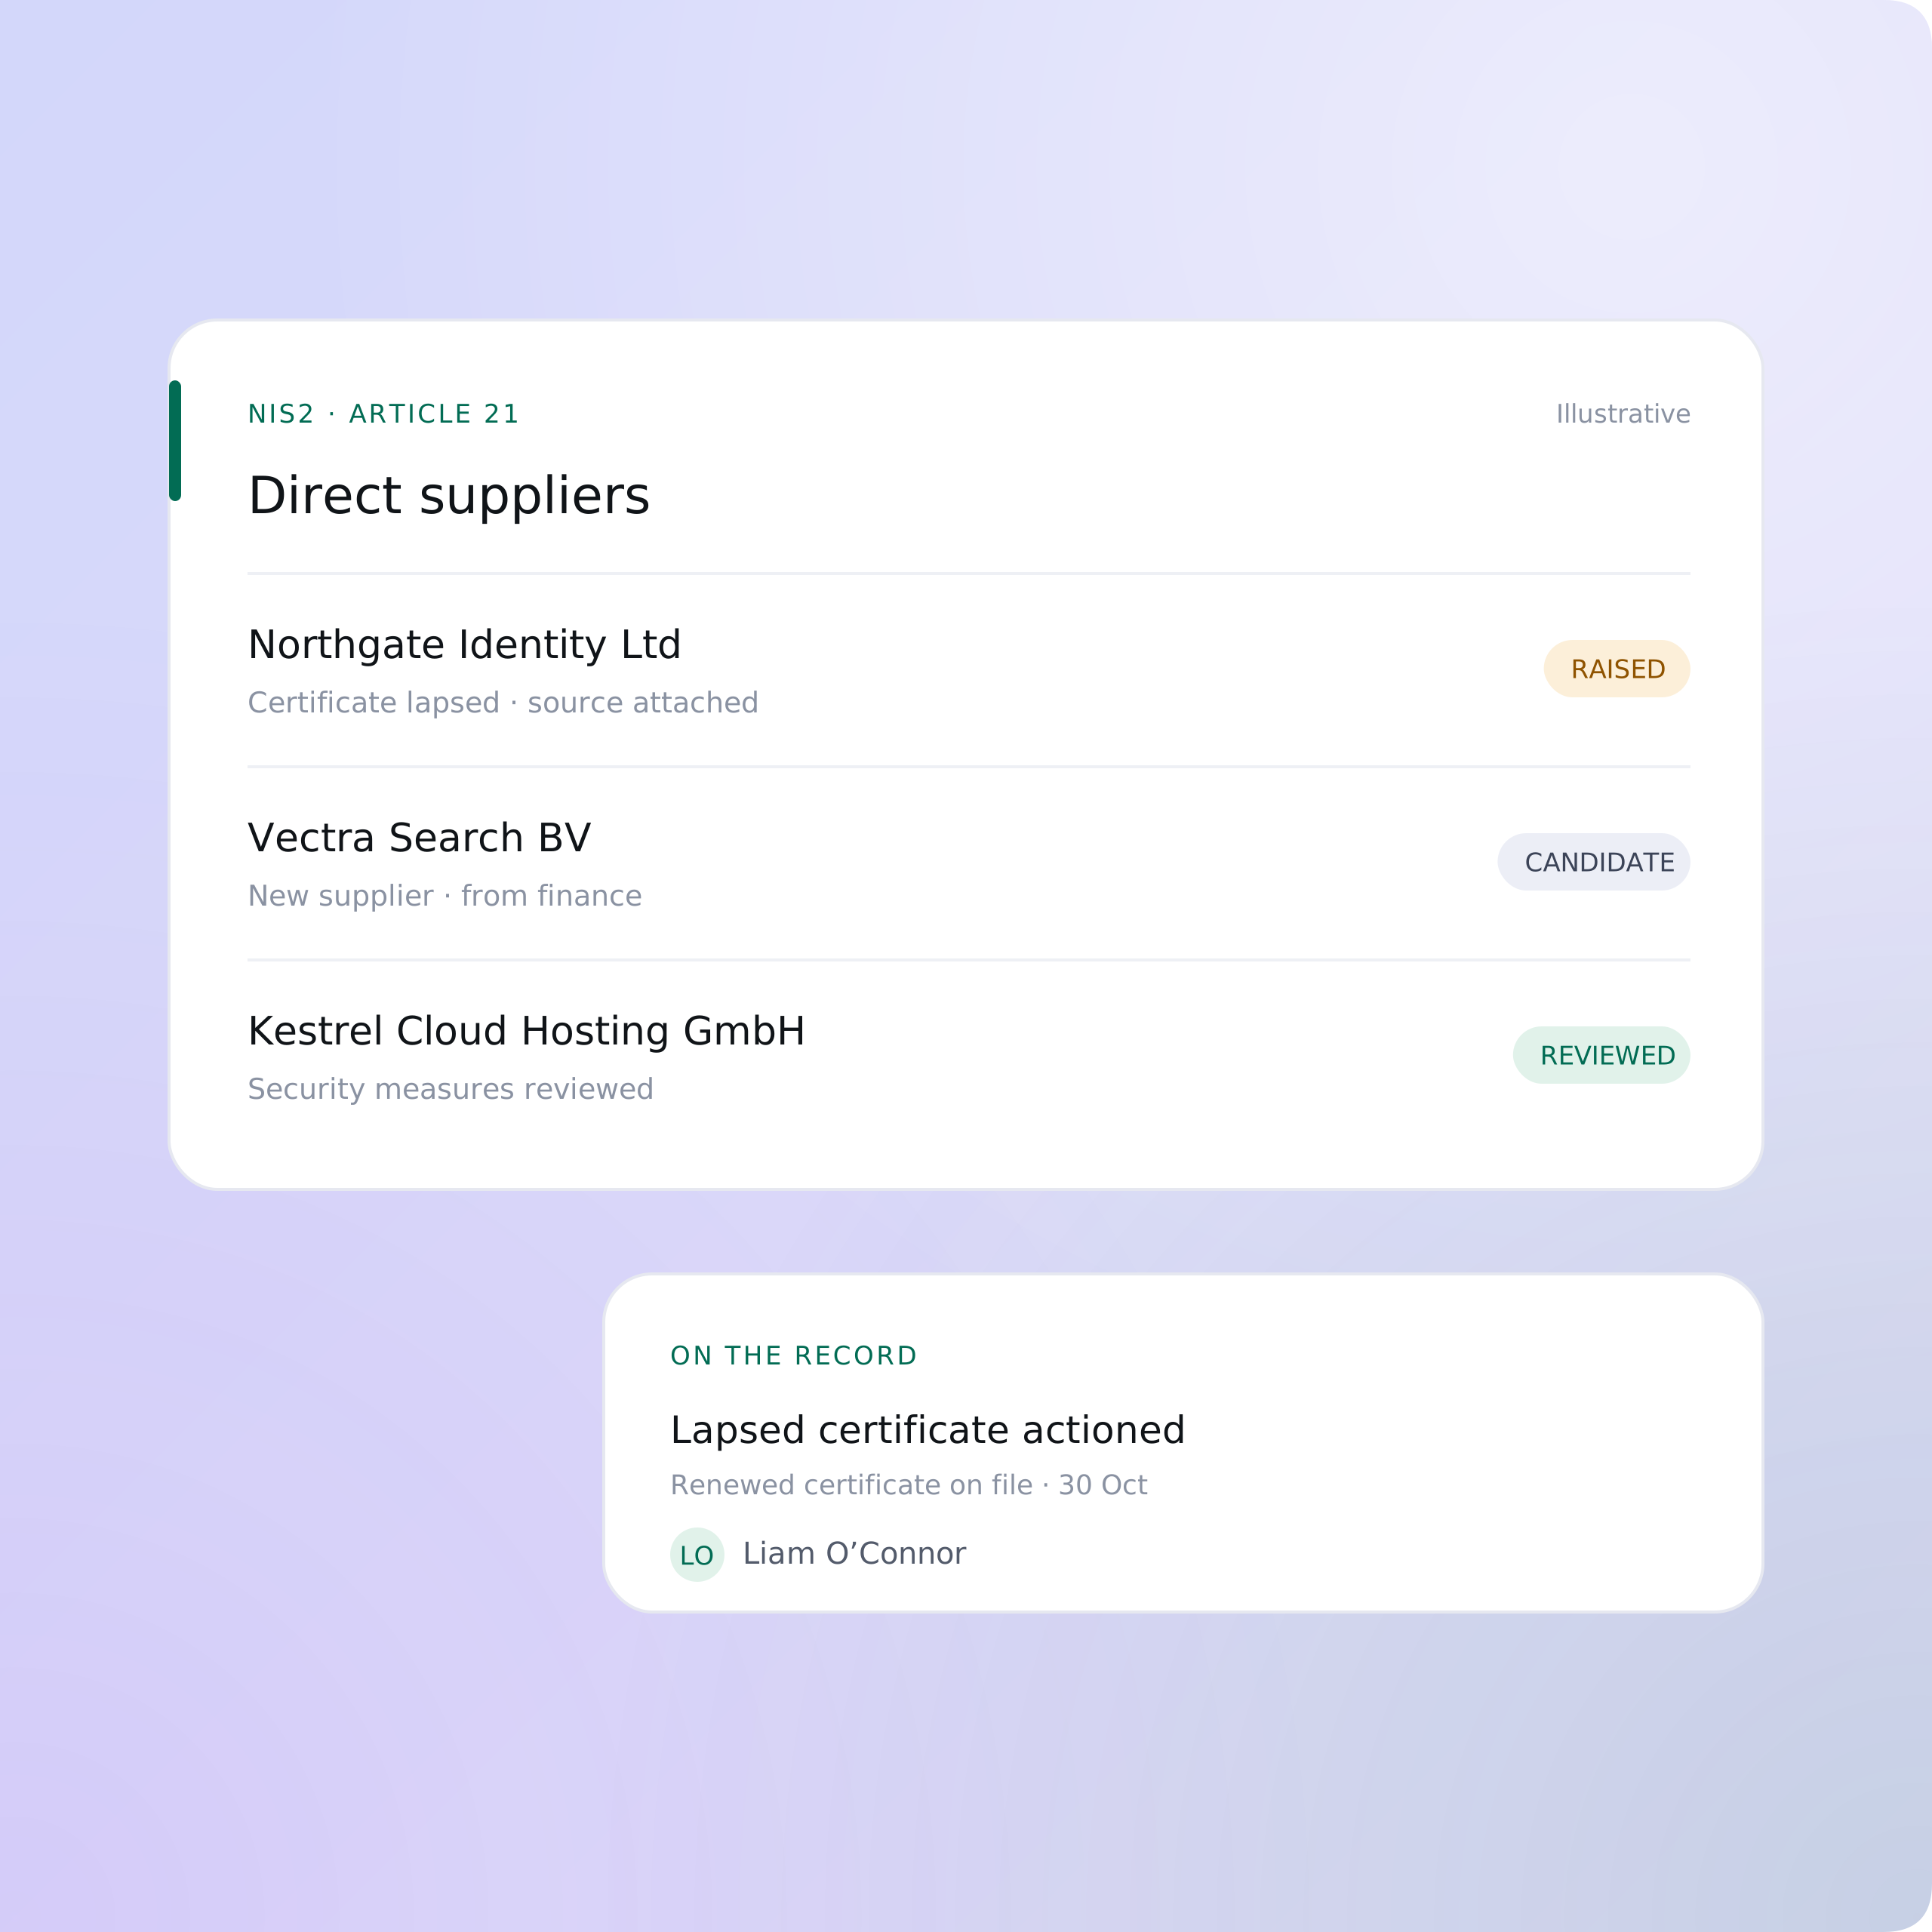
Essential and important entities keep records of their direct suppliers under Article 21. Lapsed certificates and new suppliers are raised with their source.
European
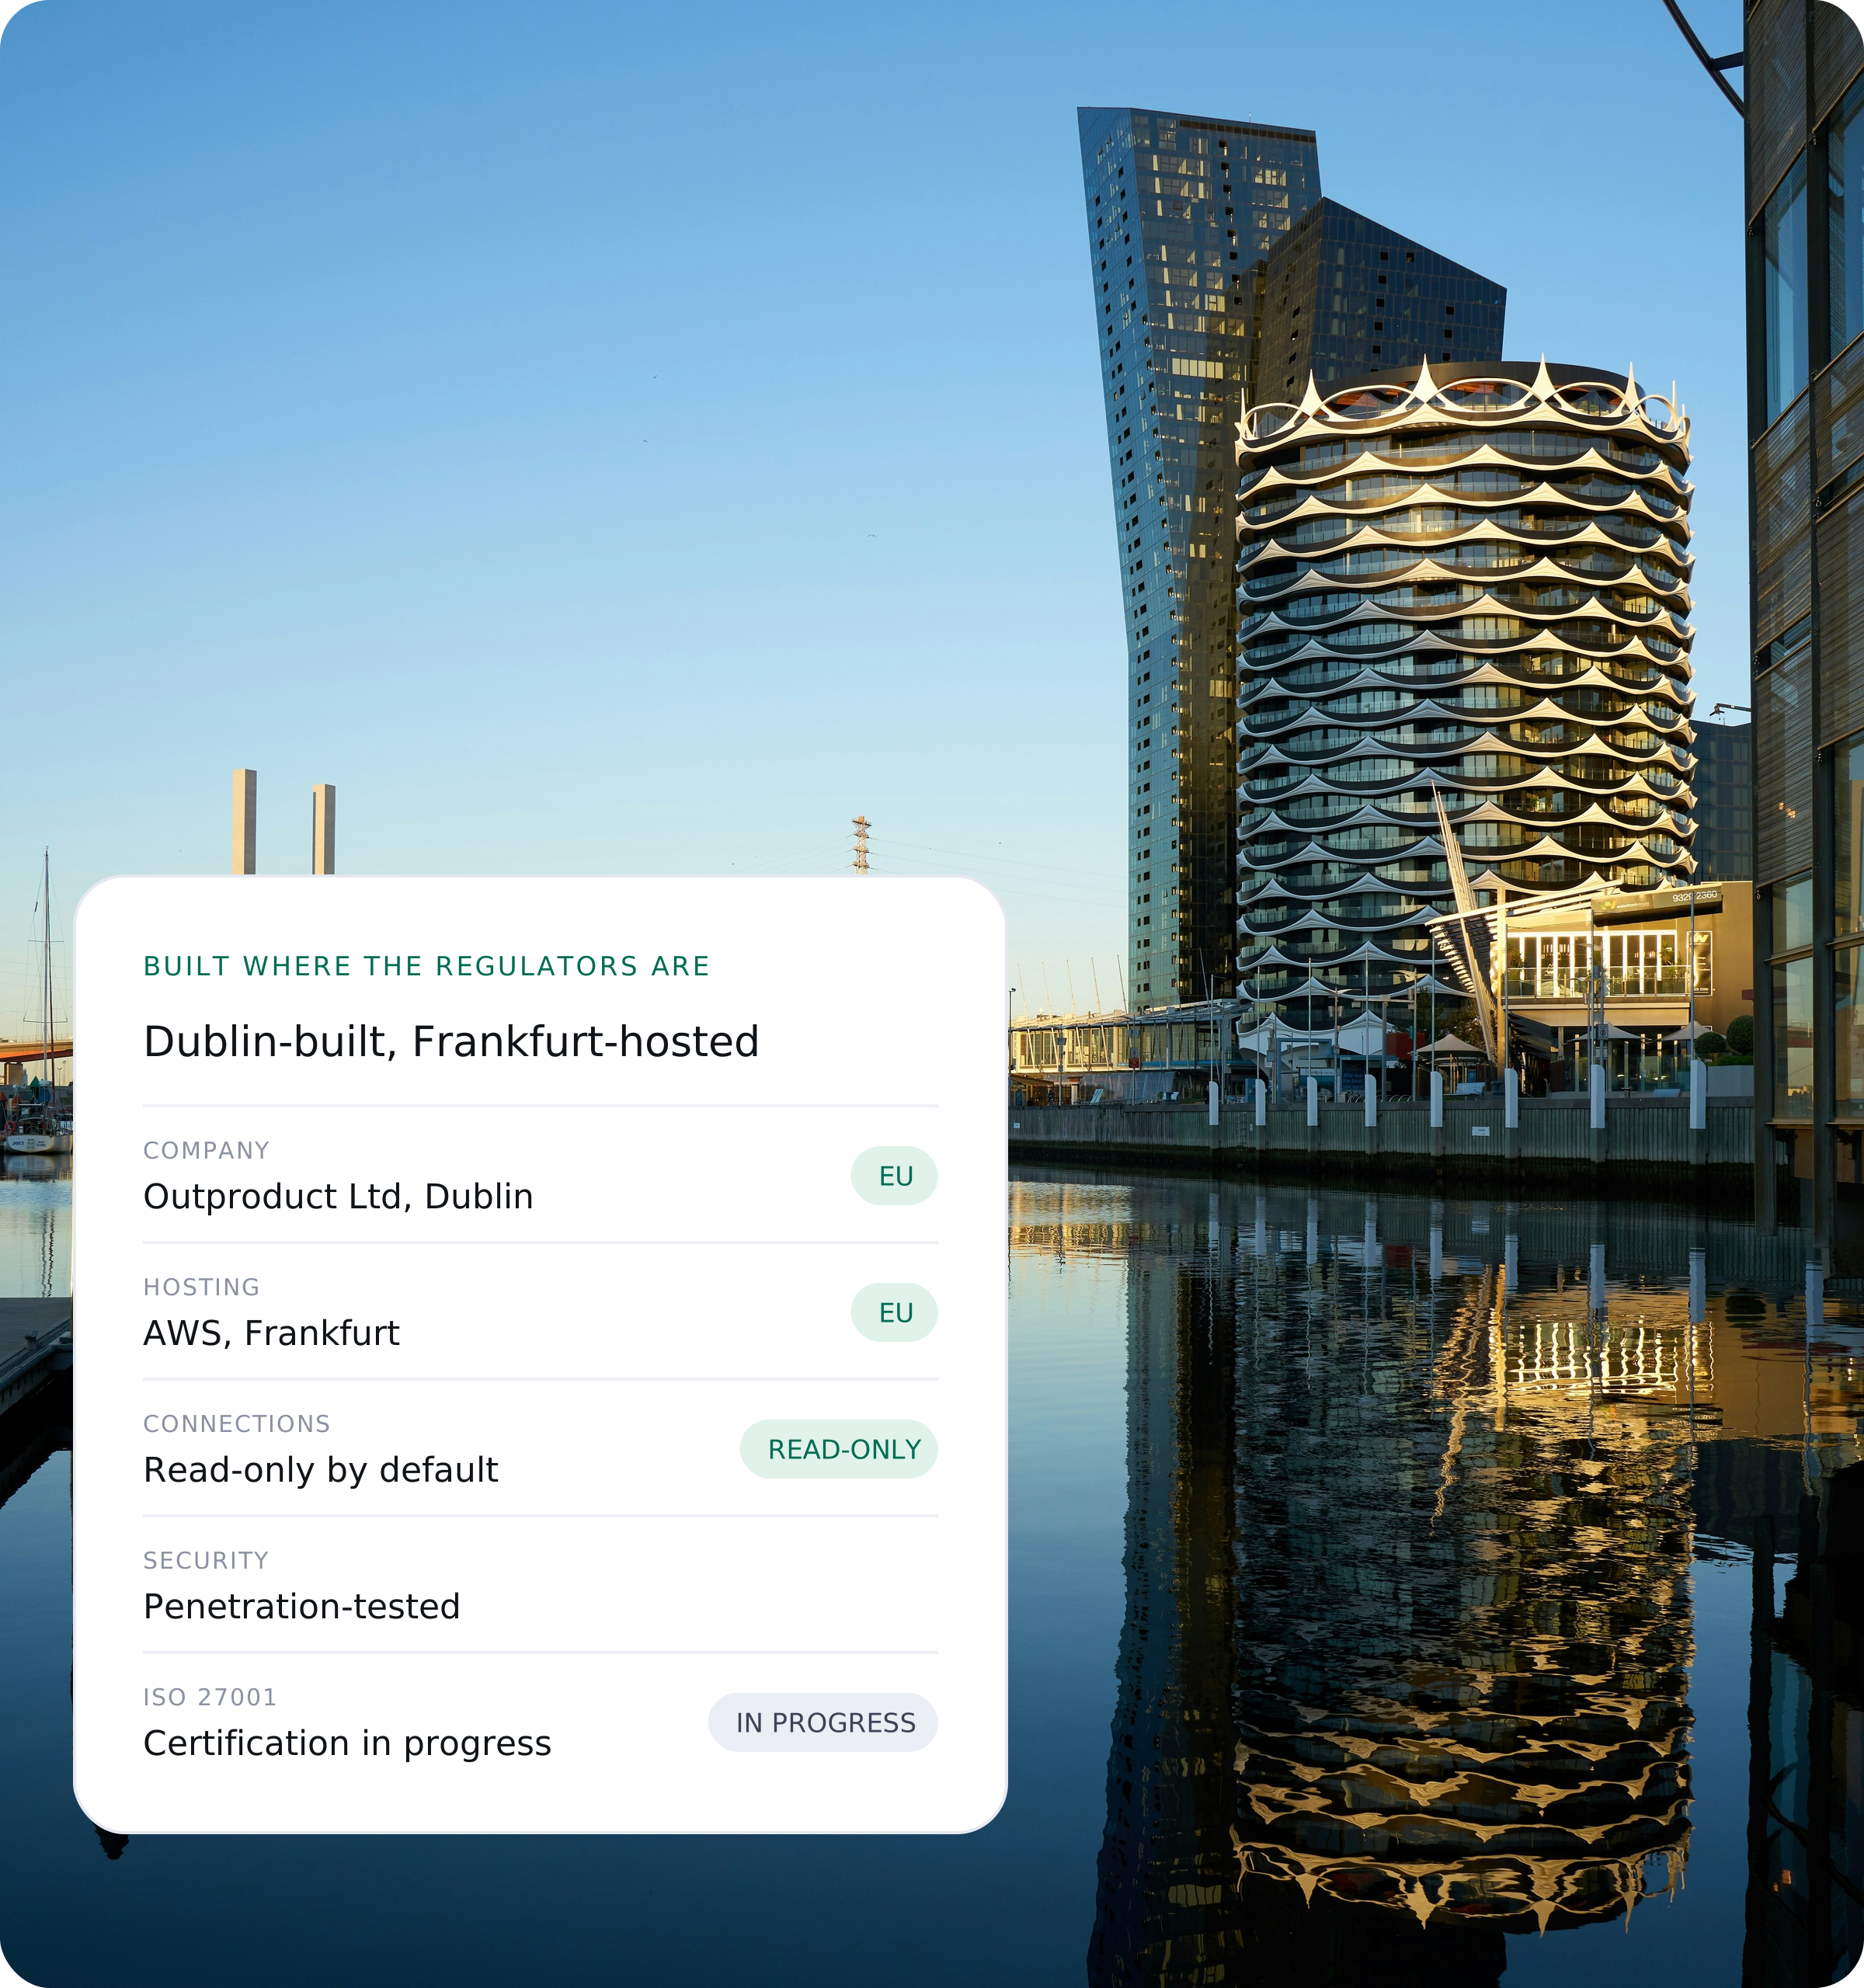
Montro is built in Dublin by Outproduct Ltd and hosted on AWS in Frankfurt. The platform is penetration-tested, and ISO 27001 certification is in progress.
On AWS in the EU. Your register and its history are held there, and connections to your systems are read-only by default.
Entries follow the registers EU and UK rules ask for, from the DORA register of information to the GDPR record of processing, rather than a generic vendor list.
Setup
A proof of concept run on your real suppliers, with your team deciding at each step.
Read-only links to sign-in, directory and finance. Nothing to install unless you add the optional browser extension.
Montro proposes the suppliers and AI tools it finds, each with its source. Your team confirms which ones belong.
Accepted entries feed the registers that apply to you, and supplier changes start coming through for review.
You’ve seen the registers built from your own suppliers, and you decide whether to continue.
Outcome
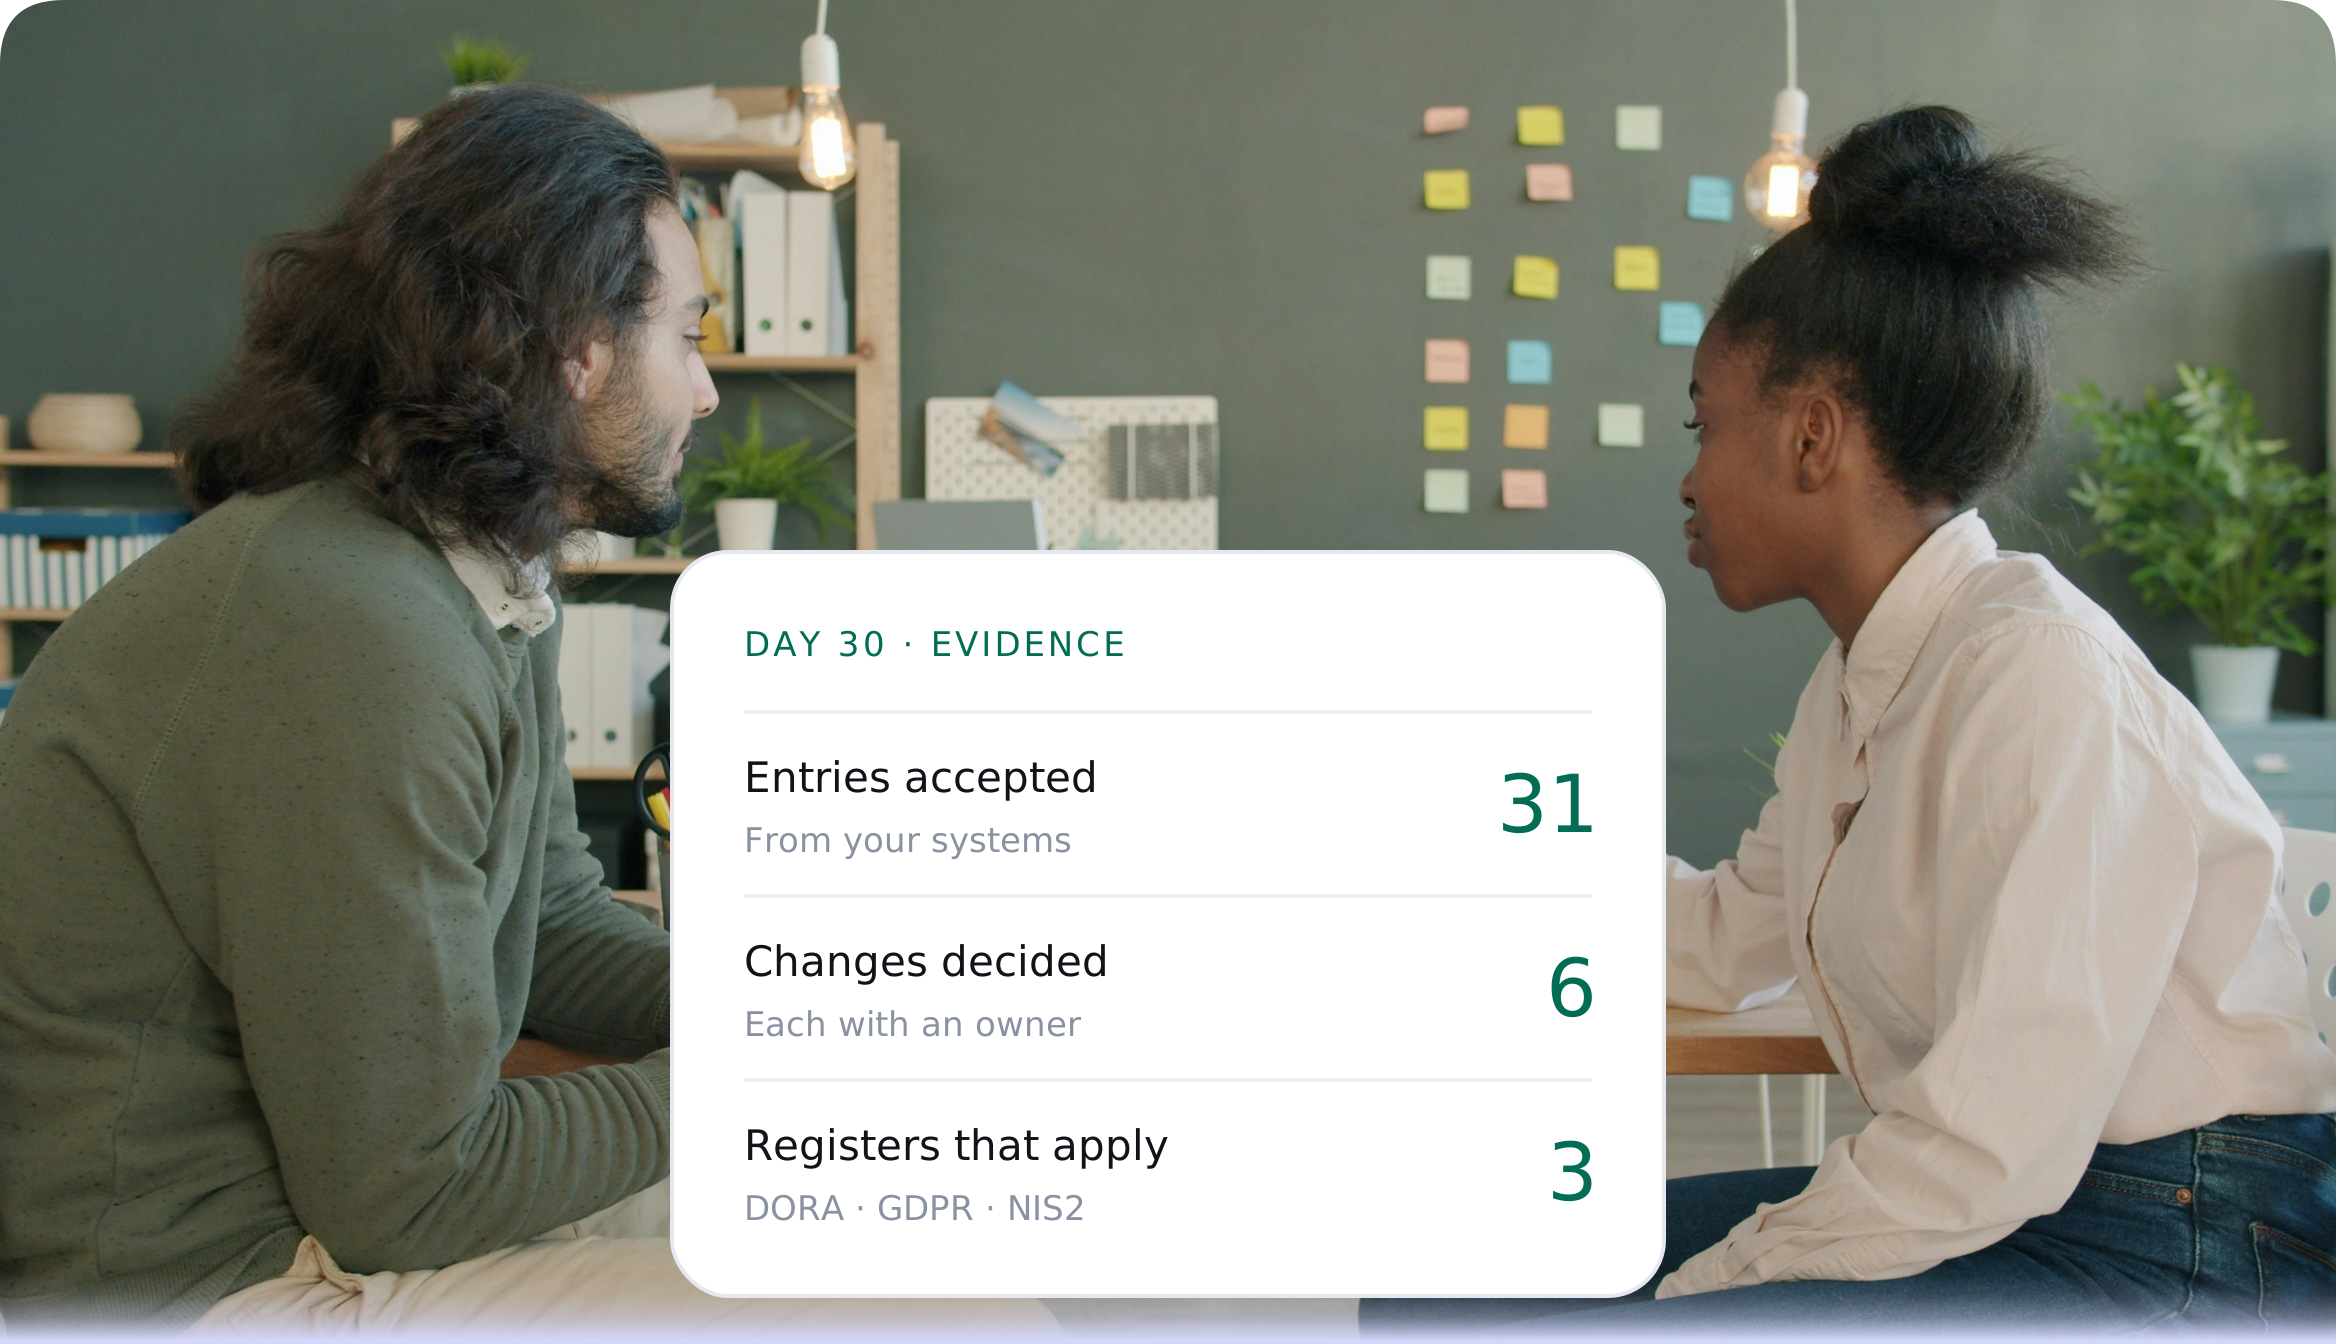
By day 30 the registers already reflect real decisions, so the choice to continue rests on what you’ve seen.
Which rules apply, working across borders, and what you share with regulators.
Third-party records are becoming decision logs. The firms that get this right will be the ones that can show who decided, on what evidence, and when.
A read-only connection, about an hour to set up, and a named person who can say yes to a decision.
Priced to scope — never per seat, never per supplier. Upgrade only when the evidence earns it.