NIS2 vs the Original NIS Directive: What Actually Changed
Organisations that were comfortably outside the original NIS Directive keep discovering they are squarely inside its successor. That is the single most important thing to understa…
Compliance strategy and regulatory guidance written by practitioners
Articles
Regulatory guidance and compliance strategy from those doing the work

Organisations that were comfortably outside the original NIS Directive keep discovering they are squarely inside its successor. That is the single most important thing to understa…

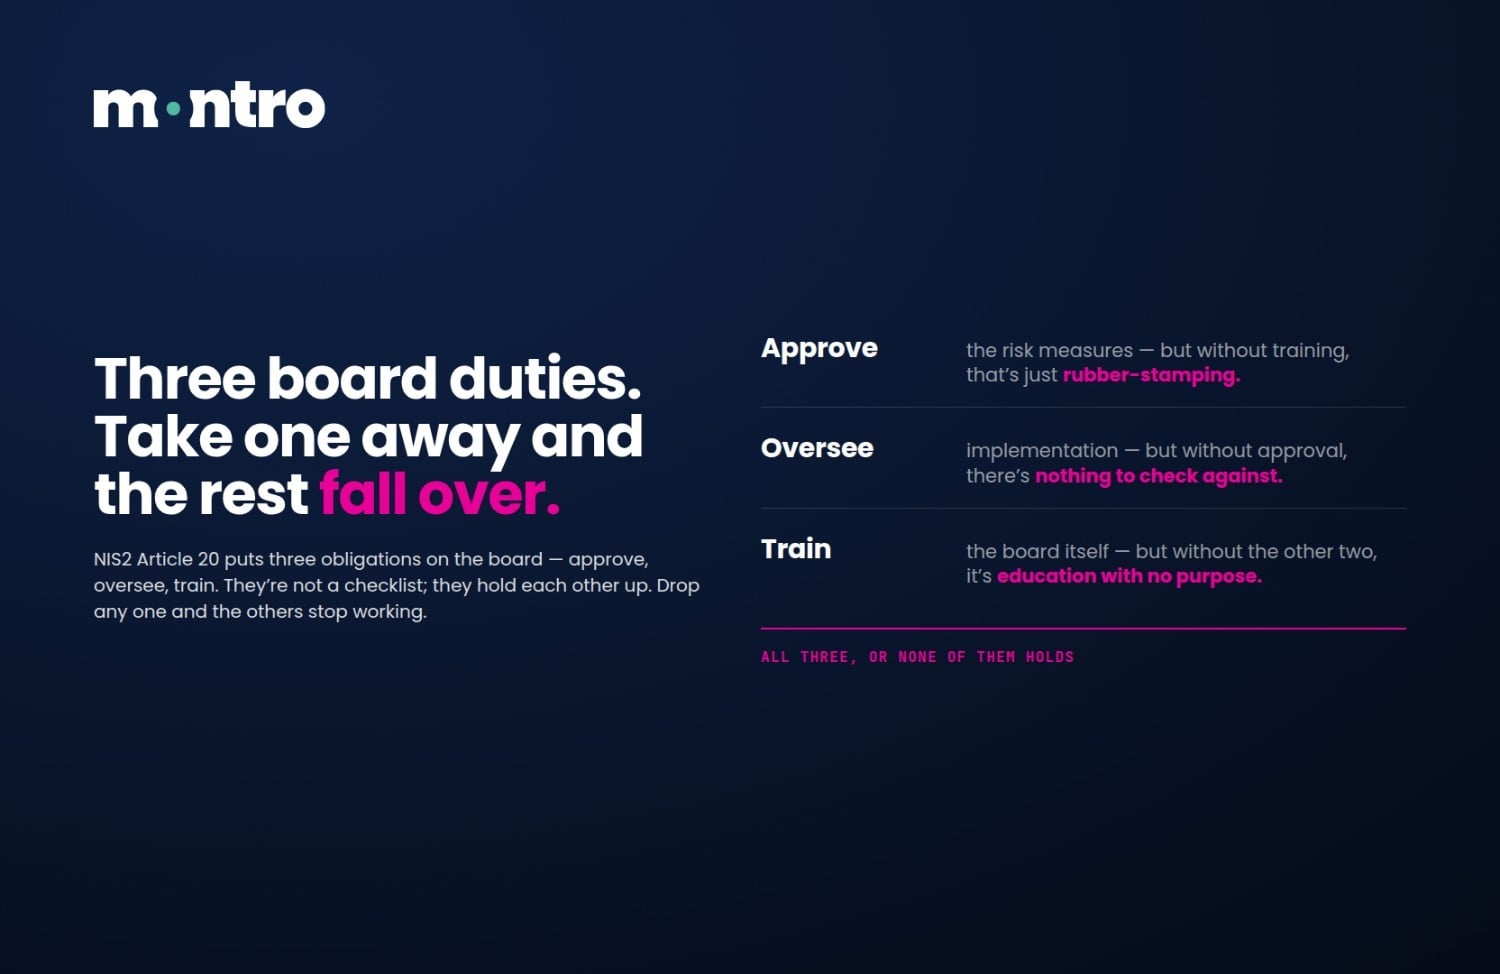
director who has been warned they can now be held personally liable for cyber failure usually asks the wrong follow-up: how bad is the liability? The more useful question sits und…

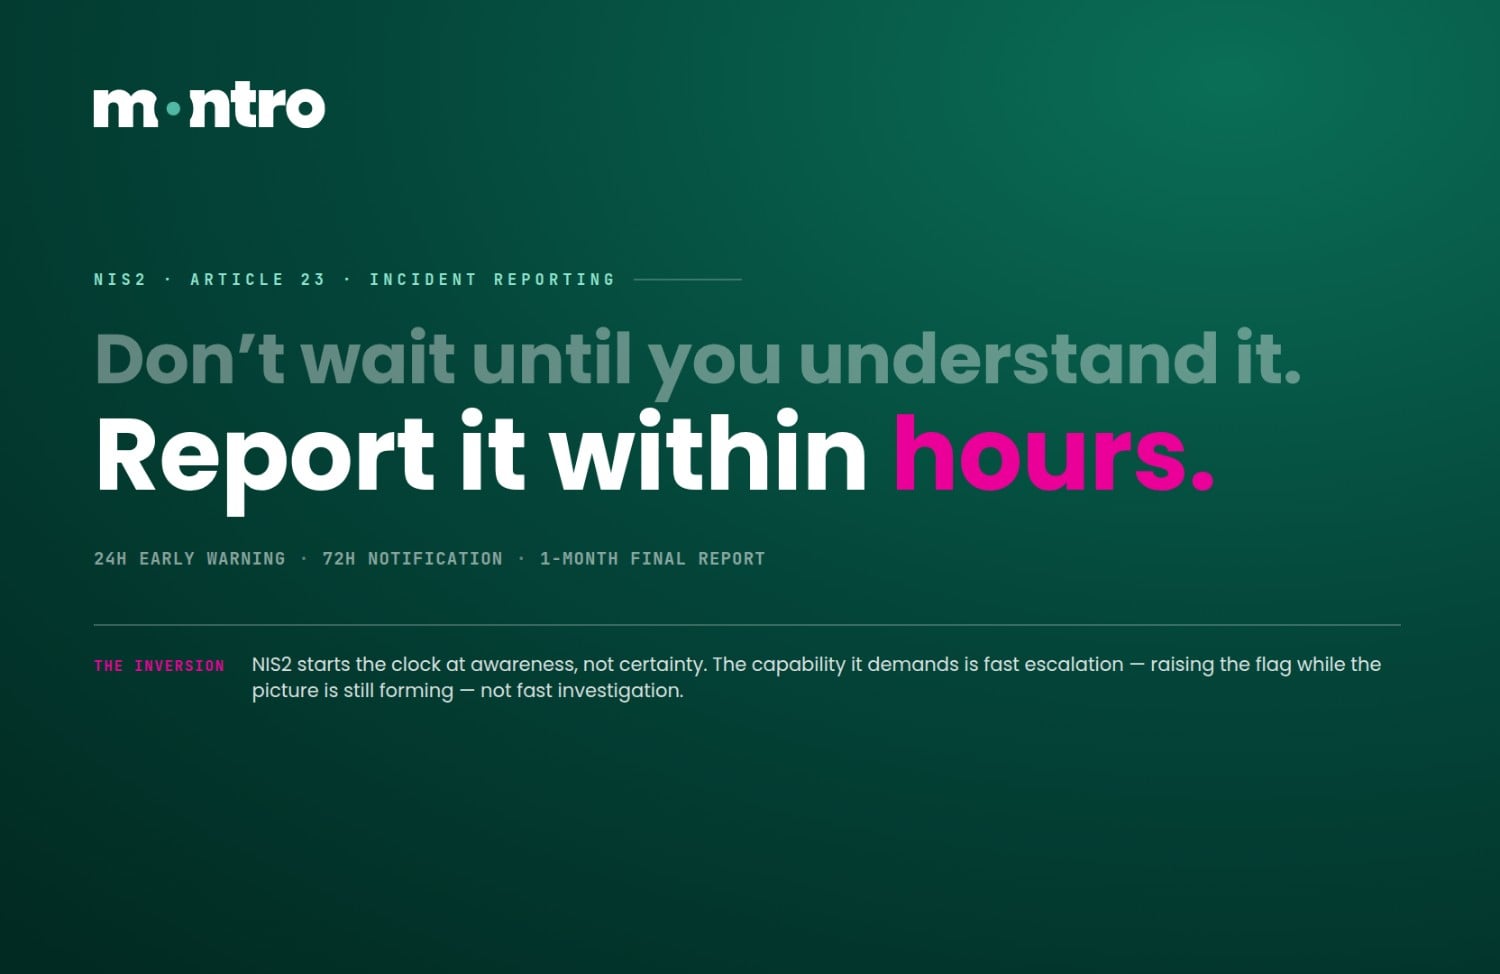
security team that has just confirmed serious incident usually assumes its first job is to understand what happened. Under NIS2 its first job is partly to tell someone - within ho…

"Comply with the directive" is the instruction security team is usually handed. In practice, most of what that means lives in single article. Article 21 is where NIS2 stops being…

company that makes components, or runs SaaS product, tends to assume cybersecurity-infrastructure rules are written for someone else - the utilities and the banks, not them. For m…

An Irish energy operator, water utility or transport network sits in an odd position right now. The cybersecurity obligations it will be held to are effectively settled, its regul…

TL;DR: NIS2 comes down to three questions. Are you in scope - and if so, are you an "essential" or an "important" entity? What does it require - chiefly the Article 21 risk-manage…

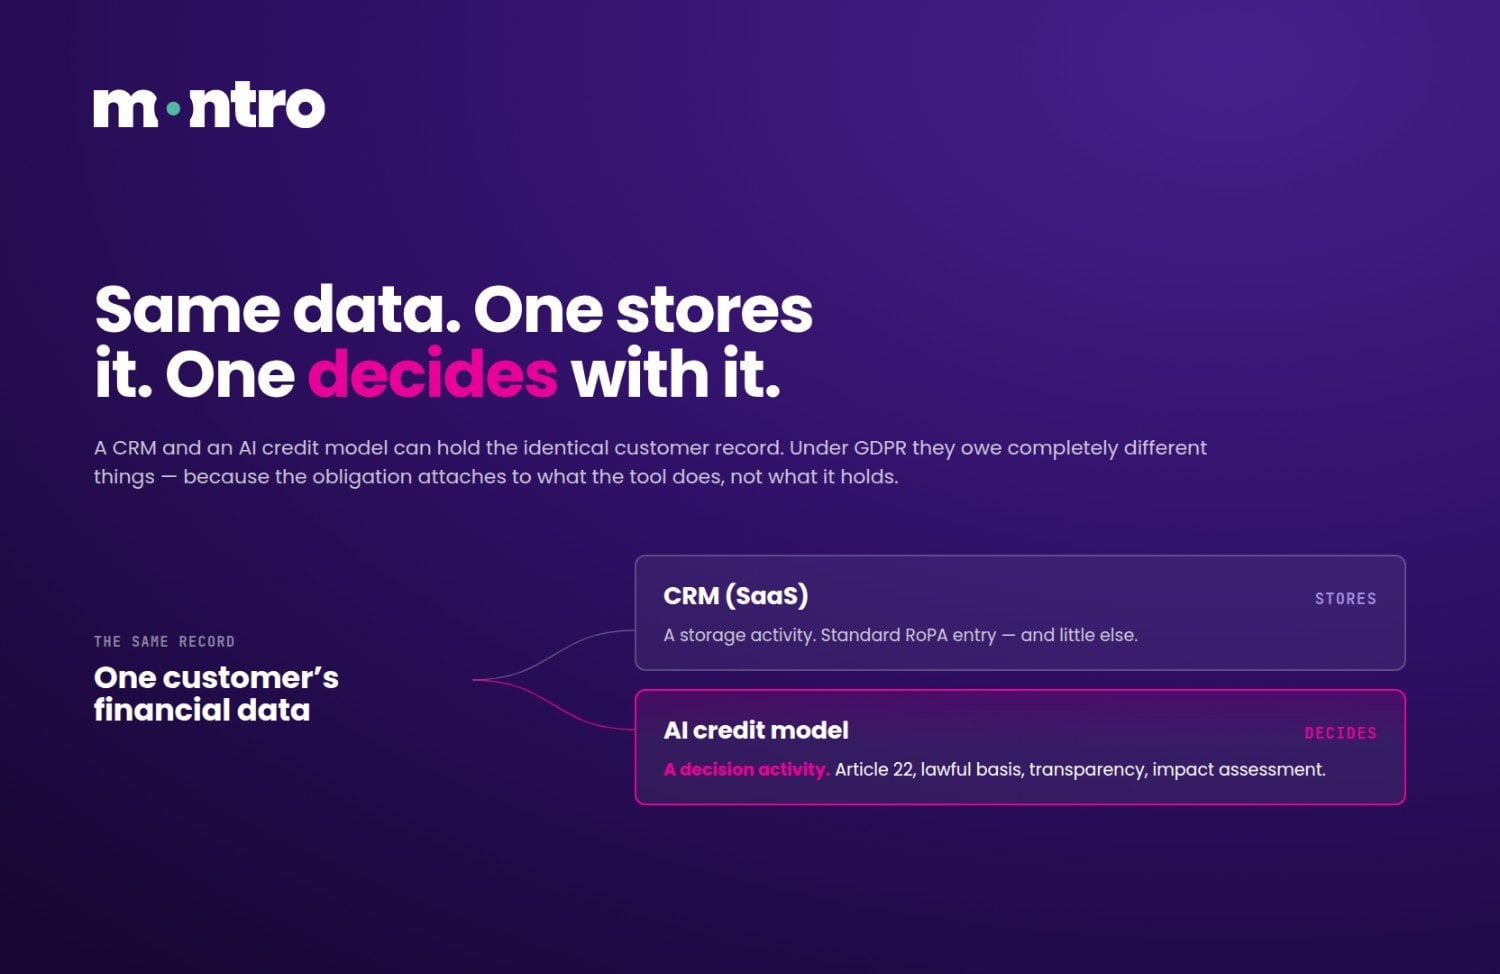
There is tidy assumption behind lot of data-protection record-keeping: tool is tool, and once you have logged what data it holds, you have done the job. Add the vendor, the data c…

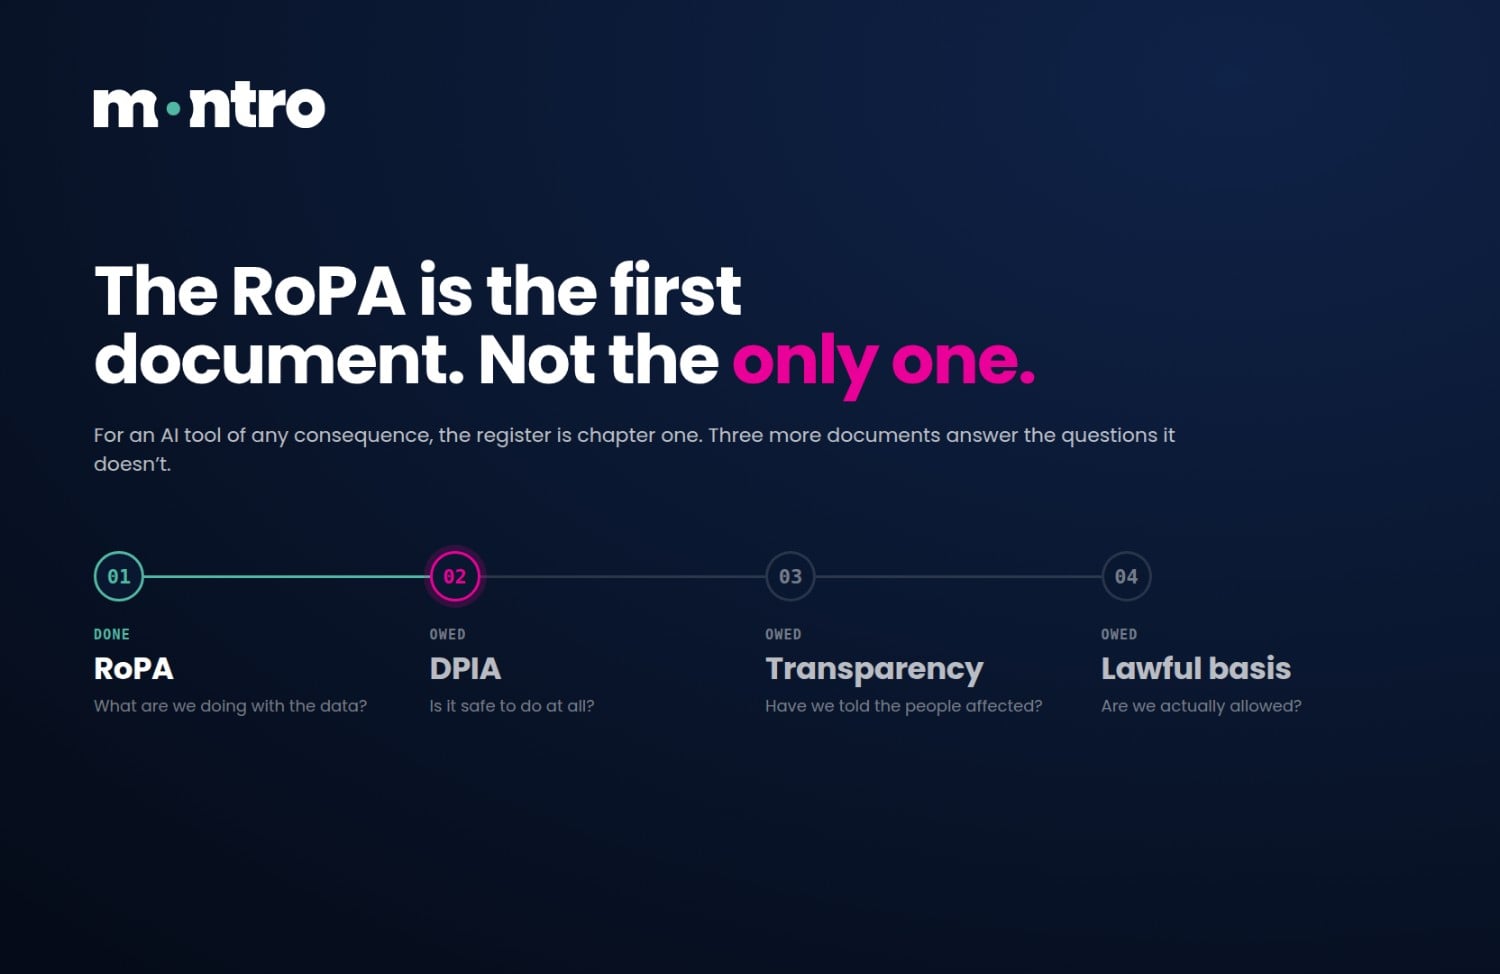
team stands up an AI tool, someone remembers it needs to go in the Record of Processing Activities, the entry gets written, and the box is ticked. The processing is documented. Ex…

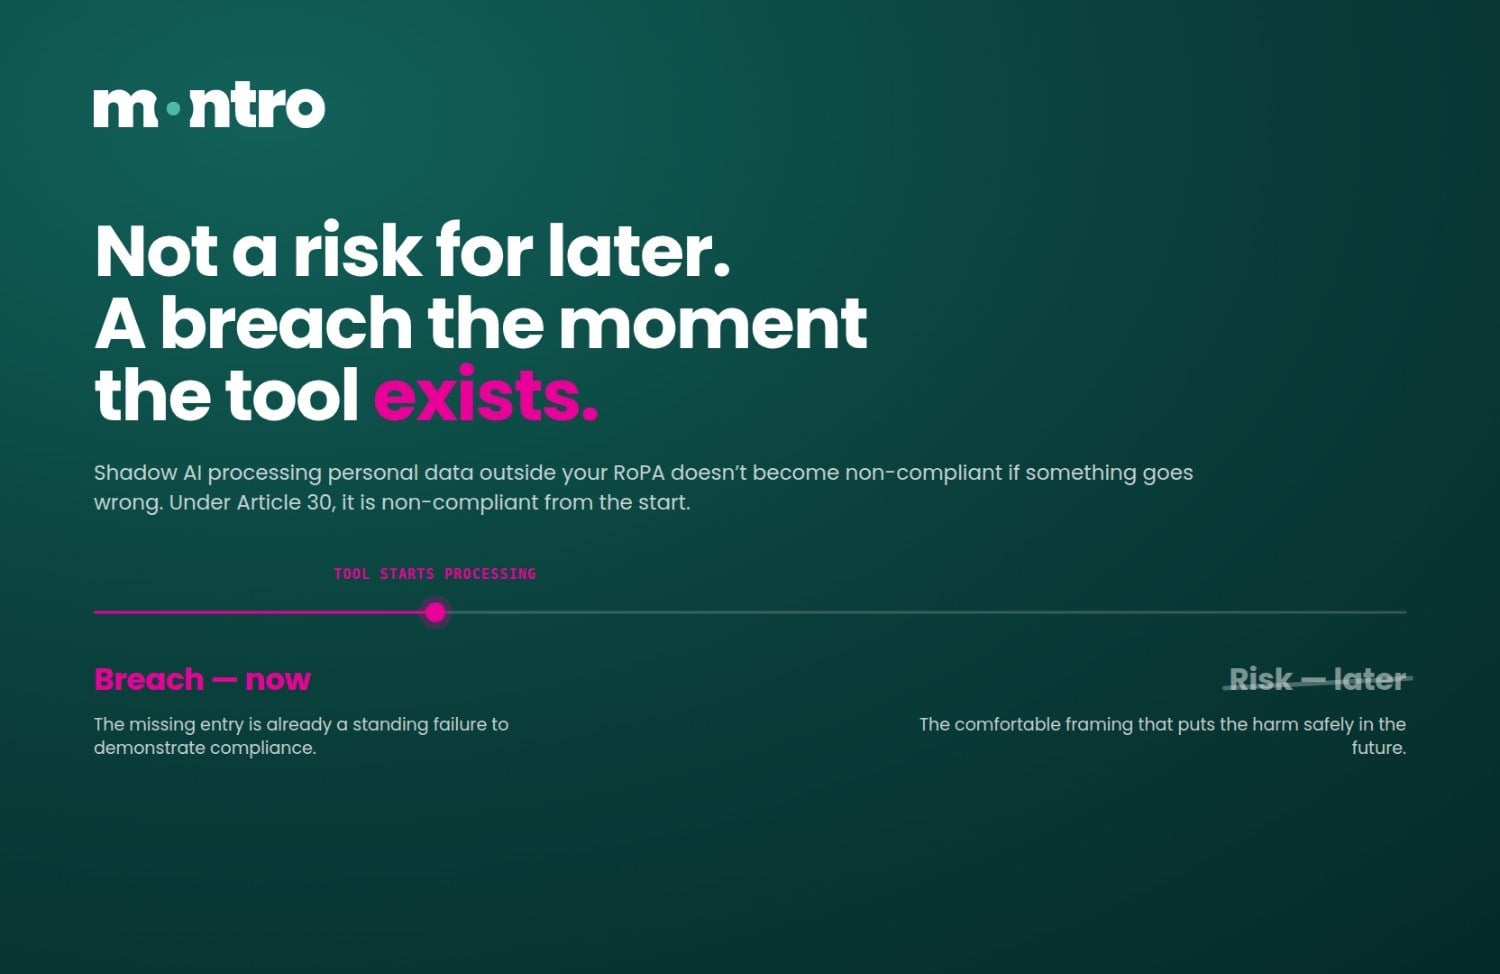
Most conversations about shadow AI treat it as risk waiting to happen - an unapproved tool that might leak data, might train on something it shouldn't, might cause problem later.…

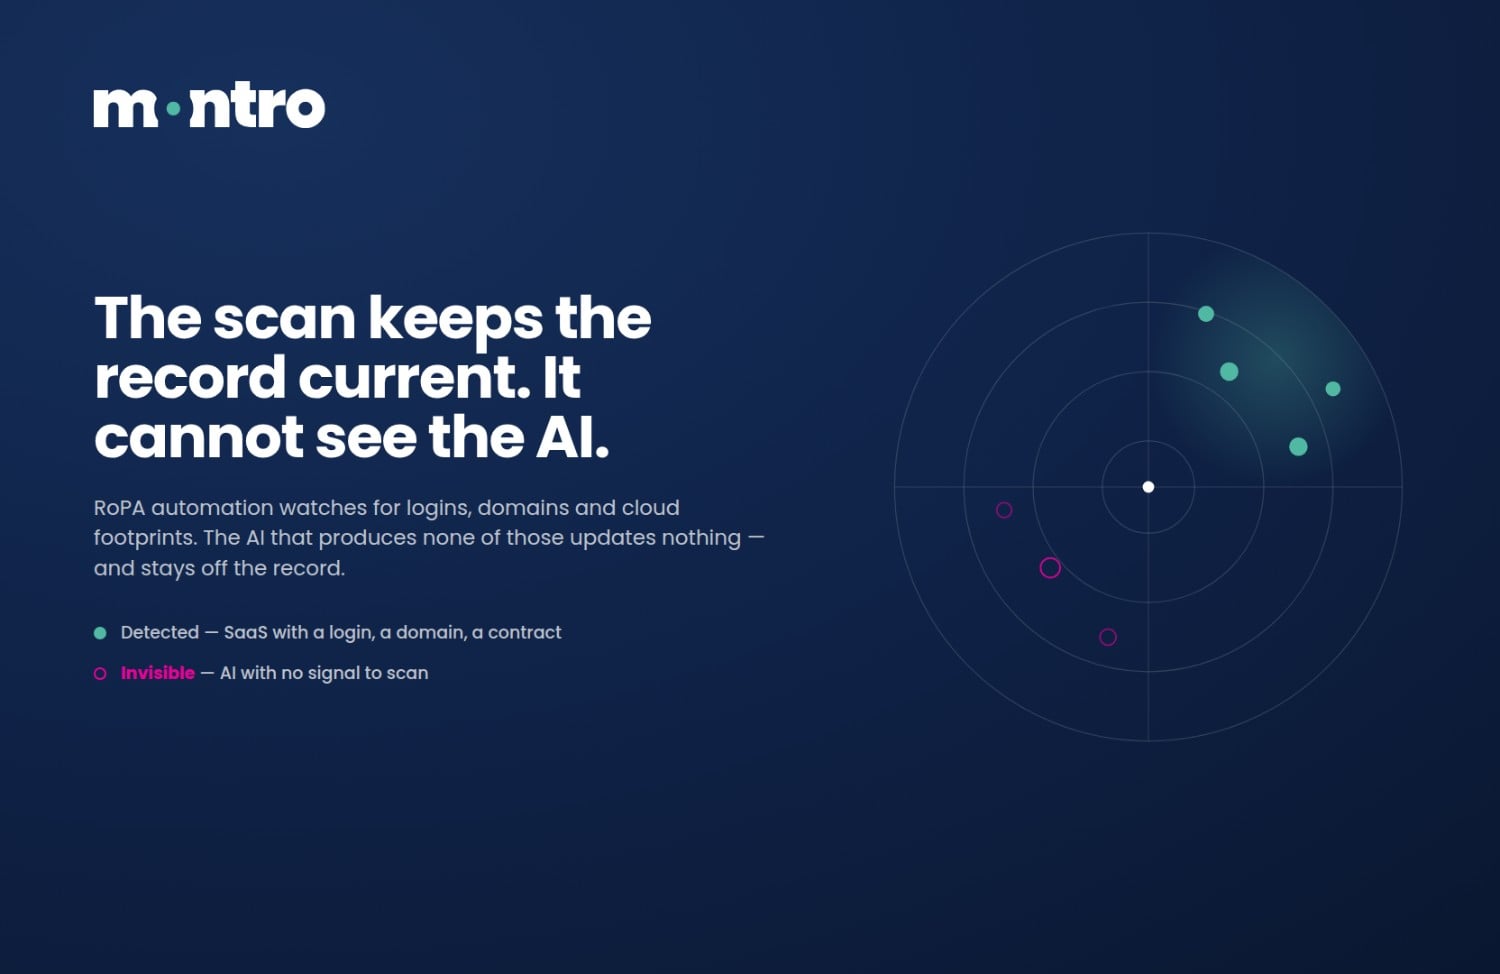
There is good reason financial firms automate their Record of Processing Activities. Maintained by hand, an Article 30 record goes stale the moment someone adds tool or reroutes d…

Three approaches to GDPR compliance under Article 30. The spreadsheet your team updates twice year. The OneTrust deployment your CFO will not approve. And third option that does t…
Find answers to common questions about our content and updates
Monthly updates on regulatory changes, compliance trends, and platform releases
By subscribing you agree to our Terms and Conditions and Privacy Policy