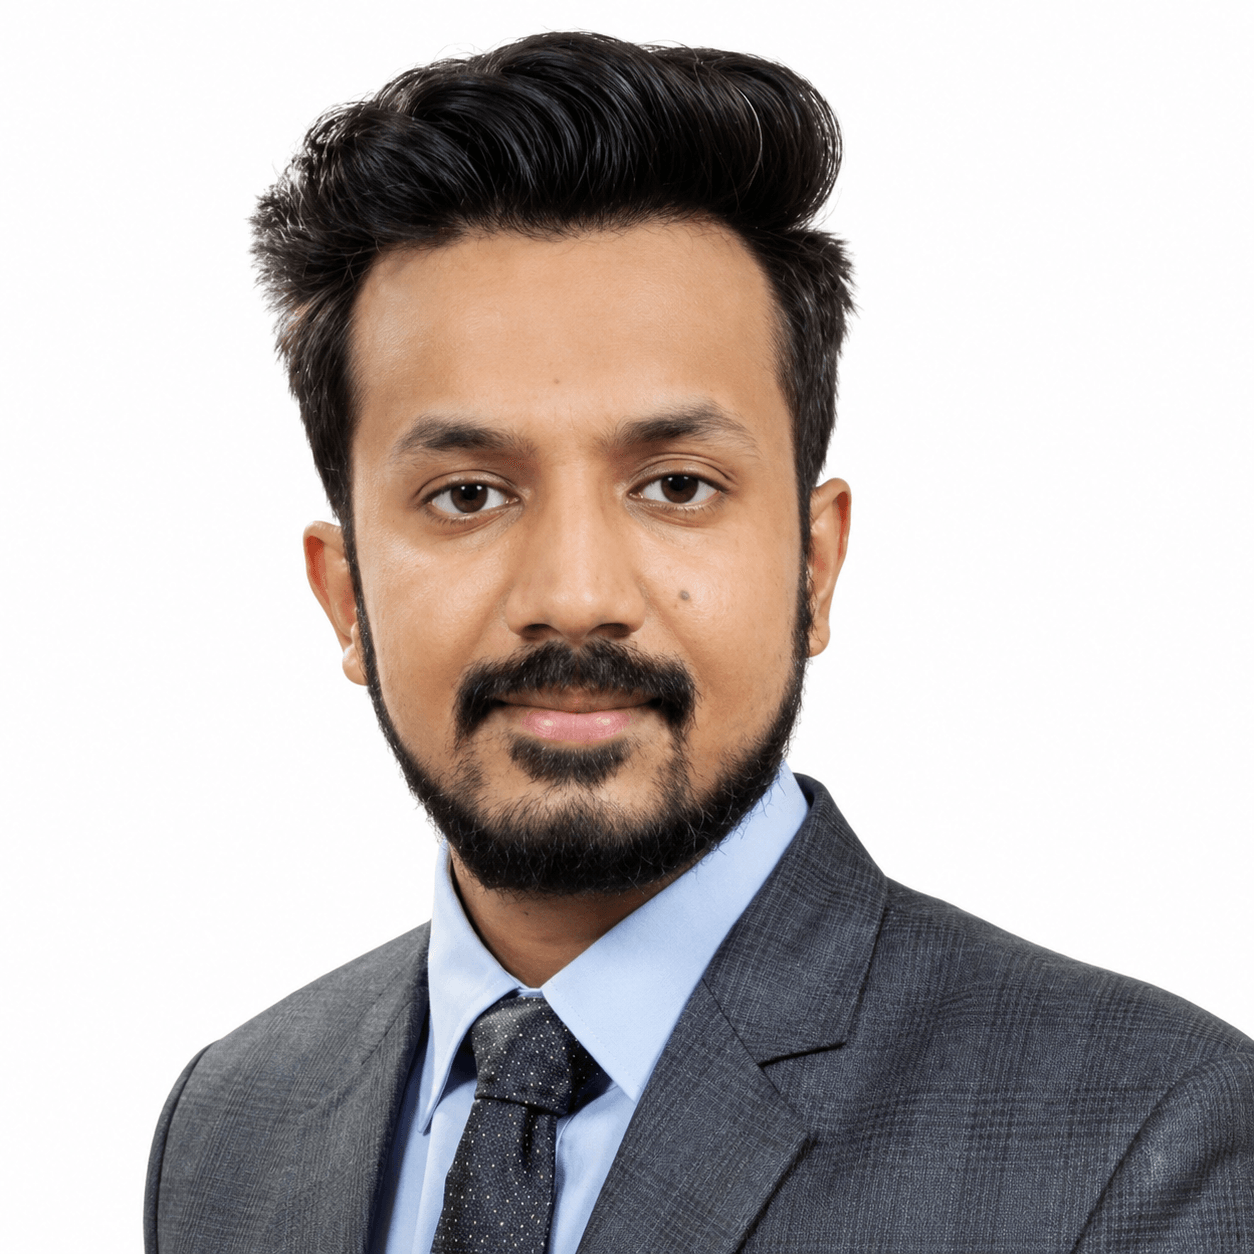
A company will tell you its data is anonymised, and on paper that's the end of it - anonymous data sits outside GDPR, box ticked. Abhishek Bansiwal's whole practice starts one question later than that. Anonymised how? Can you still single out a person? Can you match two records and pull someone back out? The document says one thing; what's actually happening in the data often says another. This conversation lives in that second question.
The gap isn't dishonesty. It's the question nobody asks.
Most organisations aren't lying when they say they're compliant, Abhishek is careful to point out. The policy does say the data's anonymised. The register is filled in. Everything has a lawful basis. The gap is that nobody asks the follow-up, to what extent? A control can be present and still be weak, and a weak control that nobody re-checks quietly stops protecting anyone.
"You cannot say 'we are compliant.' You are compliant - but to what extent? That's the question people stop asking." - Abhishek Bansiwal
The same habit, he says, is now repeating in AI governance one layer up - and arriving faster, because AI moves faster. A document declares there's a human in the loop. Fine. But as the model moves on and retrains, is that person still keeping up, or is the oversight now a line in a policy that reality has left behind?
AI isn't a privacy law. It's a product safety law.
This is the reframe Abhishek pushes hardest, and it reorders how you think about the whole thing. People treat the EU AI Act as an extension of privacy. He argues it's closer to the CE mark on a kettle or a medical device, a product safety regime that asks whether a thing is safe to build, sell and put in front of people. An AI screening job applications is a product with consequences, not a privacy clause. Which means a data protection officer who only knows privacy law isn't automatically equipped to govern it. It's a different discipline wearing a familiar name.
He's just as blunt about a sacred idea in privacy: that consent is the strongest lawful basis. It isn't, he says. Consent bends to circumstance. An employee handed a work phone that tracks them won't say no - not because they agree, but because they want to keep their job. A signature isn't proof that a choice was free.
Privacy has to see the roadmap, not the release
Ask Abhishek where privacy-by-design breaks, and his answer is that by the time engineering starts, it's usually already broken, the requirement was set before anyone asked the right questions. Engineers build what they were told to build. If privacy wasn't in the brief, it won't be in the product, and bolting it on afterwards leaves you two bad options: ship it, or delay it. Delay never wins.
Which brings him to the one thing he'd tell a leader to change: the question they ask. Stop asking the team "are we compliant?" - they're reading the same document you are, and the answer will always be yes. Start asking "so what?" You have a policy - so what's changed since? You have human oversight, so can that person actually say no? Pick one line from the privacy documentation and ask someone to show you what's really happening behind it. Not an audit. One line. It tells you more than the quarterly report ever will.
The risk was never the policy. It's the second question the policy quietly talks you out of asking.